
Choosing a Cloud Load Balancer: Match Scope and Transport to the Traffic
A practical L4/L7 decision guide for regional, global, proxy, and passthrough load balancing—with provider-neutral failure and health-check questions.
On this page
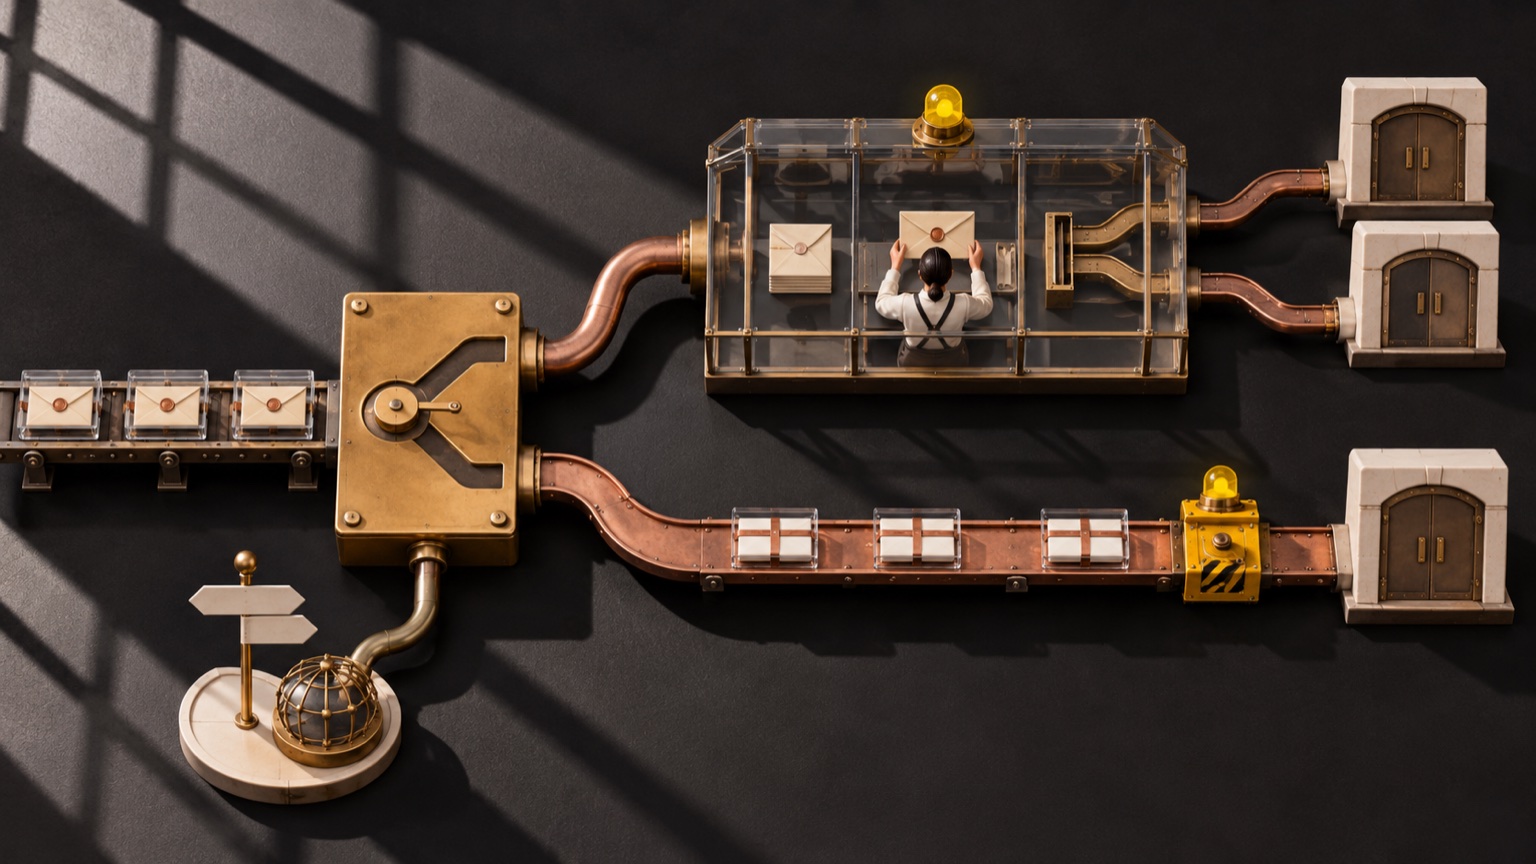
A team can select a service called a “global load balancer” and still misunderstand the packet path. Some services proxy application traffic; others choose a destination through DNS and leave the client to connect there. Within one provider, Layer 4 passthrough, Layer 4 proxy and Layer 7 application routing are also different modes. AWS, Google Cloud and Azure document distinct product families, so the workload and connection behavior should drive the choice. [1] [2] [3]
Four questions before choosing a product
1. What can the routing decision inspect?
A Layer 4 balancer works with transport or network flow properties such as IP addresses and ports. Depending on whether it is a proxy or passthrough implementation, it may terminate a transport connection or forward packets while preserving aspects of the original flow. It does not inherently know that /checkout is more important than /images.
A Layer 7 application balancer understands supported application protocols such as HTTP and HTTPS. It can commonly route by host or URL path and may terminate TLS, apply header rules or integrate with a web application firewall. The precise capabilities vary by product and mode. “L7” does not imply that every product supports every header, protocol version, WAF rule or request transformation.
2. Is traffic proxied, or only directed?
A proxy accepts a connection and creates or forwards another connection toward a backend. This creates a control point for TLS termination, connection management and application routing, while also making the proxy part of the data path. A passthrough service can preserve source information or leave protocol handling to the backend, but gives the load-balancing tier less application context.
DNS-based global steering is different again. A DNS service returns an address or hostname based on its policy; after resolution, the client connects to that endpoint. DNS caching, resolver behavior and existing connections affect how quickly clients observe changes. It is not a per-request reverse proxy. Azure’s own comparison distinguishes DNS routing from global HTTP proxying. [3]
3. What is the routing scope?
A regional frontend distributes traffic to targets inside a region or network boundary. A global application frontend can route toward backends in multiple regions, but global scope does not automatically mean every product supports arbitrary protocols, private origins or the same failover semantics. Google Cloud distinguishes global, regional, external and internal variants across application and network load balancers. [2]
4. What should count as healthy?
A TCP port accepting a connection is not the same as an application being able to serve a real request. A shallow HTTP probe may miss a failed database or an overloaded downstream dependency; an overly deep probe can mark every target unhealthy during a shared dependency outage. Define probe path, expected response, interval, failure threshold and recovery behavior alongside the application SLO.
A workload-first selection table
| Traffic need | Capability to evaluate | Operational question |
|---|---|---|
| Raw TCP or UDP service | L4 proxy or passthrough | Must the backend see the original client address? |
| HTTP path/host routing | L7 application proxy | Where does TLS terminate, and which protocols reach the backend? |
| Global web entry | Global L7 proxy/CDN or DNS steering | Does the service proxy requests or return DNS answers? |
| Internal service traffic | Internal regional/cross-region balancer | Which VPC or private network can reach its frontend? |
| Network appliance fleet | Gateway/appliance-oriented balancer | What encapsulation and flow affinity does the appliance require? |
Cloud provider terminology varies. AWS describes Application, Network and Gateway Load Balancers; Google Cloud separates Application and Network families with several global/regional and proxy/passthrough modes; Azure offers services including Load Balancer, Application Gateway, Front Door and Traffic Manager. Those labels are not a portable spec. Read the current product matrix before choosing a design. [1] [2] [4]
Failure behavior belongs in the architecture
A load balancer does not create application capacity. If ten healthy frontends all depend on a saturated database, distributing requests more evenly can still produce ten queues waiting on the same bottleneck. Scale limits, per-target concurrency, backpressure, admission control and client retry budgets remain application concerns.
Connection behavior also matters. Long-lived TCP or WebSocket sessions may not move when a backend fails. A health check that removes a target affects new routing according to the service’s rules; in-flight requests and existing connections can have separate outcomes. Retries can duplicate a write unless the operation is idempotent or protected by an idempotency key. For the same reason, avoid treating a fast health-check flip as proof that every client has recovered.
A useful architecture review draws the complete path: DNS, global entry, regional entry, service proxy, workload and dependencies. For each hop, write down protocol, TLS ownership, source-IP visibility, health signals, connection lifetime, retry owner and expected failure response. The related API gateway boundary guide explains why authentication and business-aware request policy may belong at a different layer from traffic distribution.
Do
- Select by protocol, routing information, scope and source-address requirements.
- Test health-check and connection-draining behavior with the backend failure you expect.
- Verify current provider-specific limits and DNS/proxy semantics in the chosen product mode.
Don't
- Do not assume all “global” services proxy traffic or all Layer 4 services preserve source IP.
- Do not treat a passing health probe as proof that the full user journey works.
- Do not retry non-idempotent requests without a duplicate-action strategy.
The right load balancer is the one whose observable connection behavior matches the application’s requirements. Draw the path, establish the health contract and test the failure behavior before relying on a product name.
Frequently asked questions
When should I choose a Layer 4 instead of Layer 7 load balancer?
Choose a Layer 4 service when distribution should operate on transport or network flow information and the application does not need HTTP-aware routing. Choose Layer 7 when decisions depend on HTTP host, path, headers, or other application-layer features supported by that product.
Does global load balancing always proxy the user's connection?
No. A global service may proxy application traffic, use a network proxy, or return DNS answers that direct clients elsewhere. DNS steering does not itself carry the subsequent application connection.
What does a load balancer health check prove?
A health check proves only that a configured probe succeeded under its rules. It does not automatically prove that the entire user journey, dependencies, or writes are healthy.
Can a load balancer prevent every overload or outage?
No. It can distribute eligible traffic and stop routing to targets deemed unhealthy, but a saturated shared dependency, bad health policy, regional failure, or overload of the load-balancing tier can still affect the service.
Sources & further reading
Keep reading

Traffic Engineering at the Boundary: Load Balancers, Gateways and Reverse Proxies
How Layer 4 and Layer 7 balancers, edge API gateways, and reverse proxies coordinate to shape, authenticate, and distribute web-scale traffic.

Content Delivery Networks Demystified: Edge Caching, Origin Offload and Traffic Shaping
How CDNs route requests to distributed edge locations, cache reusable responses, reduce origin load, and manage freshness without overclaiming latency gains.

Database Sharding Guide: Horizontal Partitioning, Shard Keys, and Cross-Shard Joins
Why databases resist horizontal scaling: deep dive into database sharding, range vs hash vs directory strategies, cross-shard joins, and resharding.
/* Comments */
Comments are offline right now — we reconnect automatically, nothing is lost.