
Cursor Can Turn an Agent Prompt Into a Live App. Treat That as a Deployment Pipeline
Cursor Apps bundle code, hosting, Postgres, authentication, and sharing. The speed is useful, but teams still need ownership, access, and data reviews.
On this page
A useful internal tool often dies between “it works on my laptop” and “someone can safely use it.” Cursor’s new live-app flow tries to remove that gap by provisioning the pieces around the code as well as writing the code itself. That makes a small app easier to share—and makes deployment decisions arrive much earlier in the build process.
What Cursor is bundling
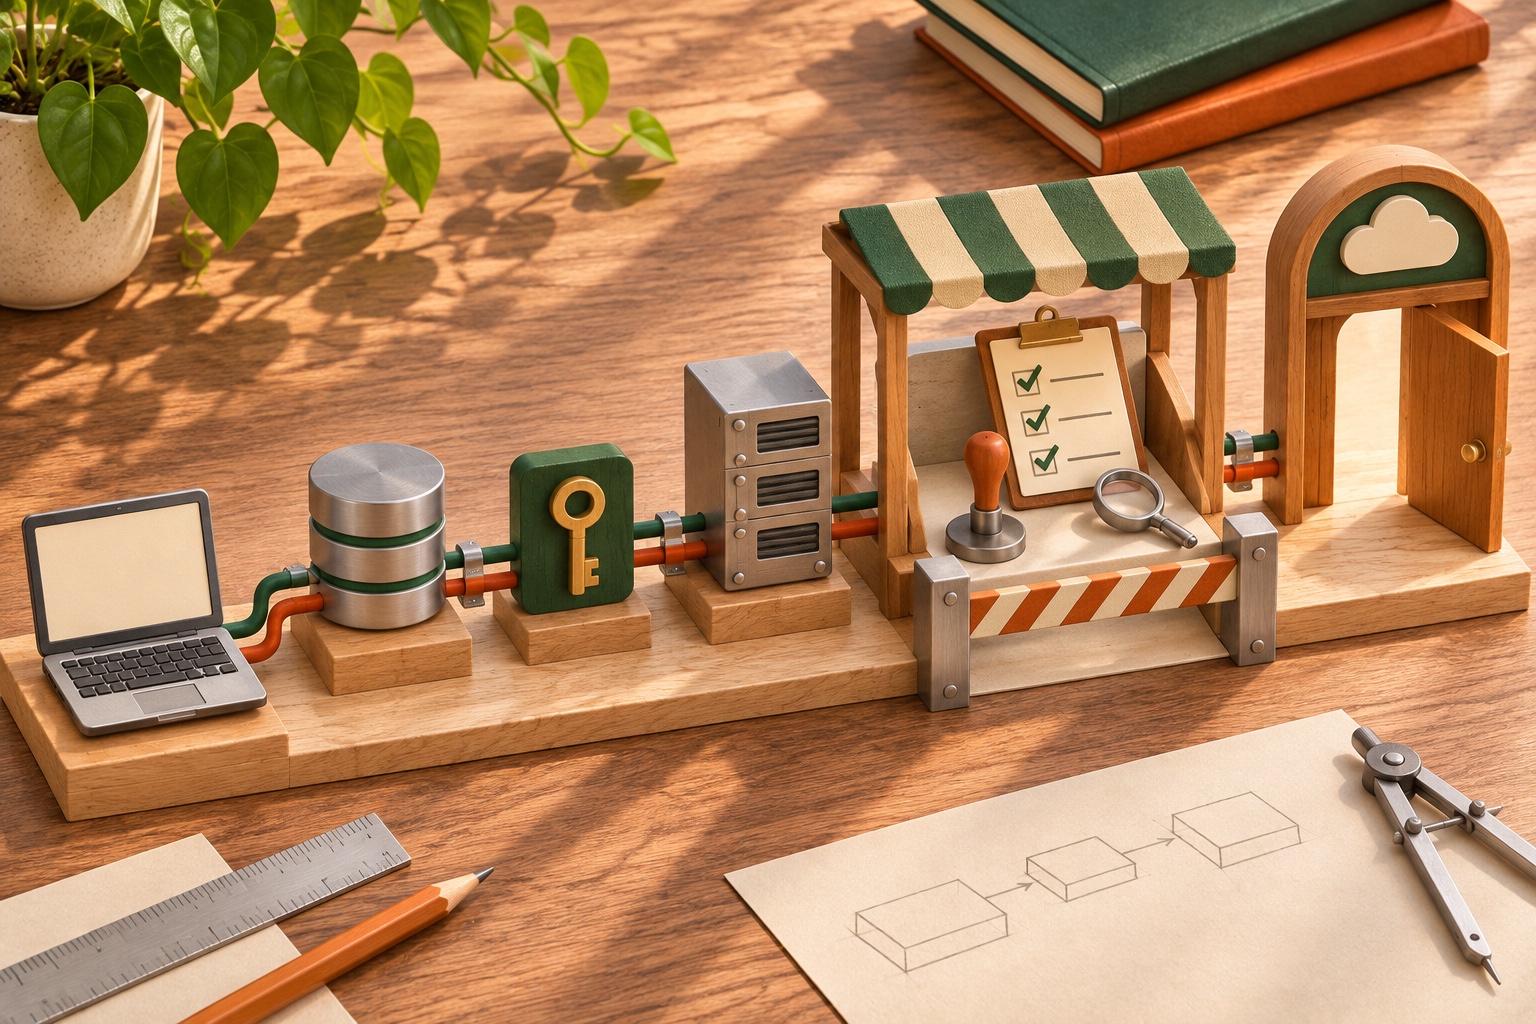
In its November 5 release, Cursor says a cloud agent can scaffold a web app, start a Postgres database if needed, configure authentication behind Cursor sign-in, provision hosting, and publish the result at a chosen domain. It supports new or existing repositories across Cursor Origin and GitHub, with other git providers described as forthcoming. The feature is available on paid plans with cloud agents enabled. [1]
The product documentation adds important details about visibility and administration. Apps can be shared with invited people, a whole team, or publicly by link. Public sharing is disabled by default for Teams and Enterprise; administrators can see team apps and secrets and can unpublish an app. Cursor says its publish flow checks for common issues such as secrets in app files and exposed credentials, and nothing goes live until the user chooses to publish. [2]
Why “publish” changes the engineering question
When a project is only local, its data may be disposable and its user list may be one developer. Once it is hosted, even a simple form can collect real information, accept authentication, or connect to internal systems. The deployment pipeline has to answer questions that code generation alone cannot: who can access each record, which credentials can the app use, who owns the domain and database, how updates are reviewed, and what happens if an integration fails?
Cursor’s checks are useful guardrails, but a passing check is not a correctness proof. A system can contain no visible API key and still expose private rows through a permissive database policy. A sign-in screen can authenticate a person while the app fails to authorize what that person may see or change. An application security standard such as OWASP ASVS is a useful source of verification requirements because it treats security as a set of properties to validate across the application, not only a pre-publish scan. [3]
A lightweight review before sharing
Name an owner. Choose the team or person responsible for the app, its repository, database, secrets, and updates. A generated tool without an owner becomes an orphaned production dependency.
Classify the data. Start with fake or low-risk data. Before connecting a warehouse or employee system, establish which fields the app needs and whether its access can be restricted to those fields and users.
Test authorization, not just login. Try the app as each intended role. Verify that users cannot read or change another person’s records by changing an identifier or URL. Confirm that a shared link has the expected audience.
Review the publish target. Check the URL, repository, environment-specific settings, database behavior, and public or team visibility before pressing publish. For a team app, verify admin controls and unpublish procedures.
Plan the next change. Confirm where the source lives, how later edits are reviewed, and who handles a bug, exposed secret, or unexpected data write. Cursor’s feature can create the first version quickly; operating it responsibly remains a team job. [1] [2]
The opportunity is a shorter feedback loop
The best use case is a small internal workflow whose owner can state its data boundaries and evaluate the result. A department can turn a repetitive spreadsheet process into a shared tool without first assembling a separate platform team. The risk is treating speed as evidence that the result is ready for every kind of data or audience.
Cursor’s launch signals a broader shift in coding agents: they are starting to create and provision deployable services, not just propose source files. Teams should welcome the shorter path from idea to working software while carrying their ordinary deployment discipline into the new interface. A generated app becomes a real app when real people and data depend on it.
Frequently asked questions
What did Cursor announce with Build Live Apps?
Cursor's November 5 release lets cloud agents scaffold an app, provision Postgres when needed, configure authentication, provision hosting, and publish to a chosen URL. Cursor says the feature is available on paid plans with cloud agents enabled.
Are Cursor-built apps automatically public?
No. Cursor's documentation describes invited-user, team, and public sharing modes. Public sharing is disabled by default for Teams and Enterprise, and the publisher must choose to publish after checks run.
Do automated security checks make a generated app production-ready?
No. Cursor says its checks catch common issues before publishing, but checks cannot establish that an app's business rules, data permissions, integrations, or privacy choices are correct for a team's actual use. Owners still need to review and operate the app.
Sources & further reading
Keep reading
Google’s Gen AI Python SDK 3.0 Changes Three Defaults. Check Before You Upgrade
Google Gen AI Python SDK 3.0 changes the API default, HTTP client and one result type. Here is what Gemini developers should check before upgrading.
GitHub Adds an Addressed Rate for Copilot Reviews. What It Measures
GitHub’s new repository metrics count how teams respond to Copilot review comments, but an addressed comment is not proof that the advice was correct.
GitHub’s ACCESSIBILITY.md Gives Projects a Place to Explain the Gaps
GitHub makes accessibility statements easier to find. The useful file explains known barriers, tests, reporting routes, and who will maintain it.
/* Comments */
Comments are offline right now — we reconnect automatically, nothing is lost.