
Docker vs Kubernetes: Where Container Packaging Ends and Orchestration Begins
Docker builds, distributes, and runs container images; Kubernetes reconciles workloads across a cluster. The tools overlap in a workflow, not in purpose.
On this page
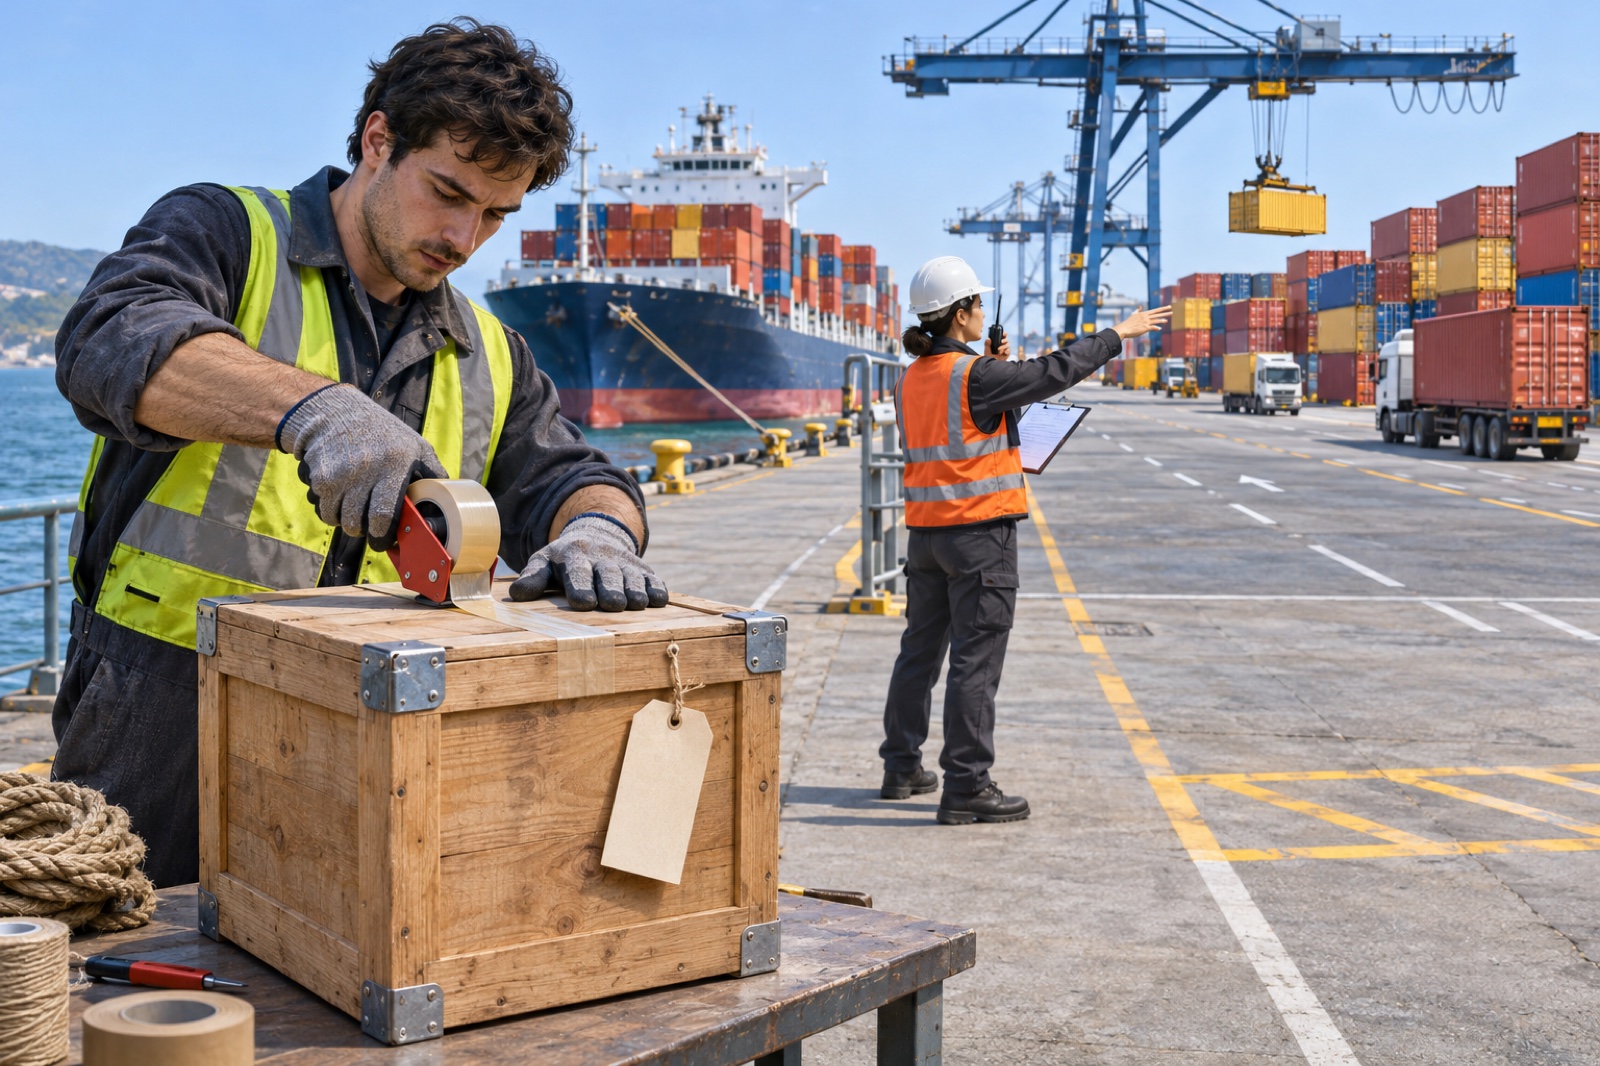
A developer can use Docker to package an application, then deploy that image to Kubernetes. The two names appear in the same command history, so it is easy to treat them as alternatives. A better mental model is a packaged crate and the port that schedules thousands of crates: one concerns the portable unit and its lifecycle; the other concerns where many units should run and how the fleet should recover when conditions change.
Docker handles the image and host-level container workflow
Docker describes itself as a platform for developing, shipping, and running applications in containers. Its client communicates with a daemon that manages images, containers, networks, and volumes. A Dockerfile defines image build steps; each instruction contributes a layer, and unchanged layers can be reused when an image is rebuilt. A registry stores images so they can be pulled onto another machine. [1]
An image is a read-only template; a container is a running instance of that image. That distinction explains why an image can be built once and then started in a test environment or production. The image carries application files and dependencies, while the runtime uses host-kernel facilities to isolate processes and resources. Containers are not small virtual machines: they share the host kernel, so their isolation model and security posture differ from a guest operating system running on virtualized hardware. [1]
The Docker CLI and daemon are one common way to perform these tasks, but they are not the only pieces that can create or run an OCI-compatible image. The Open Container Initiative publishes specifications for image formats and runtime behavior, which allow different tools to interoperate at those boundaries. Compatibility still depends on the image and runtime features in use. [4]
Kubernetes handles declared workloads across a cluster
Kubernetes is a system for managing workloads on a group of machines. An operator describes a desired state—for example, how many copies of a service should run—and Kubernetes controllers work to move observed state toward that target. A Deployment manages ReplicaSets and Pods; the scheduler places Pods on nodes, and controllers react when workloads or machines change. [3]
The container itself is launched by a runtime on each node. Kubernetes communicates with that runtime through the Container Runtime Interface (CRI), which separates Kubernetes components from one specific runtime implementation. The runtime is responsible for pulling images and creating containers; Kubernetes coordinates the higher-level objects, placement, and reconciliation. [2]
This is why the phrase “Kubernetes replaced Docker” is misleading. Kubernetes removed the dockershim integration in version 1.24, ending the direct adapter that let kubelet communicate with Docker Engine as a runtime. It did not make Docker a useless image-building tool, and it did not prevent compatible images from being used by other runtimes. The change was about the node runtime interface, not about banning images built with Docker. [2] [4]
How the tools fit together in one release path
A typical workflow might look like this: use a Dockerfile to build an image, push it to a registry, and configure a Kubernetes Deployment to reference that image. Kubernetes then schedules Pods and attempts to maintain the requested number of replicas. When a new image is released, a Deployment can roll out the updated template while monitoring readiness and replacing Pods according to its rollout strategy. [1] [3]
Each tool has a different job in that sequence. The image builder creates an artifact. The registry distributes it. The node runtime starts a container from it. Kubernetes decides which node should run the Pod and keeps the declared workload close to the target state. If the image cannot start, the orchestrator can retry or report the failure, but it cannot repair an application that has a bad configuration or incompatible dependency.
The division also clarifies debugging. If a build fails, inspect the Dockerfile, build context, dependency versions, and image layers. If a container works on a developer’s machine but fails in the cluster, compare runtime architecture, environment variables, mounted storage, network policy, and permissions. If the container starts but traffic does not reach it, look at Kubernetes Services, probes, ingress, and related networking configuration. “Docker versus Kubernetes” is not usually the root-cause question; the failure boundary is.
When a single host is simpler
Docker Compose can describe multiple related containers on one host, making it useful for local development and small deployments. Docker’s documentation describes Compose as a client for applications composed of several containers. A single host avoids cluster-level scheduling and control-plane operations, though it does not provide the same multi-node recovery and placement model as Kubernetes. [1]
Kubernetes becomes more relevant when a team needs coordinated scheduling across nodes, declarative rollout and recovery, or a shared platform for many services. It also brings more components to configure and maintain: API server, control plane, node agents, storage integrations, networking, policy, observability, upgrades, and access controls. The decision should follow operational requirements, not a belief that every containerized service needs a cluster.
A rough practical test is to ask which failure the new layer must handle. If the problem is inconsistent developer environments, an image and a simple local workflow may be enough. If one server is overloaded, a load balancer or vertical capacity change may be simpler. If workloads must be placed across machines and kept available while nodes or Pods fail, orchestration can help—but only if the team can operate the platform and design applications to tolerate those failures.
Choose boundaries before choosing products
Start by defining the artifact, runtime, and coordination requirements separately. Specify how images are built and scanned, where they are stored, which runtime executes them, and what system maintains the desired number and placement of workloads. Then decide whether a single-host tool or a cluster orchestrator is justified. This prevents a common mistake: adopting Kubernetes to solve an image-building problem or expecting Docker alone to provide cluster-wide scheduling and reconciliation.
Docker and Kubernetes work well together because each covers a different layer. Docker’s tooling can make an application repeatable to build and distribute. Kubernetes can coordinate many such workloads across a cluster. Understanding that division makes architecture decisions smaller, troubleshooting more targeted, and infrastructure choices easier to explain. [1] [2]
Frequently asked questions
Are Docker and Kubernetes competing products?
They solve different parts of a container workflow. Docker provides tools to build, distribute, and run container images. Kubernetes coordinates declared workloads across a cluster. A team can build an image with Docker-compatible tools and run it in Kubernetes.
Can Kubernetes run a Docker-built image without Docker Engine?
Usually, yes. Kubernetes nodes use a container runtime through the Container Runtime Interface. The runtime needs to understand the image format and run containers; it does not have to be Docker Engine. Kubernetes removed its built-in dockershim in version 1.24, while Docker-produced OCI-compatible images remain usable with compatible runtimes.
When is Docker Compose enough?
Compose can define and run a multi-container application on one Docker host, which is often enough for local development, tests, or a small single-host deployment. A cluster orchestrator is useful when the application needs scheduling and reconciliation across multiple nodes, but Kubernetes adds operational complexity.
Does a container provide the same isolation as a virtual machine?
No. Containers share the host operating-system kernel and use isolation mechanisms around processes and resources. Virtual machines run guest operating systems on virtualized hardware. The security and isolation properties depend on configuration and workload boundaries.
Sources & further reading
Keep reading
Cookies vs Sessions vs JWTs: Where Login State Lives and How It Fails
A comprehensive breakdown of client-side cookies, server-side sessions, and signed JWT tokens, including CSRF defenses and token revocation.
GraphQL Architecture Demystified: Client-Driven Queries, Resolvers and Federation
How GraphQL replaces fixed REST endpoints with flexible typed schemas, solves the N+1 problem with DataLoader, and scales via Apollo Federation.
Faster Go Services Start with Profiles: Allocation Hotspots, Benchmarks, and PGO
A measurement-first Go guide: benchmark representative work, inspect profiles, reduce costly allocations, and verify profile-guided builds.
/* Comments */
Comments are offline right now — we reconnect automatically, nothing is lost.