
Elastic Beanstalk Can Join Windows Instances to Active Directory Before Deploying
Elastic Beanstalk joins Windows instances to Active Directory at launch. Check platform, DNS, IAM and OU requirements—and why Ready can hide a failed join.
On this page
Windows applications often need machine identities that fit an existing directory, but boot-time domain joins have traditionally meant carrying scripts and credentials through instance provisioning. Elastic Beanstalk’s Windows platform now performs that join before application deployment. AWS published a hands-on setup guide on October 19; the feature itself is supported on Windows Server platform versions released from August 18, 2026 onward. The design removes a maintenance task, while making the network, identity and health-check details more important.
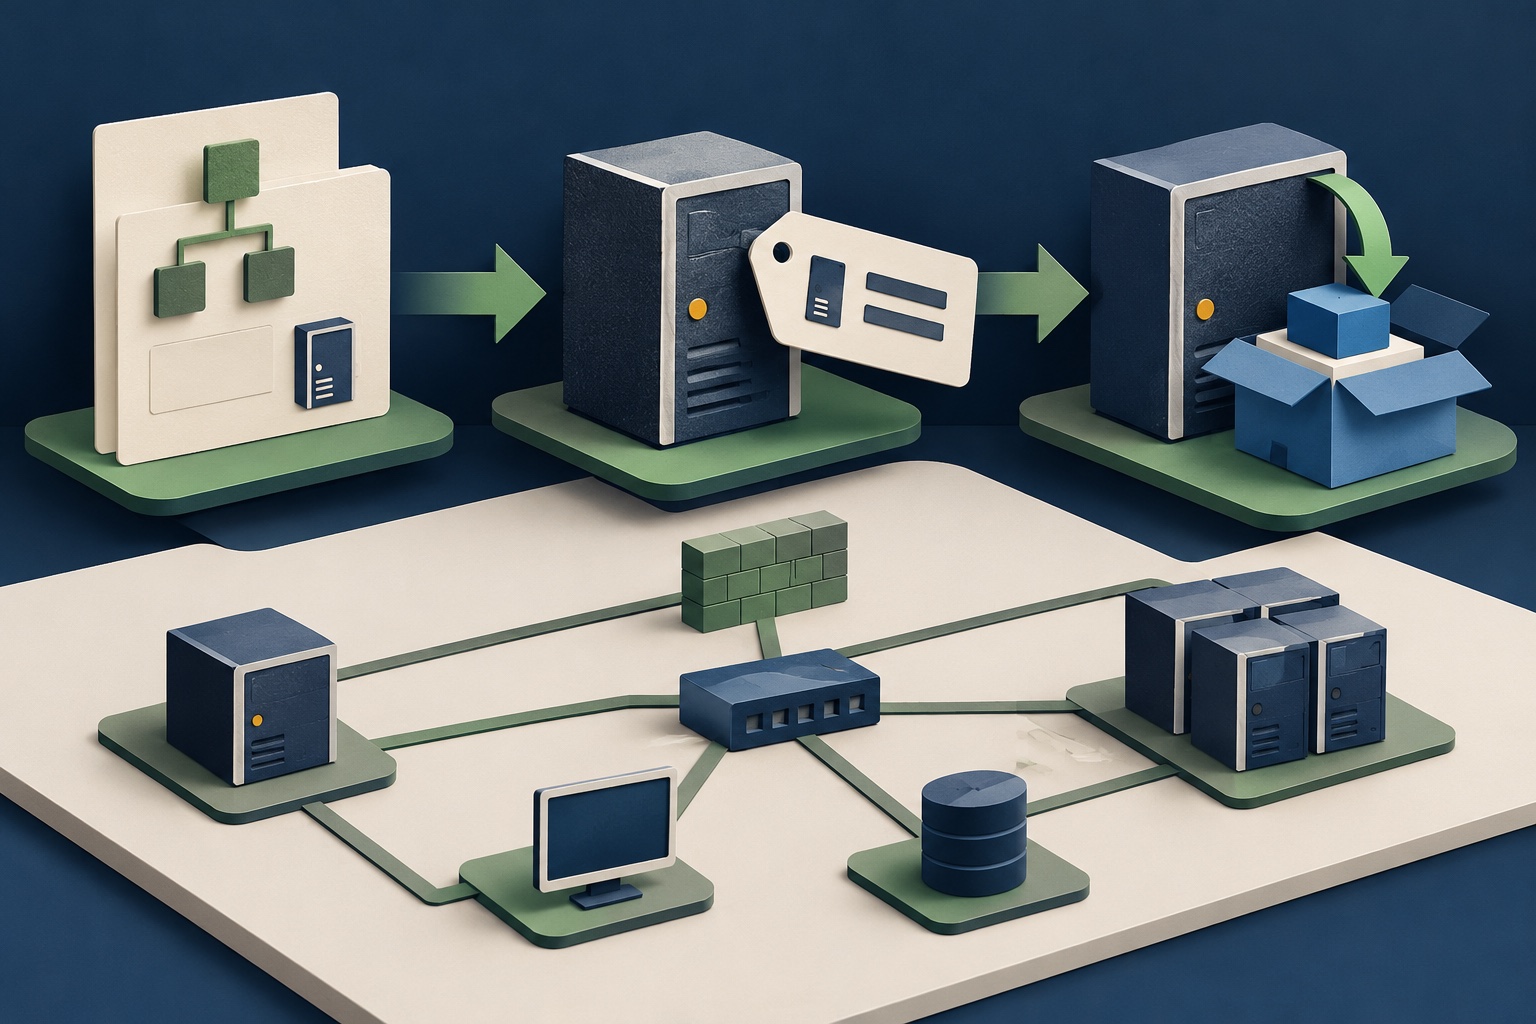
The instance joins before the application arrives
When the Active Directory options are set, each new Windows instance creates a computer object in the directory, renames itself using an instance-ID-derived hostname, joins the domain and reboots as part of normal provisioning. Then Elastic Beanstalk deploys the application. AWS says Auto Scaling instances added later follow the same process. The directory can be AWS Managed Microsoft AD, Simple AD or self-managed Active Directory connected through AD Connector. [1] [2]
That ordering is useful for applications that need domain identity during startup. The process does not require a custom join script or a domain password in the app’s deployment bundle. Instead, the instance profile calls Directory Service’s CreateComputer operation. The predictable EC2- hostname also avoids some collisions possible when the alternative IP-derived name is reused in disaster-recovery or long-lived environments. [2]
The feature has infrastructure prerequisites
First, the Elastic Beanstalk environment must use a qualifying Windows Server platform version, released on or after August 18. Older versions reject the configuration namespace. Second, instances need network connectivity to the directory and DNS resolution for its name; AWS notes that the VPC’s DHCP options set commonly points at the directory’s DNS servers. Third, the instance profile must be allowed to call ds:CreateComputer on the directory. Scope that permission to the directory where possible. If DirectoryOU is provided, that organizational unit must already exist—Elastic Beanstalk does not create it. [2] [3]
The configuration itself is a small set of options: directory ID, directory DNS name, and optionally an OU. The small syntax can obscure the lifecycle impact. AWS says adding, changing or removing any option in this namespace reprovisions EC2 instances through a rolling update. Treat enabling or retargeting domain join as an infrastructure deployment: review capacity, health checks, deployment policy and rollback behavior before applying it to a production environment. [2]
Ready does not prove domain membership
The most consequential operational caveat is how failure is surfaced. AWS says a domain-join failure does not block the deployment. The instance falls back to its usual IP-derived hostname, and the environment can still reach Ready and report healthy. Elastic Beanstalk emits an ERROR event, and the join output is included in deployment logs. The instance also stores a local join log, but the deployment log can be retrieved without connecting to the host. [2]
If the application assumes Windows integrated authentication, directory-backed service lookup or domain policy, an app health endpoint may not catch this mismatch. Add an explicit post-provisioning check that confirms membership or the expected EC2- computer object before routing production traffic to the new instance. During a rollout, alert on the ERROR event and inspect the join log for the immediate cause: unresolved directory DNS, missing IAM permission or an OU that does not exist. This is an engineering recommendation based on AWS’s described failure behavior, not a built-in guarantee that the service enforces application-level readiness.
There is also directory hygiene to plan for. AWS does not delete a computer object when its instance or environment is terminated. Scaling and replacement can leave stale entries behind, so assign an owner and cleanup process that checks object age and current instance inventory before removal. [2]
Related reading: Windows NTLMv1 hardening and legacy sign-in risk and how to choose an object-storage path for a Vercel app.
A safe first rollout
Start in a disposable environment using the same directory and VPC pattern as production. Confirm DNS resolution from the instance subnet, grant only the required directory-scoped permission, and validate the OU before enabling the options. Verify the new computer object and the deployment-log success line. Then intentionally test a failure in a non-production environment so the team knows how an ERROR event appears while the deployment can still report healthy. Finally, exercise a scale-out or replacement instance and check that the object cleanup process remains manageable.
This feature makes Windows domain integration less custom, but it does not make the directory path implicit. The useful operating model is to let Elastic Beanstalk perform the join and keep the application’s own readiness checks honest about whether that join actually happened.
Frequently asked questions
Does Elastic Beanstalk's Active Directory join require a domain password?
AWS documents the join as using the environment instance profile to call Directory Service CreateComputer. The instance needs network and DNS access to the directory, the ds:CreateComputer permission, and a supported Windows Server platform.
Can an Elastic Beanstalk environment be healthy if the domain join fails?
Yes. AWS says a failed join does not block deployment: the instance falls back to a standard IP-derived hostname and the environment may still become Ready and report healthy, while an ERROR event and deployment-log detail report the join failure.
Will enabling Active Directory replace running instances?
Yes. AWS says adding, changing or removing options in the Active Directory namespace reprovisions EC2 instances through a rolling update. Plan the configuration change and check for stale computer objects after instances are replaced.
Sources & further reading
- AWS DevOps Blog: Automate Active Directory joins for Elastic Beanstalk Windows applications
- AWS Elastic Beanstalk Developer Guide: Joining instances to an Active Directory domain
- AWS Elastic Beanstalk configuration options: Active Directory
- AWS Directory Service Administration Guide: Getting started with AWS Managed Microsoft AD
Keep reading
AWS CodeDeploy RESTART Reuses a Revision, but Your Fleet Still Needs a Drain Plan
CodeDeploy RESTART reapplies an EC2 or on-prem revision under deployment safeguards. See its agent, lifecycle and traffic-drain requirements.
Lambda Web Functions Put a Shared Node Server Behind an AWS Endpoint
AWS Lambda Web Functions run a standard Node.js HTTP server with concurrent requests. Learn the cost model, scaling limits and application risks to test.
Computer Use Agents: Building a Security Boundary Around the Desktop
GUI agents can act on untrusted screen content. Isolated environments, narrow permissions and action checks reduce risk without making a sandbox infallible.
/* Comments */
Comments are offline right now — we reconnect automatically, nothing is lost.