
Three Cryptography Papers Ask How Computing Can Be Trusted
NTT researchers present work on certified randomness, quantum-program protection, and more compact proofs. Each result remains theoretical.
On this page
A quantum computer that produces an answer is only useful when others can trust the answer, protect the program that produced it, and verify the process without exposing private inputs. Three papers involving NTT Research scientists at FOCS 2026 tackle pieces of that problem. They are advances in mathematical foundations, not evidence that practical quantum systems have solved security.
Three different trust problems
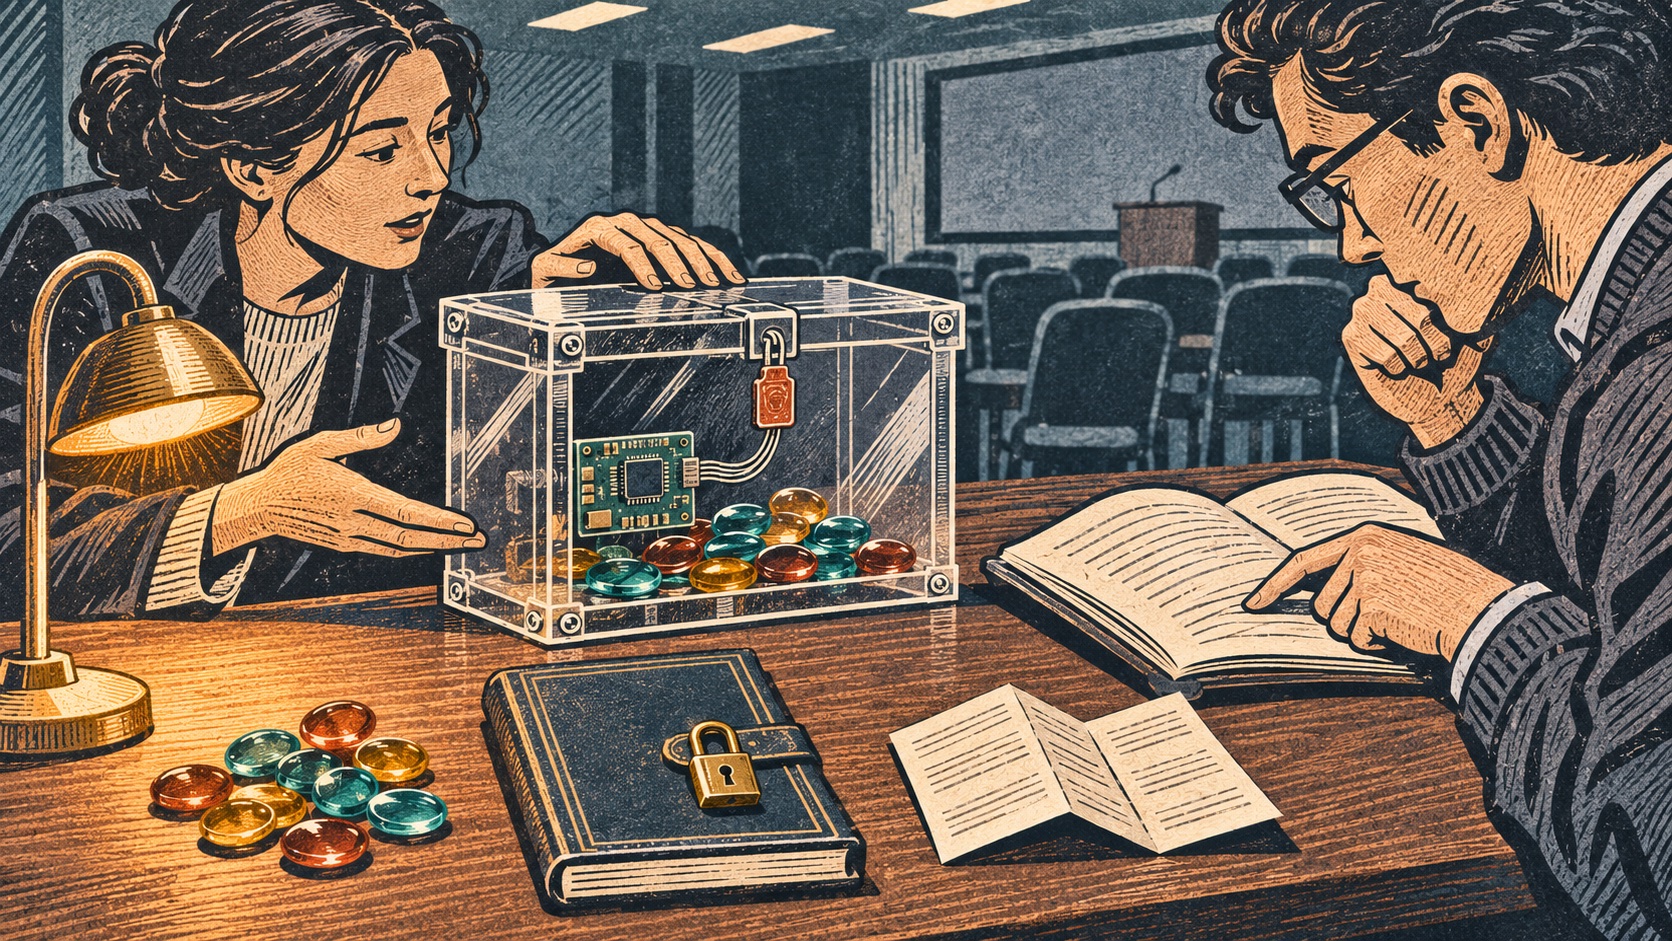
The papers address separate questions that are easy to blur together. The first studies certified randomness: under defined conditions, can a verifier gain confidence that output generated by a quantum process contains unpredictable bits? The result strengthens a protocol against a class of shallow-query adversaries without relying on a conjecture used by earlier work. Its formal threat model matters; it is not a certificate that a particular device’s random-number output is safe for every purpose. [1] [3]
The second paper concerns protecting quantum programs and checking outsourced computation. It gives a theoretical construction for classical obfuscation of pseudo-deterministic quantum circuits, using publicly verifiable quantum fully homomorphic encryption relative to a classical oracle. In plain terms, the work explores how an evaluator might process encrypted data while an outside party checks that a computation followed the protocol. The “relative to an oracle” qualification is a model assumption, not an implementation detail to skip. [1] [4]
The third attacks a less visible cost in cryptography: padding inserted because a security proof requires it, even when the padding is not needed for the scheme’s function. The authors connect the possibility of removing that overhead to the hardness of certifying that strings are incompressible, then derive more succinct versions of several cryptographic constructions under that assumption. Smaller constructions could matter for resource limits, but the paper is a theoretical framework and does not report a production deployment. [1] [5]
FOCS’s program lists the relevant papers among its 2026 research sessions, placing them in a peer-reviewed foundations-of-computer-science forum. Conference acceptance is evidence of scholarly review, not proof that every assumption or future application will hold in practice. [2]
Why these foundations matter before a product exists
Cryptography often has a long gap between a formal construction and an operational system. A real service must handle implementation bugs, side channels, key management, user error, and the cost of computation. A proof can establish security within a mathematical model while leaving those system risks untouched.
That gap is not a reason to dismiss foundational work. If future systems delegate computation to hardware or cloud services, independent verification and privacy-preserving execution could be useful design goals. If cryptographic proofs force large overheads, identifying when that overhead can be removed may eventually make advanced tools more practical. But those are possible applications, not outcomes demonstrated by these papers.
How to read the claims
Readers should look for the adversary model, assumptions, and exact object being protected. “Certified random” depends on what the verifier can observe and what the attacker can control. “Publicly verifiable” does not automatically mean that a computation is fast, universally composable, or secure under every implementation. “Succinct” describes size bounds in the paper’s construction; it does not guarantee a cheaper product.
For engineers, the useful action today is to treat this as a research signal. Track the underlying papers and later implementations, but do not revise deployed cryptographic systems based on a press release. For researchers, these results identify questions that can now be tested against stronger models and practical constraints.
The three papers share a theme: trust needs evidence about how a result was produced, not just a result that looks plausible. Their contribution is to sharpen that evidence mathematically while leaving substantial engineering work ahead.
Frequently asked questions
Are these papers new commercial quantum-security products?
No. The papers present theoretical constructions and security results. They do not announce deployable products or tested commercial systems.
What does public verification mean in the quantum-computation paper?
The work studies a protocol in which an outside party can verify a computation's result under its stated model and assumptions, without receiving the private computation data.
Does certified randomness mean any quantum device can prove its output is random?
No. The result applies under specific formal assumptions and adversary limits described in the paper; it is not a general certification for arbitrary hardware.
Sources & further reading
- NTT Research: three papers at FOCS 2026, Nov. 8, 2026
- FOCS 2026 main program
- Khurana, Roberts, and Tal: Certified Randomness without Structure Against Shallow-Query Adversaries
- Bartusek et al.: Classical Obfuscation of Quantum Circuits via Publicly-Verifiable QFHE
- Hsieh et al.: Overcoming Padding in Cryptography via Hardness of Certifying Random Strings
Keep reading
AI Proved Parts of Signal’s Code. Here Is What That Actually Guarantees
Google DeepMind used Lean-checked proofs on Signal’s libsignal code. The result is meaningful assurance with a carefully bounded scope, not a blanket guarantee.
A New EU Project Wants Privacy Defenses to Follow People Across Devices
REAL-PETS will study cross-platform tracking and usable privacy tools. The three-year project is a research plan, not a protection people can install today.
DeepMind’s RSA-1024 Results Don’t Mean Today’s Keys Were Cracked
Two DeepMind working papers report a faster legacy RSA computation and a theoretical factoring method. Neither breaks deployed 2048-bit RSA.
/* Comments */
Comments are offline right now — we reconnect automatically, nothing is lost.