
Oracle’s October CPU Lists 1,295 Patches; Your Risk Is in the Product Matrix
Oracle’s October 2026 CPU spans dozens of products. Map versions and exposure instead of treating the patch count as a queue.
On this page
A security bulletin with more than a thousand patches can create two bad reactions: panic because the total sounds enormous, or delay because the list feels impossible to process. Oracle’s October Critical Patch Update is broad, spanning database, middleware, Java, business applications, developer tools and other product families. The headline number is a starting point. The next question is whether your exact deployed versions appear in the advisory and how exposed they are.
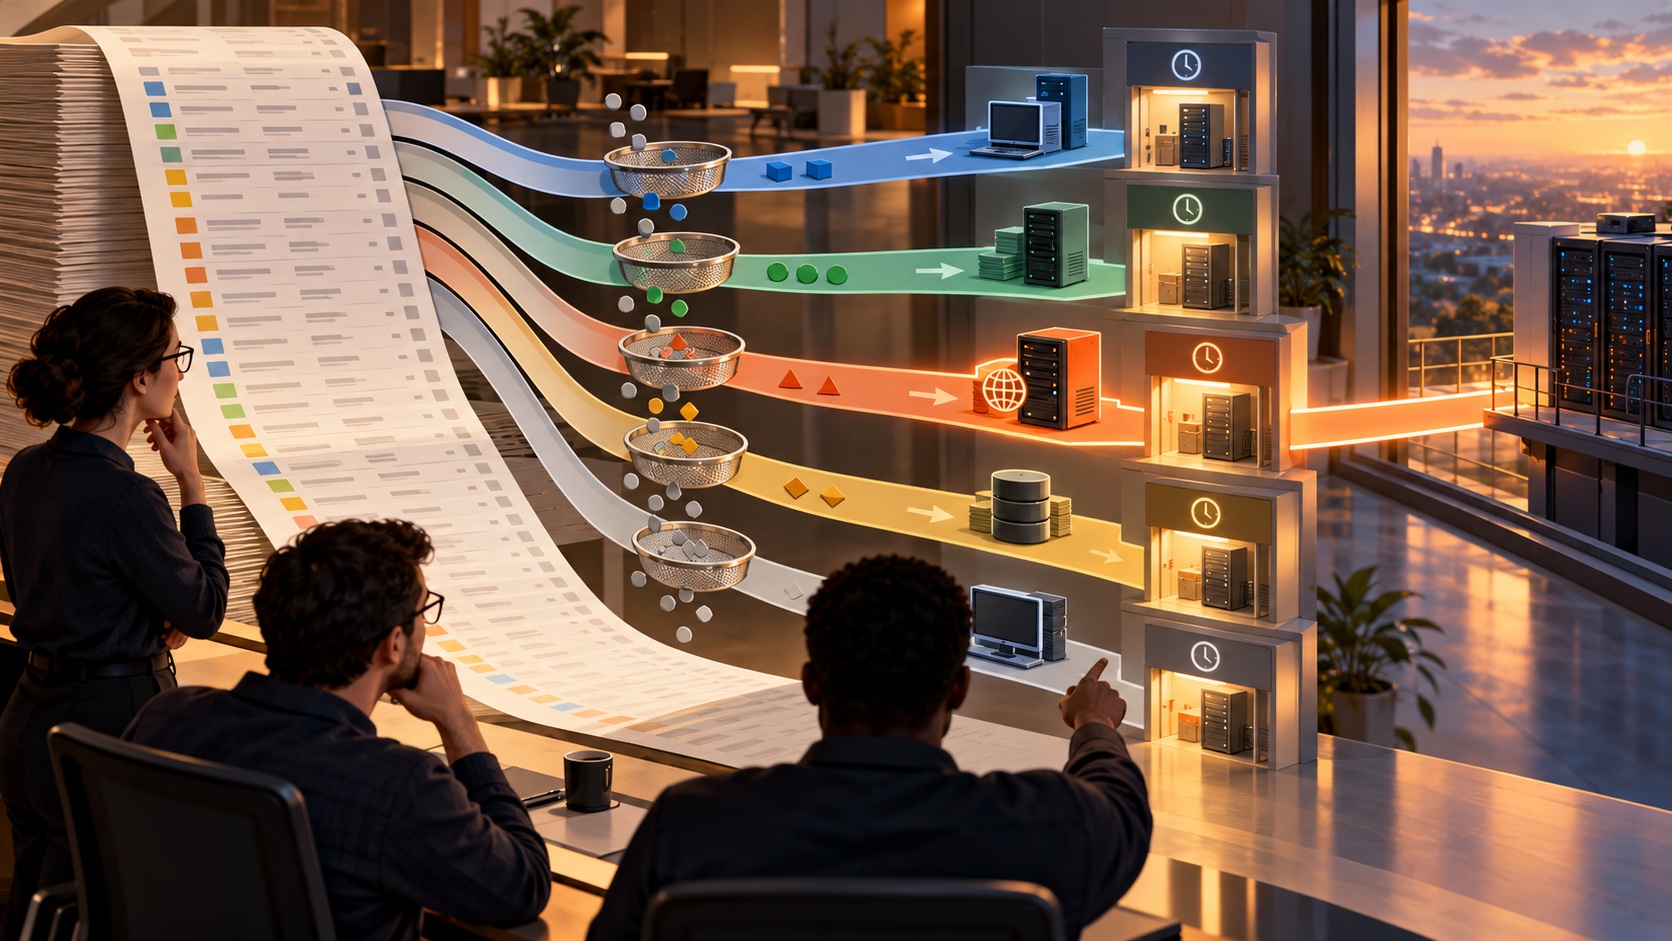
Read the number precisely
Oracle’s October 20 announcement points customers to the CPU advisory and recommends moving to a monthly security patching cycle. The advisory says it contains 1,295 new security patches across the listed product families. That figure is not necessarily a count of unique CVEs: Oracle explains that one vulnerability can affect multiple products, and a patch may address multiple CVEs. The release is therefore best read as a product-specific remediation catalog, not one universal vulnerability event. [1] [2]
The advisory’s tables carry the information administrators actually need: affected product and versions, patch availability documents, CVE identifiers, remote exploitability without authentication and CVSS 3.1 risk details. For Java SE, for example, Oracle lists 55 new security patches and says 49 relate to vulnerabilities that may be remotely exploitable without authentication. That is a product-specific signal, not a summary of the entire CPU or proof that a particular Java installation is vulnerable. [1]
The distinction between “patches,” “vulnerabilities,” and “affected installations” prevents misleading prioritization. A large patch total can cover many products an organization does not use. Conversely, one remotely reachable flaw in a critical internet-facing service can matter more than hundreds of patches for absent or isolated components.
Build the product-to-system map
Start with an inventory that records Oracle product, exact version, support status, host or managed service, exposure, business owner and maintenance window. Include embedded components: a team may know it runs a custom application without realizing that the application bundles an affected Oracle component. Compare the inventory against the advisory’s affected versions and follow each product’s patch availability document for installation instructions. Oracle notes that CPU releases are cumulative, while each advisory describes patches added since the previous CPU, so older advisories can matter when systems skipped earlier cycles. [1]
Then rank the matches using context. Is the vulnerable component reachable from an untrusted network? Does the advisory mark exploitation as possible without authentication? Does the system hold sensitive data or control a critical process? Is the instance actively supported and on a release with a patch path? Those questions help separate urgent exposure from routine maintenance while keeping the decision grounded in actual deployment details.
NIST’s enterprise patch-management guidance describes patching as a lifecycle: identify, prioritize, acquire, install and verify updates. It recommends a strategy that makes patching operationally repeatable, not a one-off reaction to a large bulletin. For an Oracle estate, that means having owners, test environments, backup and recovery plans, and a record that confirms the patch actually reached the intended version. [4]
Test and verify the change
Patching a production database or ERP system can affect application compatibility, integrations, failover and scheduled jobs. Use the vendor’s product-specific instructions and supported configurations. Test the update in a representative environment, validate backups and rollback or recovery procedures, and confirm that business owners can perform critical transactions after maintenance. If a patch cannot be applied immediately, record the reason, compensating controls and next review date rather than letting the exception disappear in a ticket queue.
After deployment, verify the installed patch level from the system itself and reconcile it with the change record. A downloaded bundle or closed ticket does not prove the running instance is fixed. Include scanner coverage and asset-owner confirmation where appropriate, but treat scanner output as another evidence source to resolve, not as a substitute for version checks.
Oracle publishes CPU releases quarterly on the third Tuesday of January, April, July and October, with additional monthly critical updates on other scheduled months beginning in 2026 according to its security-fixing policy. Teams should confirm the current release cadence on Oracle’s official page and build the relevant dates into their maintenance calendar. [3]
What not to infer from a huge bulletin
The 1,295 figure does not mean every Oracle customer has 1,295 urgent actions. It also does not mean a low count in one product means low risk: exploitability, network exposure, privileges and system importance all matter. A single CVE may appear in multiple risk matrices, while the same patch may address related CVEs. Count headlines are useful for conveying breadth but poor as an operational queue.
The October CPU’s practical value is its detailed mapping from product versions to fixes. Administrators should use that structure to find the subset that applies, schedule changes according to risk and prove the updates landed. If an organization’s asset inventory cannot answer which Oracle versions are running and who owns them, that inventory gap—not the headline number—is the immediate problem to resolve.
Frequently asked questions
How many security patches are in Oracle’s October 2026 CPU?
Oracle’s advisory says the October Critical Patch Update contains 1,295 new security patches across its listed product families. That count refers to patches, not necessarily 1,295 unique vulnerabilities, and a single patch can address multiple CVEs.
How should administrators prioritize the Oracle October 2026 CPU?
Map each product and version in the advisory to deployed instances, exposure and business criticality, then consult the corresponding patch availability document and risk matrix. Test and verify the applicable update; the headline total alone cannot identify which systems are affected.
Sources & further reading
Keep reading
GitHub Actions Lockfiles Pin the Workflow Behind a Readable Tag
GitHub’s Actions lockfiles resolve moving tags to exact commits, including transitive dependencies. They improve reproducibility but do not certify safety.
Node.js’ October Security Release Fixes DNS, TLS and Brotli Risks Across Three Lines
Node.js shipped security updates for 26.x, 24.x and 22.x on October 21. Inventory runtimes, patch deployed binaries and verify the process actually restarted.
GitHub Says Its Secret Classifier Finds More Credentials With Less Noise
GitHub reports faster secret scanning and higher alert acceptance after adding context classification. What the numbers mean for security teams.
/* Comments */
Comments are offline right now — we reconnect automatically, nothing is lost.