
eMudhra Is Winding Down Public TLS. What Certificate Teams Should Do Next
eMudhra disclosed weak intermediate keys and plans to exit public TLS issuance. Here is how certificate teams can plan a safe transition.
On this page
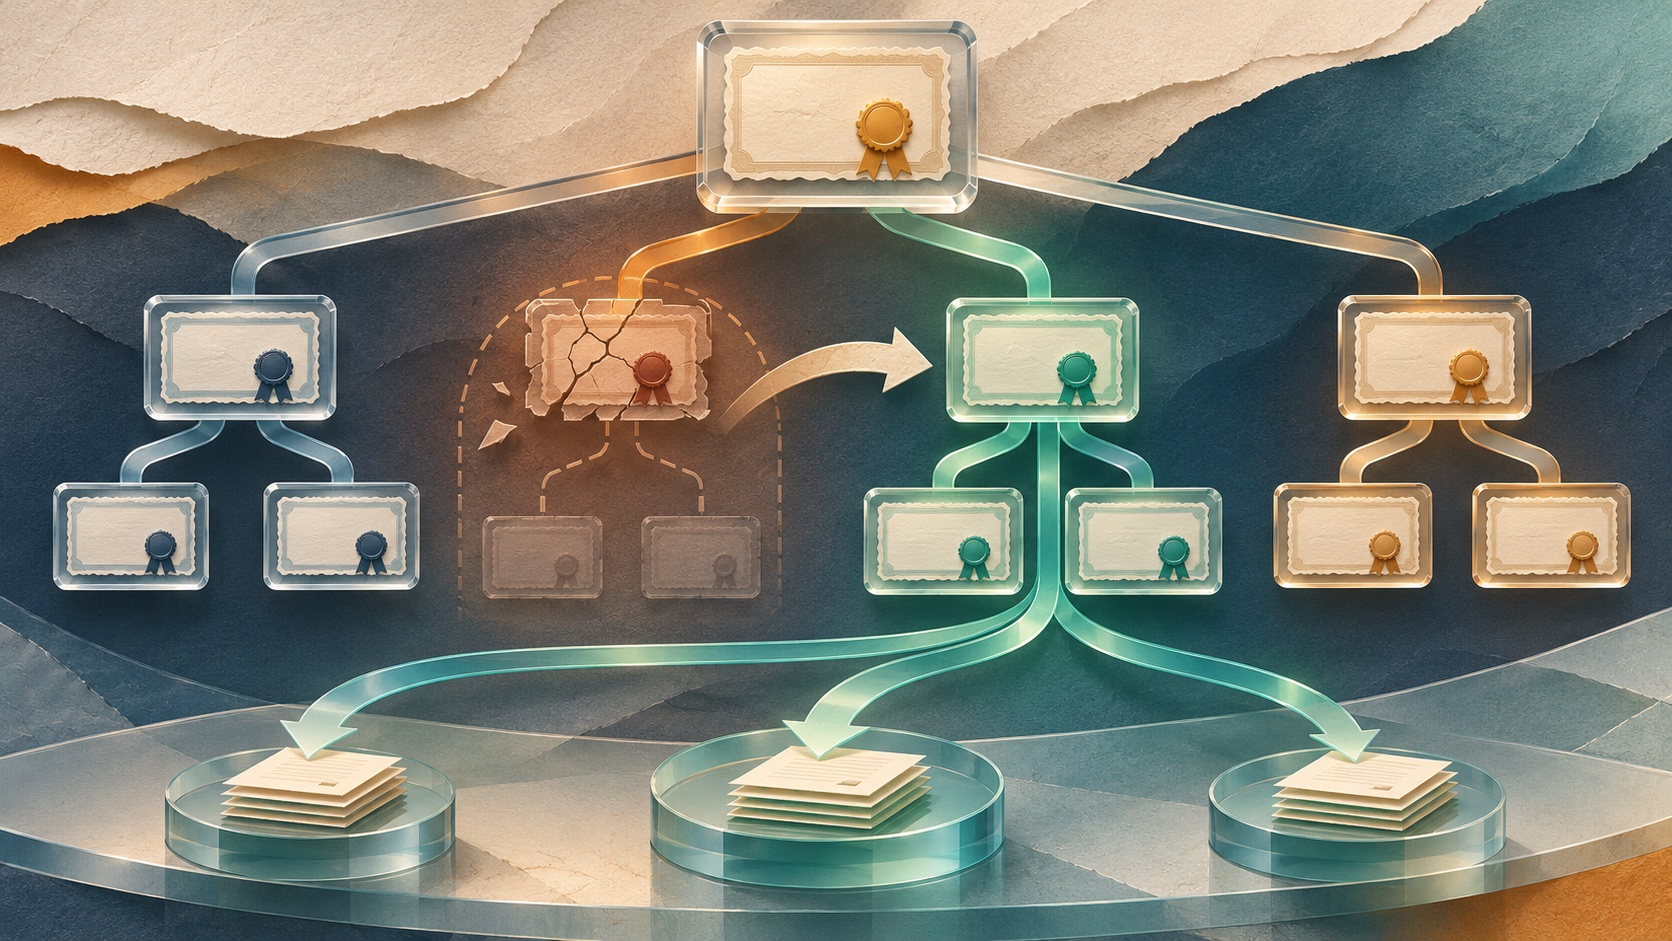
Certificate incidents travel through a chain of authorities, root stores, libraries and applications. A warning in one browser is a useful signal, but it does not tell an administrator which workloads still trust which part of that chain. The latest eMudhra updates add a second operational change: customers must plan for the provider’s stated exit from publicly trusted TLS issuance.
What changed after the first disclosure?
On October 17, 2026, a researcher reported that private keys for eight eMudhra intermediate certificate authorities were recoverable. eMudhra’s incident account says a script error during a key-generation ceremony created weak keys alongside the intended strong keys; Mozilla’s response described the report as a compromise and blocked the affected certificates in Firefox. These are vendor and browser-operator statements about the incident, not evidence that an attacker used the keys to impersonate a live site.
The distinction between an intermediate CA and a root matters. The eight intermediates sit below a signing root. eMudhra said the intermediates had not issued end-entity certificates, yet browser programs also distrusted the relevant ECC root as a precaution. eMudhra’s October 28 update describes roughly 30,800 certificates in the affected G3 hierarchies associated with one U.S. customer ecosystem, using an alternate path while transition work proceeds. On November 5, the incident page still showed October 30 as its latest dated update and had not published a completed root-cause analysis.
The trust-store response is also platform-specific. Mozilla used OneCRL for Firefox and updated NSS so applications using Mozilla-derived trust data can receive the change. Apple says its devices automatically block the affected TLS intermediates and began blocking the associated ECC root on October 23. Apple separately warns that some command-line tools, including certain macOS and Xcode Command Line Tools that consult /etc/ssl/cert.pem, may continue to accept certificates until a future software update. That is a concrete example of why “the browser is fixed” and “the fleet is fixed” are different claims.
The business transition is now part of the incident response
In its October 28 incident update, eMudhra said it was moving customers to alternate certificate providers and would stop issuing publicly trusted TLS certificates from its G1 root after the affected customer federation completes its transition. Its October 22 press release describes the board’s decision to exit the global SSL/TLS certificate business, while its October 30 update names KPMG as an independent reviewer.
Those are company statements and future commitments. They do not establish that every customer has completed migration, that the root-cause review is finished, or that a specific replacement provider is appropriate for every deployment. The provider change does, however, give certificate owners a planning deadline they should not confuse with the immediate trust-store mitigation.
Treat chain distrust as a platform-remediation task and issuer wind-down as a certificate-lifecycle task. The first belongs with endpoint, OS, runtime and application owners; the second belongs with service owners and whoever manages renewal, inventory and vendor relationships.
A practical response for platform and service teams
Start with inventory, not a global search-and-delete. Find certificates issued under the affected hierarchies, record each leaf certificate’s issuer and expiration, and identify where the chain is consumed: public endpoints, internal TLS, Java truststores, container images, appliances, command-line clients or pinned certificate bundles. Certificate transparency and issuer metadata can help, but the service owner should validate each live chain.
Next, map trust behavior by platform. Record which clients use the operating system store, which carry an independent bundle, which use NSS, and which ship a runtime-specific store. Apply the Apple, Mozilla or other vendor update through normal patch channels. For tools Apple calls out as exceptions, follow Apple’s current guidance and test the affected command-line workflows before making a targeted local change. Avoid removing a root from a shared trust file without checking whether unrelated services depend on it.
Then rotate affected service certificates to an approved alternate CA. Test the complete chain from representative clients, including older runtimes and build agents. A successful browser check does not certify a workload’s private JVM, Python image or embedded device. Record the new issuer, validation date, renewal owner and fallback plan in the certificate inventory.
Finally, review the provider’s announced transition with a written schedule. Ask which certificate families are in scope, when new issuance stops, what alternate paths are offered, and how renewal support works during the transition. Require confirmation from the provider for account-specific dates; the public incident page cannot tell an individual customer whether its move is complete.
For teams reviewing adjacent trust and runtime changes, Crashtech’s Node.js October security release guide covers why TLS fixes still need application-level rollout planning, and our SSH post-quantum transition explainer shows how a separate trust migration can require a different client inventory.
What would change this assessment?
A published root-cause report, a final customer-transition status, or a new root-program notice could alter the operational picture. Until then, separate what browser operators have already blocked, what eMudhra says about the customer migration, and what remains a future commitment. The safest useful message is narrower than “replace everything”: identify affected chains, verify each platform’s trust behavior, and schedule a controlled move to a new issuer.
Frequently asked questions
Were the affected eMudhra intermediate certificates used to issue customer certificates?
eMudhra says the eight weak intermediates did not issue end-entity certificates. The wider response also involves distrust of the signing ECC root, which affects a customer ecosystem and certificate chains beyond those eight intermediates. Check the chain and platform notice rather than treating the two scopes as identical.
Do all administrators need to remove an eMudhra root manually?
No. Apple says its managed trust updates block the affected TLS intermediates and root, while noting that some command-line tools can use a separate certificate bundle until a future update. Follow the platform vendor's current instructions and avoid unscoped edits to system trust files.
What did eMudhra announce after the initial incident?
The company's updates describe customer migration to alternate issuance, a voluntary wind-down of publicly trusted TLS certificate services, and appointment of KPMG as an independent reviewer. As of November 5, 2026, the latest dated item on its incident page was still the October 30 review announcement; a completed root-cause analysis had not appeared there.
Sources & further reading
Keep reading
CodeQL 2.27.4 Fixes Specific False Positives and Tightens Pack Publishing
CodeQL 2.27.4 updates query behavior, metadata and pack handling. Learn how security teams can assess the changes without assuming every alert is solved.
Dependabot Can Now Update Agent Skills and Prompts Through APM
Dependabot now updates supported Agent Package Manager dependencies. Learn what its manifest and lockfile support covers—and what security updates do not.
GitHub Actions Lockfiles Pin the Workflow Behind a Readable Tag
GitHub’s Actions lockfiles resolve moving tags to exact commits, including transitive dependencies. They improve reproducibility but do not certify safety.
/* Comments */
Comments are offline right now — we reconnect automatically, nothing is lost.