
Dependabot Can Now Update Agent Skills and Prompts Through APM
Dependabot now updates supported Agent Package Manager dependencies. Learn what its manifest and lockfile support covers—and what security updates do not.
On this page
An agent instruction file can be a dependency just as surely as a library is. It may shape which tools an agent calls, how it handles files, or what it says to the user. GitHub’s November 3 addition lets Dependabot propose version updates for supported Git dependencies used by APM, rather than leaving those references to drift unnoticed. [1] [2]
What the integration actually does
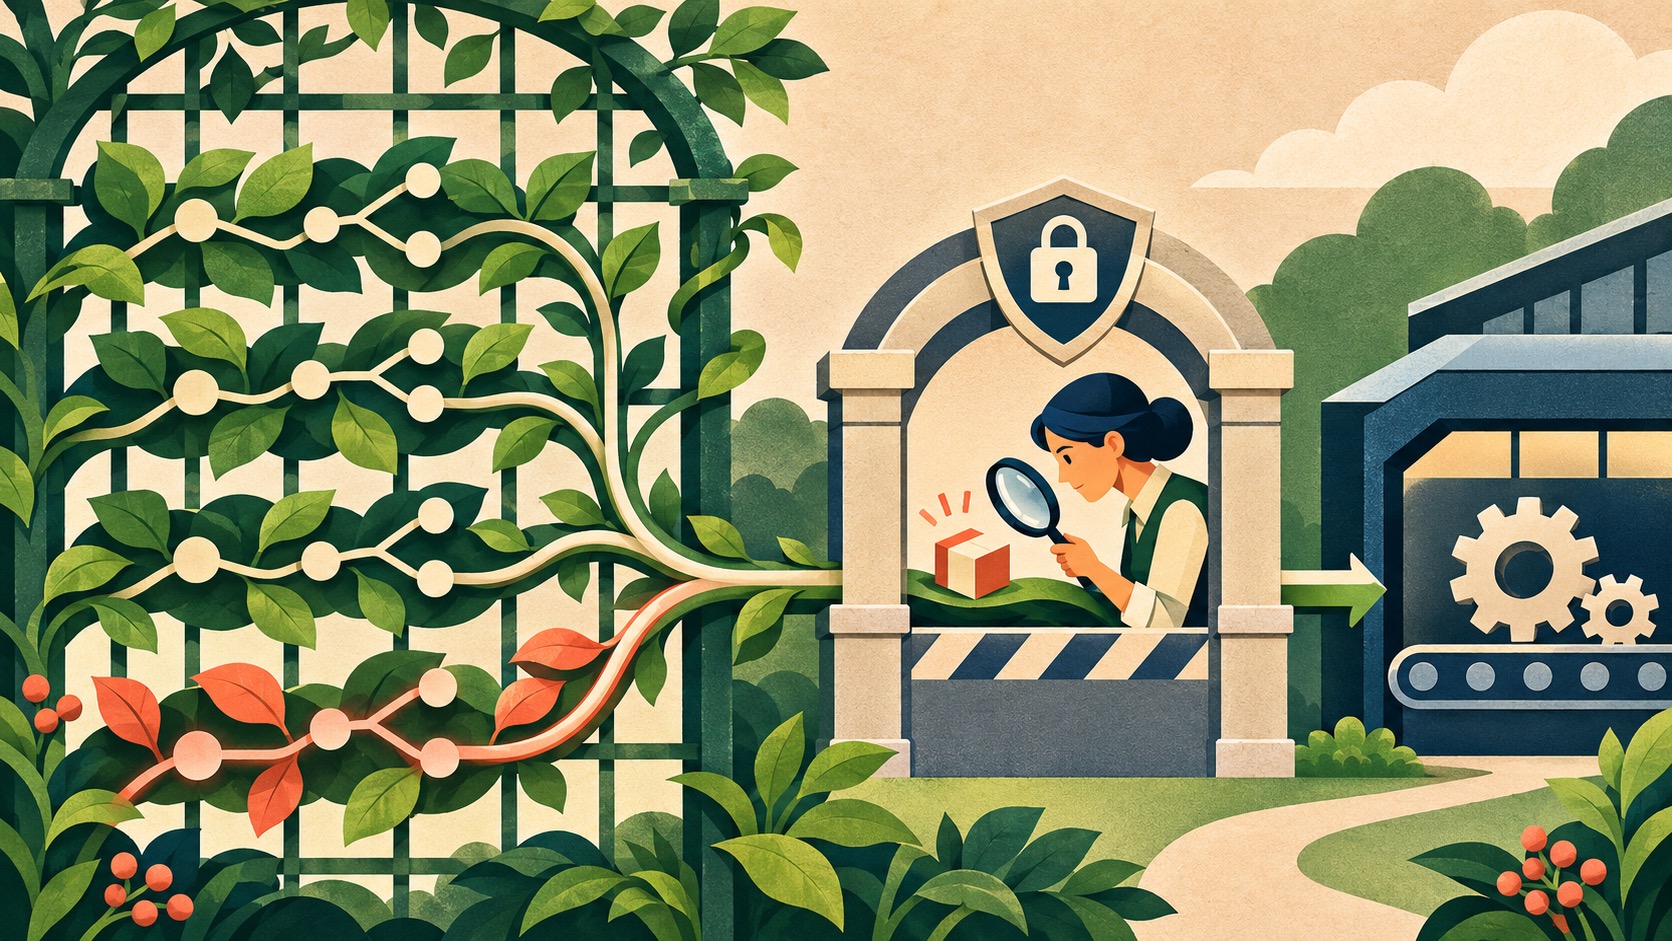
APM describes a manifest and lockfile approach for managing agent skills, prompts and instructions. GitHub says Dependabot version updates now cover supported Git dependencies declared in apm.yml; when an apm.lock.yaml file exists, Dependabot regenerates it as part of the update. That creates a familiar review point: a pull request can show that a dependency reference and its resolved state changed. [1] [2]
The boundary is important. GitHub says this feature handles version updates, not security updates. A newly published version is not necessarily a security fix, and a version update is not a vulnerability finding. Teams should not interpret the feature as a scanner for malicious instructions or as a guarantee that a prompt’s behavior stayed stable.
Why agent packages deserve dependency review
Traditional dependency review asks what code will run and which maintainers control it. Agent packages add another question: what instructions and tool-use conventions will influence a model’s next actions? A skill that changes from “summarize these files” to “run this command” can alter risk even if its package name remains familiar. A prompt update can also change output format, tool selection or assumptions in ways that break a downstream workflow.
The same controls still help. Pin and review sources, limit who can approve updates, compare the manifest and lockfile diff, and run the agent only in the permissions boundary appropriate to the task. If the package can direct an agent to execute code or transmit content, test it in a disposable environment with representative untrusted inputs before merging.
A practical adoption checklist
- Confirm the repository’s
apm.ymldependencies are supported by the current Dependabot implementation. Do not assume every source or version scheme is covered. - Add the appropriate update configuration and inspect the first pull request manually.
- Review both the manifest change and lockfile regeneration. Verify the resolved commit and upstream project rather than relying only on a release label.
- Run the agent package in a low-privilege test context. Check whether its instructions alter tools, permissions, network access or data handling.
- Keep security scanning and supply-chain review in place. This specific announcement is version-update automation, not vulnerability remediation. [1] [3]
This is a modest integration with a useful implication: teams can manage agent instructions with the same visible update cadence used for code dependencies. The safeguard remains human review. A pull request makes change observable; it does not make the change trustworthy by itself. For another dependency pinning control, see our guide to GitHub Actions workflow lockfiles and the practical lockfile implementation details.
Frequently asked questions
Does Dependabot now scan APM packages for vulnerabilities?
The November 3 announcement covers version updates for supported Git dependencies in apm.yml. GitHub explicitly says this support is for version updates, not security updates.
What happens to apm.lock.yaml?
When the repository has an apm.lock.yaml lockfile, Dependabot regenerates it as part of an update pull request. Maintainers still need to review and test the resulting change.
Sources & further reading
Keep reading
GitHub's December pull_request_target Rule Needs a Workflow Audit Now
GitHub will block pull_request_target by default in public repositories on December 2. Use the November brownouts to find affected workflows.
GitHub Adds a Starlink Token Pattern and Refines Secret Scanning
GitHub's latest secret scanning update adds a Starlink credential detector and narrows matches for several providers. Here's what the change covers.
CodeQL 2.27.4 Fixes Specific False Positives and Tightens Pack Publishing
CodeQL 2.27.4 updates query behavior, metadata and pack handling. Learn how security teams can assess the changes without assuming every alert is solved.
/* Comments */
Comments are offline right now — we reconnect automatically, nothing is lost.