
Cloud Sovereignty Is a Control Test, Not a Map Pin
EU cloud sovereignty means more than data location. Map operational control, legal exposure, dependencies and recovery for each workload.
On this page
A server can sit inside a country while the customer still depends on an outside company for privileged support, software updates, encryption control or service recovery. That is why “sovereign cloud” cannot be reduced to a data-center address. The European Commission’s framework makes the question more concrete: what control does the buyer retain, what dependencies remain, and how resilient is the service if the normal operating relationship changes?
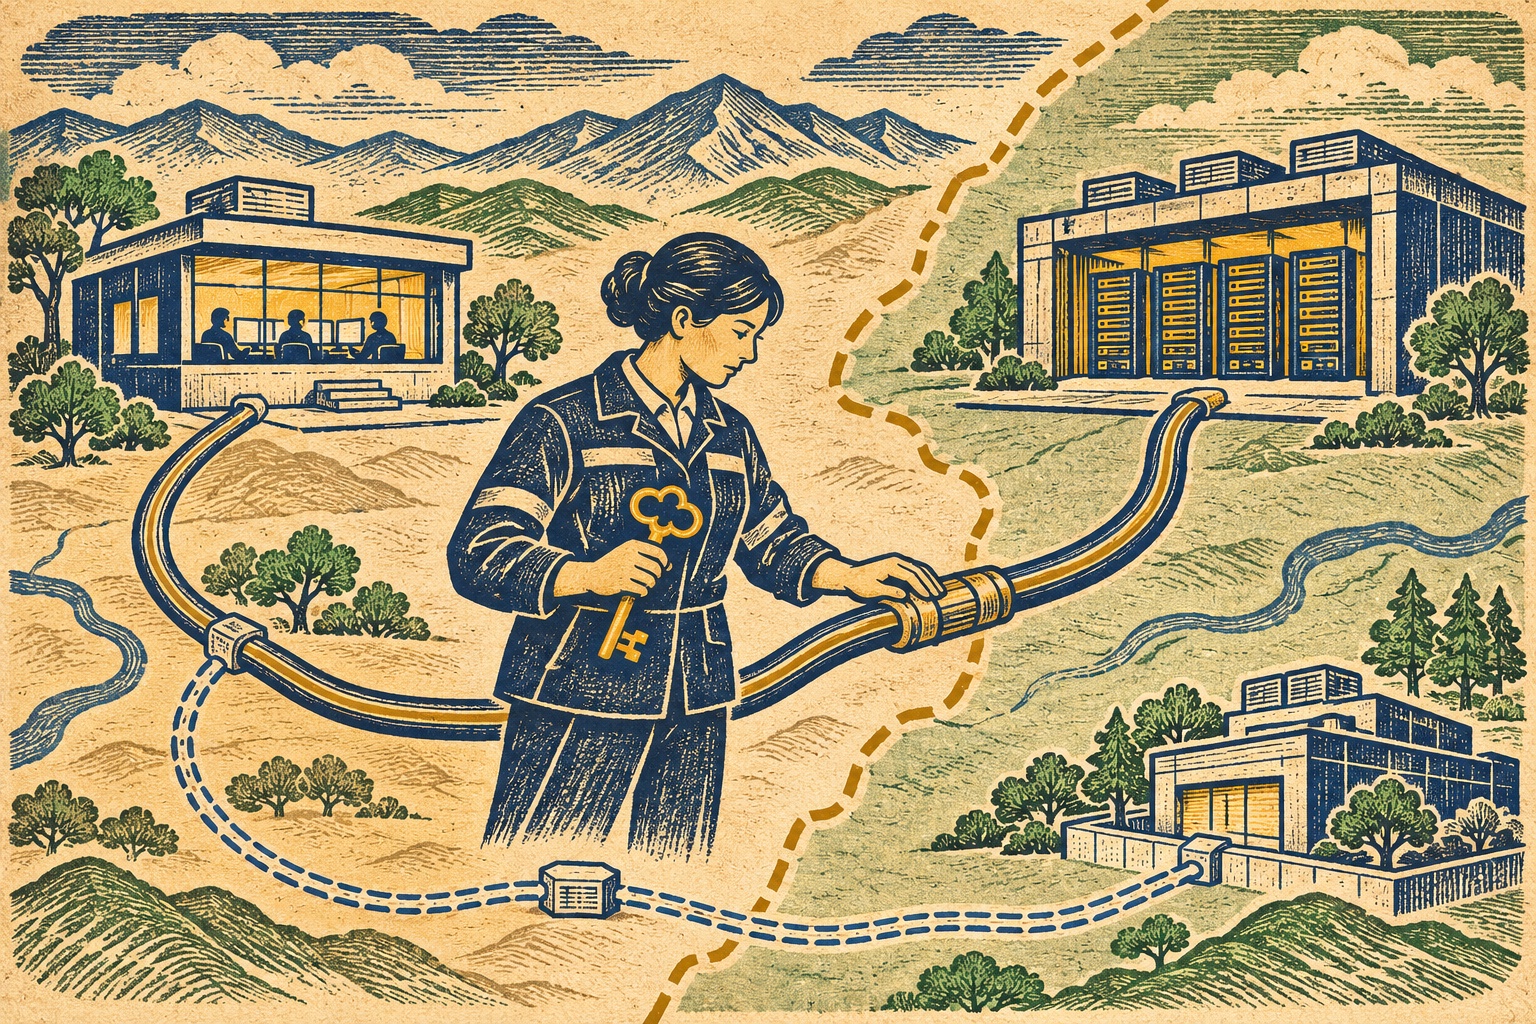
What the Commission’s framework measures
The Commission describes its Cloud Sovereignty Framework as a tool used to assess providers in a procurement. Its 2025 framework document defines sovereignty objectives and evidence-based assessment, while the Commission’s June 2026 explainer describes two complementary measures: a Sovereignty Effectiveness Assurance Level (SEAL) and a sovereignty score. The assurance levels distinguish thresholds such as data sovereignty, technological autonomy and full sovereignty. They are assessment dimensions for that procurement context, not a universal certification label that automatically applies to every product a provider sells. [1] [2]
The tender itself is instructive. In April 2026 the Commission awarded a contract worth up to €180 million over six years to four providers for EU institutions. That multi-provider outcome shows sovereignty can be pursued through procurement choices and workload placement, rather than by assuming one supplier or one national location solves every dependency. It does not mean the EU has eliminated external technology or legal dependencies across its whole public sector. [4]
Ask workload questions, not brand questions
A useful assessment starts with the workload and the failure it must withstand:
- Data control: Where is content stored and processed? Who can access it, and under which support or emergency conditions?
- Operational control: Who can administer the service, issue updates, manage keys and restore systems? Can local staff operate it during a connectivity or political disruption?
- Legal exposure: Which entities and legal regimes could compel access or constrain service? Data residency does not by itself resolve the corporate-control question.
- Technology dependencies: Can the customer export data, configurations and audit records in usable formats? What proprietary services would make a move costly or technically difficult?
- Resilience: What happens if a region, supplier, identity system or control plane is unavailable? Has the recovery path been tested, or only described?
The Commission’s framework explicitly combines sovereignty objectives with assurance and scoring. Its public explanation is useful because it moves procurement away from slogans and toward evidence. The Commission adopted a proposal for the Cloud and AI Development Act in June 2026. The proposal remains a legislative proposal in the Commission materials consulted for this article; its current policy overview describes four assurance levels. Do not conflate that proposed EU-wide system with the procurement-specific framework used in the earlier tender. Both move the conversation toward operational evidence, but their status and scope differ. [3] [5]
Turn the framework into a procurement worksheet
For each workload, assign an owner and classify the harm caused by interruption, foreign access or loss of portability. For a related procurement example, see our analysis of OpenAI models entering Google Cloud Model Garden. Then ask the provider for concrete evidence: support-access logs, key-management options, subcontractor dependencies, software-update controls, exit formats and recovery-test results. Separate contractual promises from technical controls, and distinguish “available as an option” from “included in this service configuration.”
A weighted score is useful for comparing offers, but it can hide a critical weakness if the buyer averages across categories. If a public-safety workload cannot tolerate a foreign support dependency, a strong score on several less important dimensions does not erase that requirement. Set pass/fail thresholds for the controls that matter to the workload, then compare the remaining trade-offs.
Sovereignty also has a cost. Operating redundant systems, retaining local expertise and avoiding proprietary dependencies can increase complexity and price. The right goal is not maximal isolation for every application. It is a documented choice that matches the workload’s legal obligations, recovery needs and tolerance for supplier dependence.
The label is less important than the evidence
Cloud providers will continue to describe products with sovereignty language. Buyers should read that as a prompt for due diligence: which specific control does the product add, where does the customer retain authority, and how can that be tested? The EU framework is a helpful public example of structured assessment. It is not a shortcut around architecture review, legal analysis or continuity planning.
Frequently asked questions
Does storing data in the EU make a cloud service sovereign?
Data residency is one dimension. The EU framework also considers operational control, legal exposure, technology dependencies, supply-chain autonomy and resilience. A local data center alone does not settle those questions.
Is the EU Cloud Sovereignty Framework a universal certification?
The Commission developed it for procurement assessment in a specific tender context. Buyers should not treat a score or framework reference as a blanket certification for every service, workload or jurisdiction.
Sources & further reading
- European Commission: Sovereign Cloud Framework explained
- European Commission: Cloud Sovereignty Framework v1.2.1
- European Commission: proposal for the Cloud and AI Development Act
- European Commission: award of four sovereign cloud contracts
- European Commission: Cloud and AI Development Act policy overview
Keep reading
Palantir’s Audit Explorer Logs the Searches Auditors Make. That Is Useful—and Incomplete
The beta makes audit-log review easier and records each search, but its own documentation lists what those search records do not capture.
AWS Step Functions Gives AI Agents a Safer Door Into Existing Workflows
AWS now exposes Step Functions workflows as AgentCore Gateway tools. The agent can choose a workflow and input; the state machine still controls execution.
AWS CodeDeploy RESTART Reuses a Revision, but Your Fleet Still Needs a Drain Plan
CodeDeploy RESTART reapplies an EC2 or on-prem revision under deployment safeguards. See its agent, lifecycle and traffic-drain requirements.
/* Comments */
Comments are offline right now — we reconnect automatically, nothing is lost.