
On this page
A failing check or a merge conflict often turns a nearly finished pull request into a queue item that nobody wants to reopen. GitHub’s Agent Merge can monitor those selected blockers and try to resolve them in the cloud. The useful promise is ongoing maintenance between authoring and review. The risky misreading is that an agent watching the merge box has become an approver.
What the feature watches
Agent Merge is now integrated into GitHub pull requests, extending a capability that GitHub says was already available in the Copilot app and Visual Studio Code. On a pull request, an author can choose Watch and fix and select whether Copilot should address failing GitHub Actions workflows, merge conflicts, or both. When one of those blockers appears, Copilot starts work in a cloud development environment and reports its activity in the pull request timeline. [1] [2]
That scope is intentionally concrete. It is not a general mandate to improve a pull request, rewrite its architecture or decide whether a product change is correct. The agent responds to a blocker the author selected. Teams can also enable it by default for pull requests they create, but the setting still includes switches for the actions it may take.
The feature currently has important boundaries. GitHub Docs require access to Copilot in the cloud through a paid plan and say organization and enterprise policies must allow it. The repository’s Enable automations Copilot policy must also be enabled. Stacked pull requests and pull requests opened from forks are not supported. These are deployment and governance constraints, not edge cases to discover after expecting a bot to act. [2]
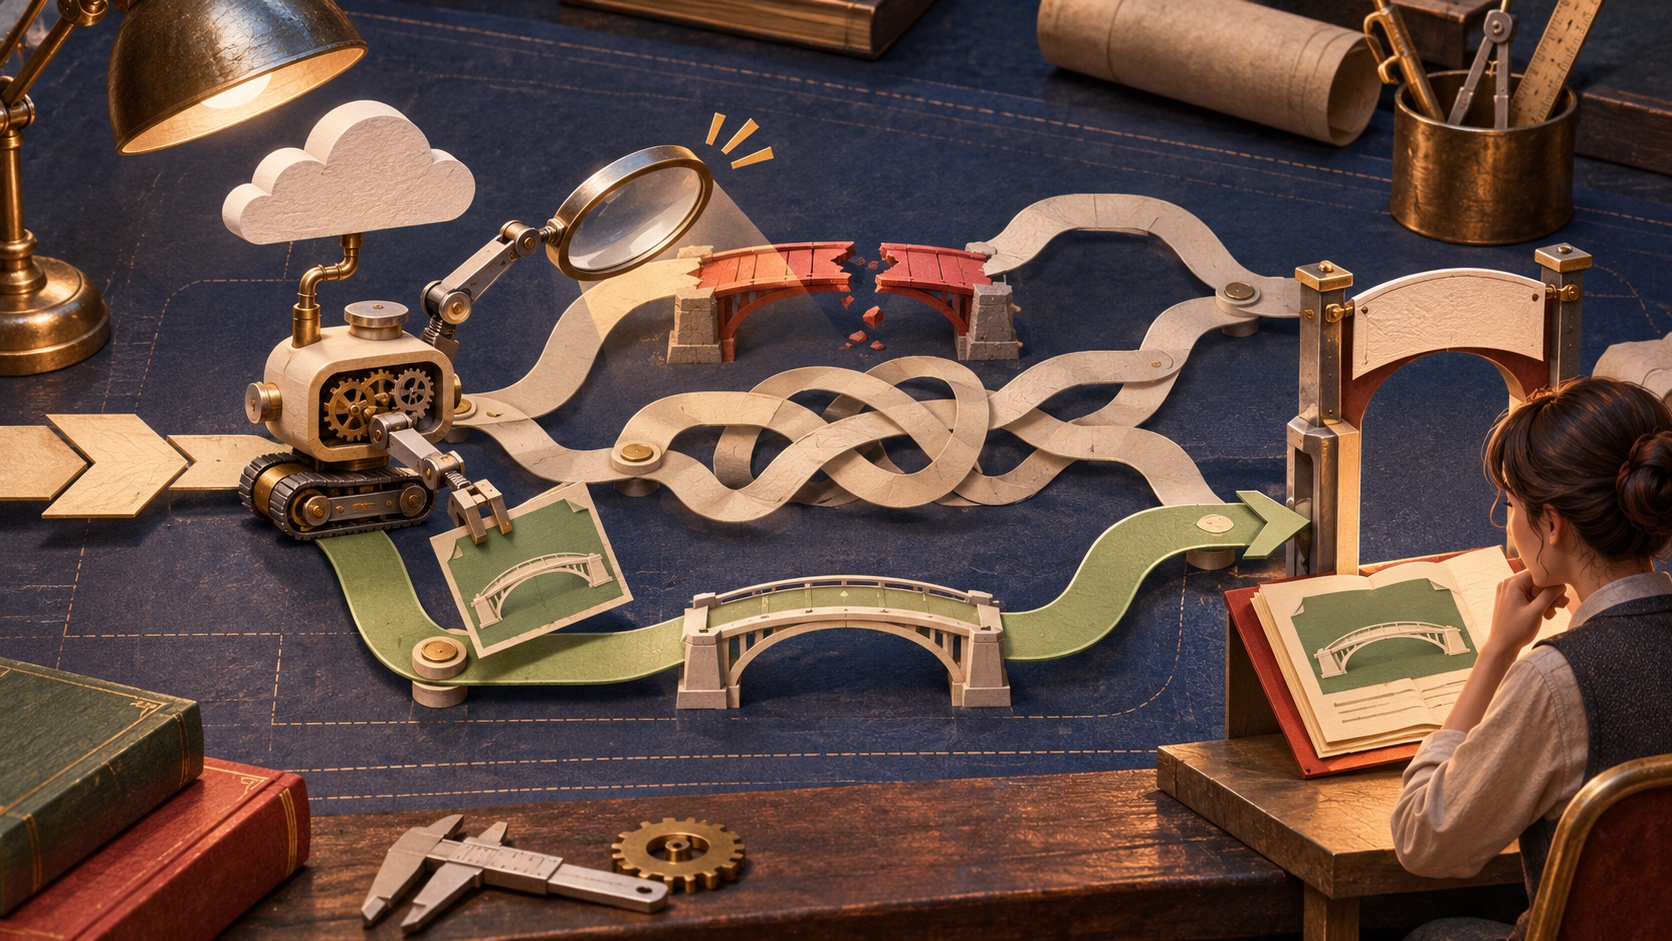
Ready to merge is not approved to merge
GitHub’s documentation draws the distinction clearly: Agent Merge helps get a pull request ready and keep it there, but it does not replace review or repository merge requirements. Its activity should be treated as a proposed code change that can itself introduce a defect. A successful repair run does not establish that the result is safe, correct or aligned with the intended behavior. [2]
Protected branches make this division practical. Repository rules can require reviews, status checks, signed commits or other conditions before a branch accepts a change. Those rules are independent of whether an agent believes it has resolved the current blocker. Keep them attached to the protected branch and verify that the actual check contexts are the ones the team depends on. [3]
Agent Merge can be paired with auto-merge, but that is a composition of two separate systems. Agent Merge works to clear blockers. Auto-merge waits until the configured reviews and checks pass, then merges. GitHub explicitly says enabling Agent Merge does not enable auto-merge. That separation is valuable: one automation can repair a branch while another enforces the repository’s existing merge policy. [2]
Start with a bounded pilot
A sensible pilot uses a repository with a clear test suite and a small group of maintainers. Enable only the blocker type with the most repetitive manual work. Track how often the agent starts, whether the proposed patch fixes the underlying issue, and what new failures it creates. Require a human to inspect the diff and rerun the relevant checks before approving.
For failed workflows, make sure logs do not contain secrets or sensitive customer data that a cloud agent should not see. For merge conflicts, review both sides of the resolution: the result can be syntactically valid while silently discarding intended behavior. Treat the timeline as an audit trail, and make sure maintainers know how to unassign Copilot when a proposed repair is not useful. [2]
If your team already has an unattended coding service, workload identity and usage attribution matter too; our guide to GitHub Copilot’s organization-owned server authentication explains that separate access boundary. And if Actions itself is a source of queue pressure, see our explainer on GitHub’s expanded multi-cloud runner pool.
The agent can reduce waiting, not accountability
The best use of Agent Merge is to shorten the time between a detectable blocker and a reviewable repair. That can help maintainers focus on code intent instead of repeatedly restarting the same troubleshooting loop. The standard for merging should remain unchanged: reviewers inspect the proposed patch, automated checks pass, and repository policy is satisfied. Delegating the repair does not delegate responsibility for the change.
Frequently asked questions
What does Agent Merge do?
Agent Merge watches a pull request for selected blockers, currently failed GitHub Actions workflows and merge conflicts, and starts Copilot work in a cloud development environment to address them.
Does Agent Merge merge code automatically?
No. Agent Merge can prepare a pull request to meet merge requirements, but it does not replace review or those requirements. Auto-merge is separate and merges only after configured checks and reviews pass.
Which pull requests are currently unsupported?
GitHub Docs say Agent Merge does not support stacked pull requests or pull requests opened from a fork. Availability also depends on a paid Copilot plan and applicable organization and repository policies.
Sources & further reading
Keep reading
Copilot Fusion Makes the Model Picker a Routing Policy
Copilot Fusion routes coding tasks across models and execution patterns. Teams still need visibility into access, output and cost.
Copilot Can Generate Images in Your Project—Treat the Result Like Any Other Asset
Copilot’s image-generation preview keeps prompts, review and saved assets in one coding session. Teams still need quality and usage controls.
ANSI’s New AI Register Could Make Claims Easier to Compare—If Buyers Read the Evidence
ANSI’s AI Register will catalog declarations, attestations, and independent assessments; a listing will not certify or endorse a system.
/* Comments */
Comments are offline right now — we reconnect automatically, nothing is lost.