
On this page
A security patch in a language runtime matters only when it reaches the program that performs certificate verification. For Go services, that usually means identifying the toolchain, rebuilding the binary and redeploying it—not merely updating a builder image and assuming an already-produced artifact changed.
What the release says
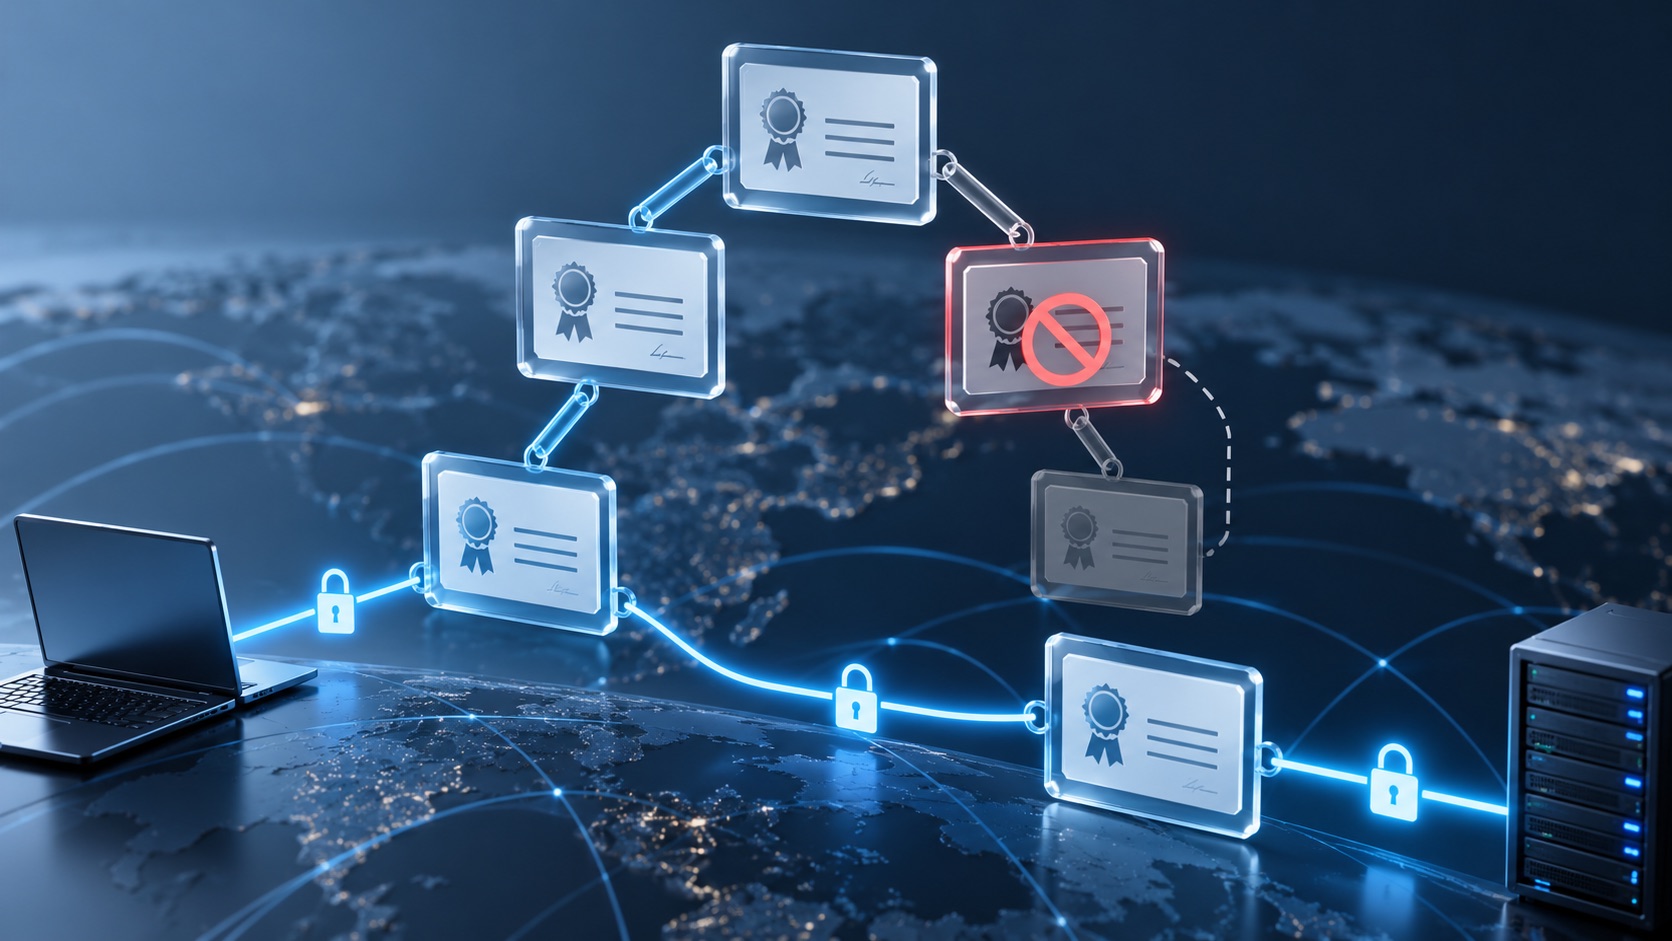
Go’s release history lists Go 1.27.3 and Go 1.26.10, released Oct. 19, as containing security fixes to crypto/x509. The upstream issue describes the mitigation: Verify filters out certificate chains containing a small set of intermediates, preventing those chains from being returned to the caller. The issue recommends upgrading promptly and tracks the change as CVE-2026-111943. [1] [2]
The wording is deliberately narrow. The public release record identifies a targeted change to certificate-chain verification; it does not describe a wholesale removal of a root certificate or a general change to all TLS connections. The issue title and patch tracker are enough to establish the action without speculating about the authority beyond what the project has published.
The Go 1.27 backport tracker records the security label and the release-branch change titled “crypto/x509: distrust a handful of intermediates.” Go’s release history is the most direct guide to the available fixed versions, so check it again when planning an upgrade across supported branches. [3]
Find the component that actually verifies certificates
Start with the Go versions used to compile and ship each service. Inspect module build images, release pipelines, container manifests and artifact provenance. Then identify applications that rely on Go’s crypto/x509 for peer or server certificate verification, including code that builds custom root pools or performs explicit verification.
The standard library is compiled into Go binaries. Updating the compiler in a build container does not retrofit an artifact that has already been built. Rebuild affected programs with Go 1.27.3 or 1.26.10, depending on the version line your organization uses, and redeploy through the normal release process.
Do not assume every service has identical exposure. Some applications use different runtimes or delegate certificate handling to another component. Others may have custom trust roots or verification callbacks. Inventory by verifier and deployment artifact rather than by repository language label alone.
Test trust paths after the upgrade
A certificate-chain change can surface as a failed connection for a client or service that encounters an affected chain. Include representative endpoints and intermediates in a post-upgrade test. For externally managed dependencies, check actual handshake behavior from the same runtime environment as production. For internal PKI, validate the intended chain and confirm that any replacement certificate is provisioned through the normal trust-management process.
Keep the test focused on verification outcomes and logs. Avoid shipping custom workarounds that re-accept a chain rejected by the updated library unless a security review has explicitly approved a narrow alternative. If a connection fails, record the Go version, peer chain and verifier configuration needed to diagnose it, while protecting any private material.
Close the release loop
A practical patch checklist is short: locate the toolchain, identify binaries that use Go certificate verification, rebuild on the fixed patch line, redeploy, and exercise relevant TLS paths. Track the completed artifact version—not only the base image tag—so teams can distinguish a patched build from an unchanged binary.
Go’s patch is a reminder that trust policy can change inside a library even when application code does not. The operational unit is the shipped artifact. A verified rebuild and a tested certificate path are the evidence that the fix reached production.
Frequently asked questions
Which Go versions include the crypto/x509 security update?
Go's release history lists Go 1.27.3 and Go 1.26.10, both released Oct. 19, 2026, as including crypto/x509 security fixes. Check the official release history for the current supported patch line before upgrading.
Does updating a Go builder image patch already-built binaries?
No. Standard-library code is compiled into Go applications. Rebuild and redeploy affected binaries with the fixed toolchain, then test certificate paths used by your services; changing only the build image does not rewrite an artifact already produced.
Sources & further reading
Keep reading
Claude Structured Outputs on Bedrock Can Enforce Shape, Not Business Truth
Bedrock adds schema-constrained Claude output, but route and model support vary and valid JSON still needs domain validation.
GitHub’s SSH Brownout Starts Nov. 4: Check the Client Before Replacing Keys
GitHub is phasing out older SSH signatures and key exchange; distinguish RSA key files from the SHA-1 signature algorithm before changing access.
OpenAI’s New Coding Benchmark Tests Whether Models Can Preserve Legacy Behavior
MultiLangBench measures SQLite-compatible engines across 20 languages, but its test design shows why benchmark wins are only a migration screen.
/* Comments */
Comments are offline right now — we reconnect automatically, nothing is lost.