
Gemini 4 Carbon Is Limited to Trusted Cyber Defenders—for Now
Gemini 4 Carbon targets long-horizon engineering and cybersecurity. Its restricted rollout and vendor-reported benchmarks deserve careful interpretation.
On this page
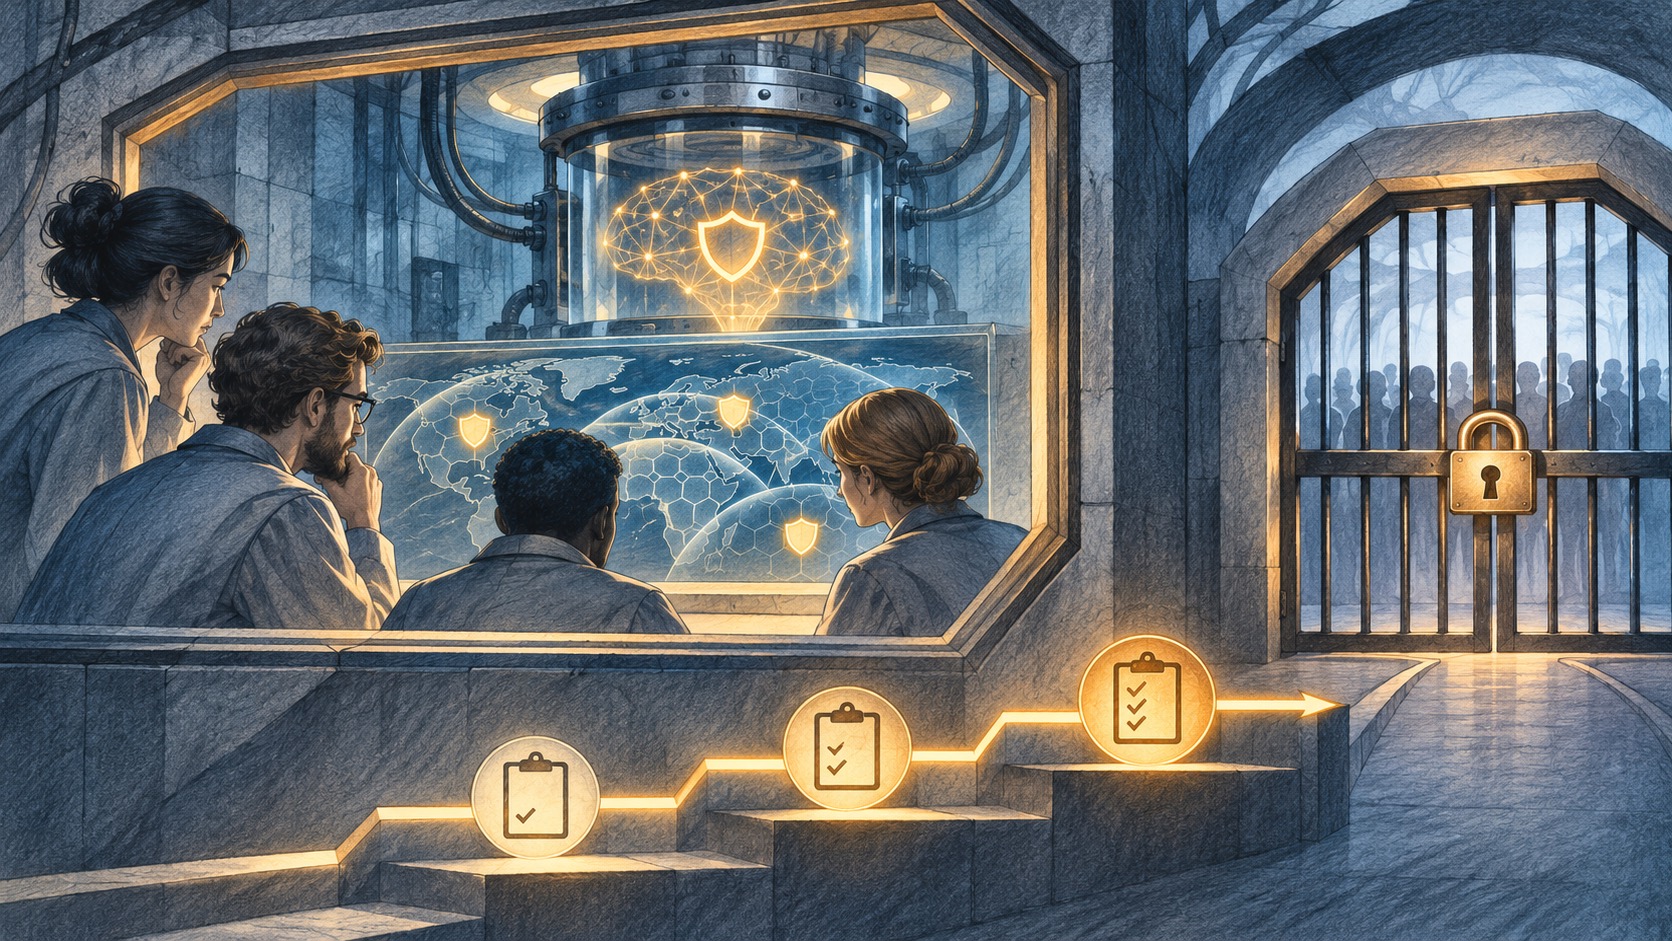
The headline capability is also the reason Google is not opening the model to everyone at once. Carbon is designed for sustained software engineering and cybersecurity work, including vulnerability discovery, validation and remediation. Google says it is initially providing access to selected cyber defenders and trusted partners while it continues testing safeguards. That staged rollout is a deployment choice, not proof that the model is already safe for arbitrary security operations. [1] [3]
What Google says Carbon is built to do
Google describes Carbon as a continuation of Gemini 4 Argon, with work focused on longer-running engineering tasks and cybersecurity defense. The announcement says internal teams used it on multi-step work such as finding and fixing subtle bugs in large codebases and low-level systems. It also reports scores on benchmarks for vulnerability discovery, exploit validation and patching. The company says it will use a staged partner program to gather feedback and iterate on safeguards before a broader product launch. [1]
Those statements describe the vendor’s goals and results. The post includes its own benchmark scores and internal comparisons, including runs without guardrails. Those figures can help explain why the model matters, but they are not independent audits. Benchmark performance also does not tell a security team how the model behaves with its code, policies, data or threat model. [1]
Why the restricted rollout matters
A model that can inspect code and help develop patches may be useful to defenders, but the same underlying capabilities can be misused. Restricting early access lets a provider gather feedback from selected users while evaluating safeguards. The tradeoff is that outsiders cannot yet independently reproduce the workflow or determine how broadly the performance claims apply.
Google says the launch is engaged with the U.S. government’s voluntary pre-release testing process and uses multiple safeguards, including training, misuse defenses and prompt-injection resilience. Those are company descriptions, not an assurance that every risk is eliminated. Teams should not interpret “cyber defense” labeling as a permission to connect a model to sensitive repositories or autonomous response actions without their normal controls. [1]
What security teams can do now
If your organization is not in the initial cohort, there is no public production endpoint to plan around based on this announcement. Keep the model off critical workflows until eligibility, terms, product surfaces, data handling and independent evidence are clear. If access becomes available, start with a sandboxed evaluation against a bounded task and a reviewed, non-sensitive codebase.
Define success in advance: Are you measuring precision of findings, time to reproduce a flaw, patch correctness, or the human effort required to validate output? Keep a record of prompts, model version, tool permissions and any external actions. Require a human reviewer to validate code changes and reproduce security findings before they enter a backlog or release branch. Do not give a preview system credentials to production infrastructure simply because the use case is defensive.
Google says Carbon is expected to become available to developers, businesses and consumers later. Until then, the practical signal is the rollout design: high-capability systems are being tested with selected partners before broader release. Readers should track the independent evidence and deployment conditions as closely as the benchmark headline. This follows the rollout story in our Gemini 4 Argon long-running-agent analysis; for a contrasting safety-governance example, see OpenAI’s Astra capability threshold. [1] [2]
Frequently asked questions
Can developers access Gemini 4 Carbon now?
Google announced a staged rollout to a subset of cyber defenders and trusted partners through its Fairwind Program. Broader availability to developers, businesses and consumers is described as forthcoming, not generally available today.
Are the published security benchmarks independent?
Google reports benchmark scores and internal results in its announcement. Treat those as vendor-reported claims until independent evaluations provide comparable methods and results.
Sources & further reading
Keep reading
Apple Opens Siri AI Actions to Developers
Apple’s developer preview lets apps expose actions to Siri through App Intents. Shipping, policy, age and regional limits still shape what teams can build.
Google Dreambeans Turns Connected Apps Into a Morning Story Feed
Dreambeans is an experimental Google Labs app that turns selected Google app data into daily stories. Its usefulness depends on what people connect.
A Bigger AI Cache Can Save GPU Time—If the Network and Reuse Rate Cooperate
Supermicro, IBM and NVIDIA proposed persistent KV-cache storage for long prompts. Their headline speedup is a vendor test, not a universal inference result.
/* Comments */
Comments are offline right now — we reconnect automatically, nothing is lost.