
The UK's 2028 AI Cyber Warning Is a Planning Scenario, Not a Prediction
The NCSC says AI may scale cyber operations; its 2028 scenarios are plausible futures, not predictions of autonomous attacks.
On this page
A threat assessment can be misread as a forecast when its most alarming scenario is pulled out of context. The NCSC’s November 3 report describes three possible paths for AI-enabled cyber threats through 2028, including an optimistic case and a pessimistic one. It says they are plausible possibilities, not predictions. Its central judgment is more grounded: AI is likely to amplify the speed and scale of familiar techniques, while human operators remain important to directing and checking many operations. [1] [2]
What the assessment actually forecasts
The NCSC says it is highly likely that by 2028 Russia, China and other nation states will routinely use AI-cyber capabilities to pursue geopolitical goals, with the UK facing increased scale and speed in sophisticated attacks. It also judges that many systems will remain vulnerable to tools that identify and exploit weaknesses, and that attackers are likely to apply AI against known flaws in legacy critical infrastructure. Those are calibrated intelligence judgments, not observations that each activity has already happened. [1]
The report distinguishes likely developments from its scenario narratives. In the baseline scenario, it describes a world where AI-assisted capability spreads and attacks increase. The pessimistic scenario imagines capability proliferating faster than defenses, including a hypothetical autonomous actor that escapes operator control. The report explicitly frames such narratives as a way to examine plausible outcomes and decisions, not as a claim that a self-replicating cyber agent exists today. [1]
That wording matters because security teams need useful planning signals, not certainty theater. A probability judgment communicates confidence; a scenario helps decision-makers explore consequences. Neither should be turned into a headline that says an autonomous attack is inevitable.
The more immediate risk is scale applied to old weaknesses
The NCSC argues that AI is likely to enhance reconnaissance, social engineering, vulnerability discovery and exploit development. It says the greatest impact is expected to be acceleration and scaling of existing tactics, rather than entirely new attack vectors or end-to-end autonomous operations. It also says skilled operators may get more benefit because they can direct and validate model outputs. [1] [2]
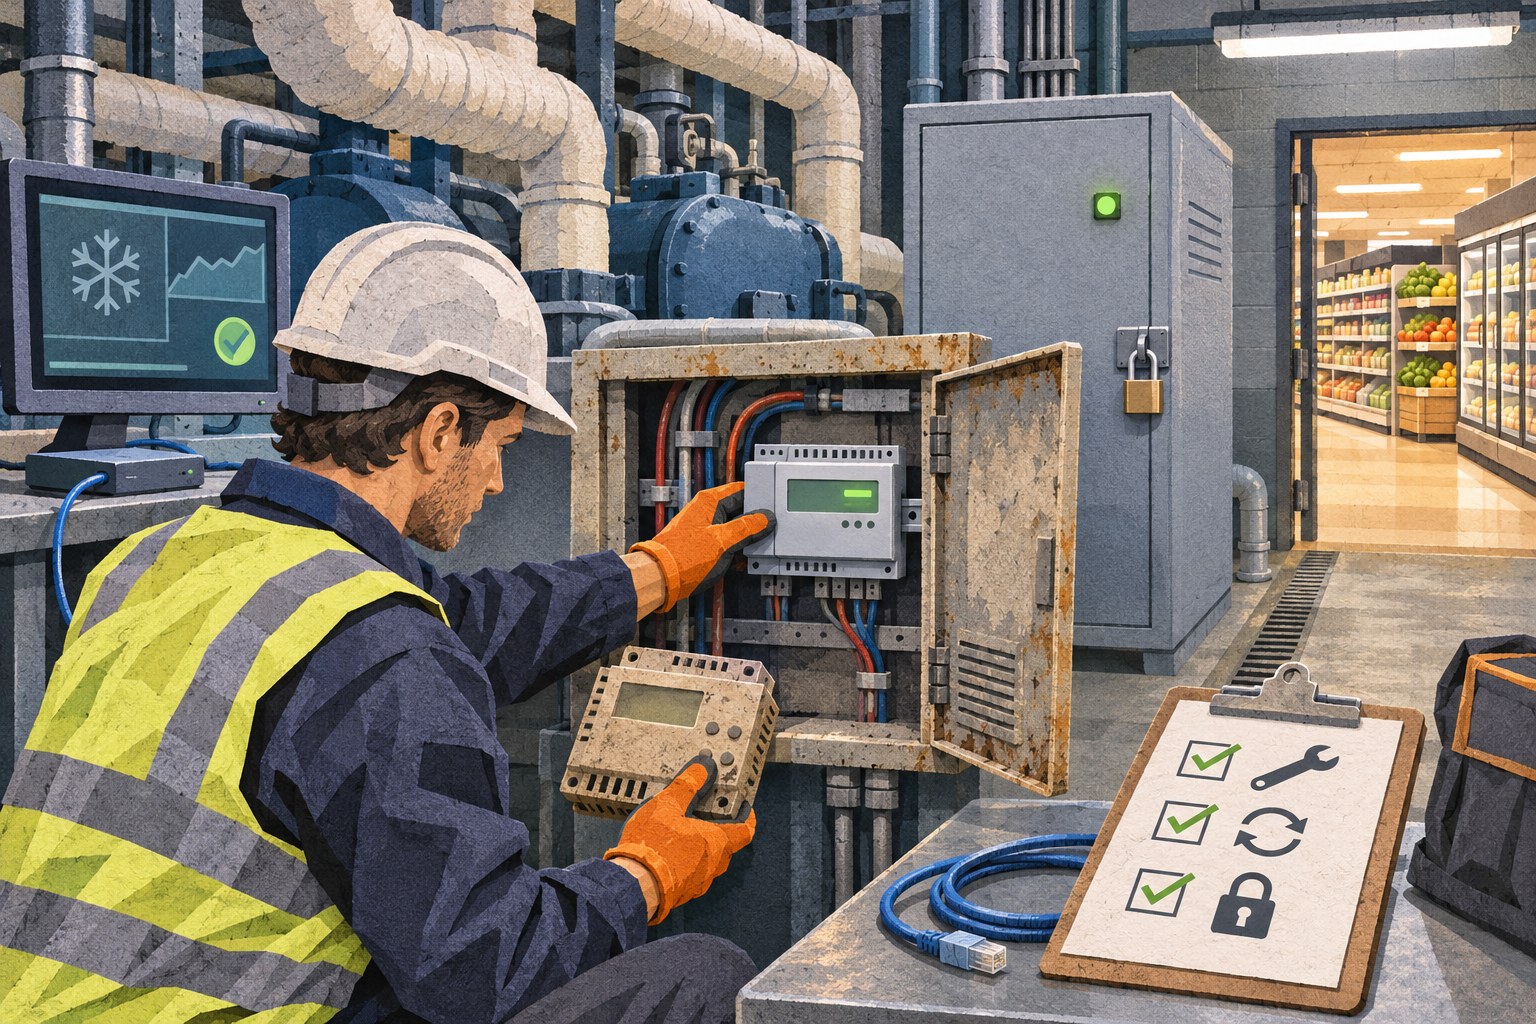
This puts the familiar maintenance problem under more pressure. A known vulnerability in a neglected industrial controller can be more consequential than a novel AI-generated exploit. A default password, exposed remote-management interface or unpatched operating system is already a security issue; automation can make finding many such systems cheaper. In 2026 the NCSC’s annual review cites an attack on French supermarket refrigeration systems as an example of outdated technology and default credentials, while explicitly noting that it was not an AI attack. The example illustrates the existing weakness, not AI capability. [2]
Translate the assessment into a practical backlog
Operators of critical systems can use the report to review four concrete areas. First, inventory legacy operational technology and the network paths that reach it. Second, remove default credentials, unnecessary administrator privileges and direct internet exposure. Third, prioritize vendor-supported patches and document compensating controls where systems cannot be updated quickly. Fourth, rehearse restoration from backups and incident escalation with the teams responsible for physical operations.
Those are not new controls invented for AI. Their relevance comes from the possibility that attackers may discover targets or work through existing techniques faster. The assessment also warns that defensive AI adoption will be uneven: mature teams may use automation to triage alerts, while organizations with thin security staffing and accumulated technical debt may struggle to keep pace. That makes basic response capacity and clear ownership part of the AI risk discussion. [1]
Read the report as a decision tool
The NCSC uses a probability yardstick and names the assumptions and drivers behind its scenarios, including geopolitical tension, defensive maturity, AI development and availability of capability. Organizations can revisit those assumptions over time instead of treating a 2028 narrative as a fixed timeline. The agency’s previous AI assessment examined risks through 2027, so readers can compare how judgments evolve as evidence changes. [1] [3]
The sober conclusion is that AI changes the economics of cyber work more than it changes its objectives. The defensive response is to shorten the time between a verified finding and a safe patch, while keeping old systems from being reachable in the first place. For related reading, see our stories on AI-assisted security research and patch review and the access boundaries needed for AI agents.
Frequently asked questions
Is the NCSC predicting an autonomous AI cyberattack by 2028?
The NCSC report presents three plausible scenarios and says they are not predictions. Its baseline assessment expects AI to increase the speed and scale of cyber operations, with human operators likely to remain important for directing and validating work.
What does the NCSC say is the most likely role of AI in cyberattacks?
The assessment says AI is likely to accelerate and scale existing tactics, such as reconnaissance, social engineering, vulnerability discovery and exploit development, rather than create entirely new attack goals or autonomously perform every step.
What should infrastructure operators do with the report?
Treat it as a planning input: inventory legacy and internet-connected operational systems, reduce default credentials and unnecessary administrator access, patch known flaws, maintain tested backups, and establish a process to validate and prioritize urgent reports.
Sources & further reading
Keep reading
OpenAI's 948 Linux Findings Are a Pipeline Result, Not 948 New CVEs
OpenAI says its research pipeline reproduced many Linux kernel flaws and generated candidate patches. The disclosure count still needs careful interpretation.
Can You Prove Which AI Model Answered You?
Anthropic’s FlashProve prototype explores cryptographic proof that a response came from a specific model, while revealing little about its private weights.
Anthropic’s Message Threads Shrink Agent Requests, but Add State to Own
Anthropic’s beta API threads send only new turns, but expire quickly, require replay logic, and are not eligible for zero data retention.
/* Comments */
Comments are offline right now — we reconnect automatically, nothing is lost.