
Cloud Armor’s CDN Edge Rules Can Filter Before Cached Content Is Served
A November Preview adds ASN, threat-intelligence and HTTP filtering to Cloud Armor edge policies for Cloud CDN. The cache boundary changes where policy applies.
On this page
A cached response may never reach the application backend. That is good for latency, but it changes where a security rule needs to run. Google’s November 16 Cloud Armor update expands filtering options for edge policies serving Cloud CDN cache services, with ASN, Network Threat Intelligence and HTTP filtering now in Preview. The policy sits upstream of the cache, allowing a request to be evaluated before a stored response is delivered. [1]
Why the cache changes the enforcement point
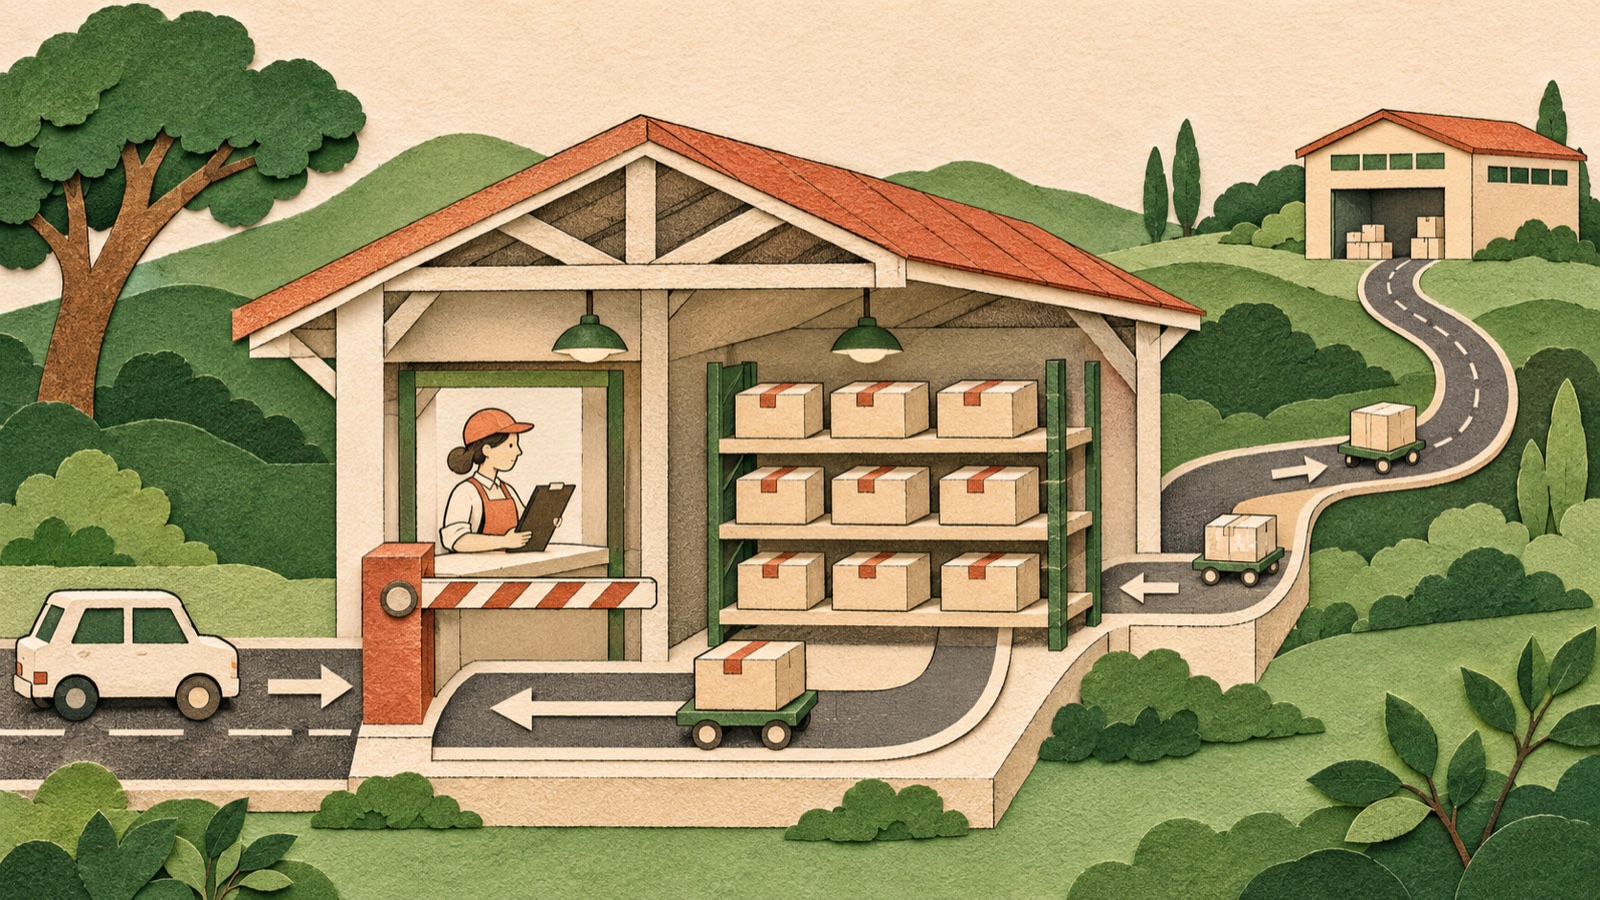
A CDN can serve an object directly from cache. If a policy only runs at the backend, a cache hit may bypass the application path where that policy is enforced. Cloud Armor’s documentation describes edge security policies as filtering and access control for content in cache, evaluated before the request is served from Google’s cache. When edge and backend policies are attached to the same backend service, the backend policy applies only to cache-miss requests that passed the edge policy. [2]
That creates a clear two-layer model. The edge rule decides whether a request may reach the cached-content path. If the requested object is absent or stale and the request proceeds toward the backend, backend policy provides another evaluation point. The layers are complementary; they answer different questions at different places in the delivery path. This also means a rule configured at one point should not be assumed to apply identically at the other.
The November feature matters because the edge policy can now use additional signals for Cloud CDN edge cache services. The release note identifies ASN, Network Threat Intelligence (NTI) and HTTP filtering, and marks the capability Preview. It does not mean all Cloud Armor features are now available at the edge or that all CDN configurations behave identically. [1]
Three signals, three limits
An ASN is useful as a network-level grouping. It can help identify traffic associated with a particular network operator or hosting range, but it is not a user identity. A mobile carrier, corporate proxy or shared cloud provider may serve many legitimate users. A blanket block can therefore turn a coarse signal into collateral damage. Use targeted conditions, observe matches and keep a narrow rollback path.
Network Threat Intelligence is a provider-maintained signal. It may help operators respond to known threat sources, but its value depends on its documented scope, update behavior and false-positive profile. Review the relevant product documentation and test the policy against your own traffic before enforcing it broadly. The release note announces the signal’s availability; it does not publish an independent effectiveness measurement.
HTTP filtering lets policy inspect request attributes. The exact fields and semantics supported by the Preview feature should be checked in current Cloud Armor rule documentation before translating existing backend rules. An edge policy supports a subset of parameters compared with backend policy, so policy portability cannot be assumed. [2] [3]
Preview rollout: map first, enforce second
Before configuring a rule, sketch the actual path for one representative request: client, load balancer, edge policy, cache hit or miss, backend policy, then application. Include identity-aware components where used. Google documents that edge policies run before IAP; a request blocked at the edge will not reach IAP to receive its sign-in flow. That ordering can affect what a user experiences and which logs contain the decision. [2]
Then test candidate rules in a non-production service or observation mode supported by the product. Compare match counts with known traffic, especially shared NATs, corporate egress and mobile networks. Check the behavior of cache hits and misses separately, and confirm that denied traffic is visible in the expected telemetry. Start with one narrow rule, a named owner and a rollback plan. Do not promote a Preview feature into a broad policy based only on a successful configuration command.
Teams should also separate content sensitivity from origin protection. If content is already public and cached globally, an edge policy may be the place to restrict delivery. If the application needs per-user authorization, a network location rule is not a substitute for identity-aware checks. Cache keys, signed access and backend authorization remain separate design concerns and should be tested with the intended request path.
What to verify before relying on it
Confirm that the protected service is among the supported Cloud CDN edge cache configurations and that the edge policy scope is correct. Check which match attributes are supported in Preview, whether existing rules can be translated, and which request stages emit logs. Validate both allowed and denied cache hits and misses. Track false positives and user impact before expanding coverage.
Finally, keep the maturity label visible. For more context, see common cache failure modes and how CDNs fit into web infrastructure. Preview availability is an invitation to evaluate the feature, not proof that it is ready for every production policy. The most important architectural takeaway is durable: cached delivery creates an enforcement boundary upstream of the origin. Put controls where the content is actually served, and preserve backend checks for requests that continue past the cache.
Frequently asked questions
What did Cloud Armor add for Cloud CDN edge policies?
Google's November 16, 2026 release note says globally scoped edge security policies for Cloud CDN edge cache services now support ASN, Network Threat Intelligence and HTTP filtering in Preview.
Do edge policies replace backend security policies?
No. Google documents that edge policies can screen requests before cached content is served, while backend policies apply to cache misses that pass the edge policy. They can provide separate layers.
Does an ASN rule identify an individual user?
No. An Autonomous System Number identifies a network operator's routing domain, not a person or a reliable individual identity. Treat it as a coarse network signal and validate its operational impact.
Sources & further reading
Keep reading
Cloudflare vs AWS and Azure: Compare Execution Boundaries, Not Labels
A grounded comparison of edge Workers, regional cloud functions and CDN paths—focused on runtime, networking, state, operations and workload fit.
Compiler-Built Device Graphs Target the Cost of Recording GPU Work
Modular says compiling a known execution graph can avoid runtime capture overhead. Here is what its claim means, where graph replay helps, and what to measure.
.NET 11 Is Here: Choose the Support Track Before You Retarget
.NET 11 launched as a two-year STS release while .NET 10 remains LTS. Map support dates, target frameworks, SDKs, images and runtime changes before upgrading.
/* Comments */
Comments are offline right now — we reconnect automatically, nothing is lost.