
Git’s Six November Fixes Make Recursive Clones a Supply-Chain Checkpoint
Git 2.56.1 and maintenance releases address six vulnerabilities. Recursive clones deserve attention, but upgrading Git alone does not vet repositories.
On this page
A repository is more than a collection of source files when a tool follows its submodules, parses patches or imports repository data. Git’s November update fixes six vulnerabilities in those paths and related operations. The highest-value response is twofold: update the Git implementation that actually runs in developer and CI environments, then identify automation that recursively fetches repositories from outside your trust boundary. [1]
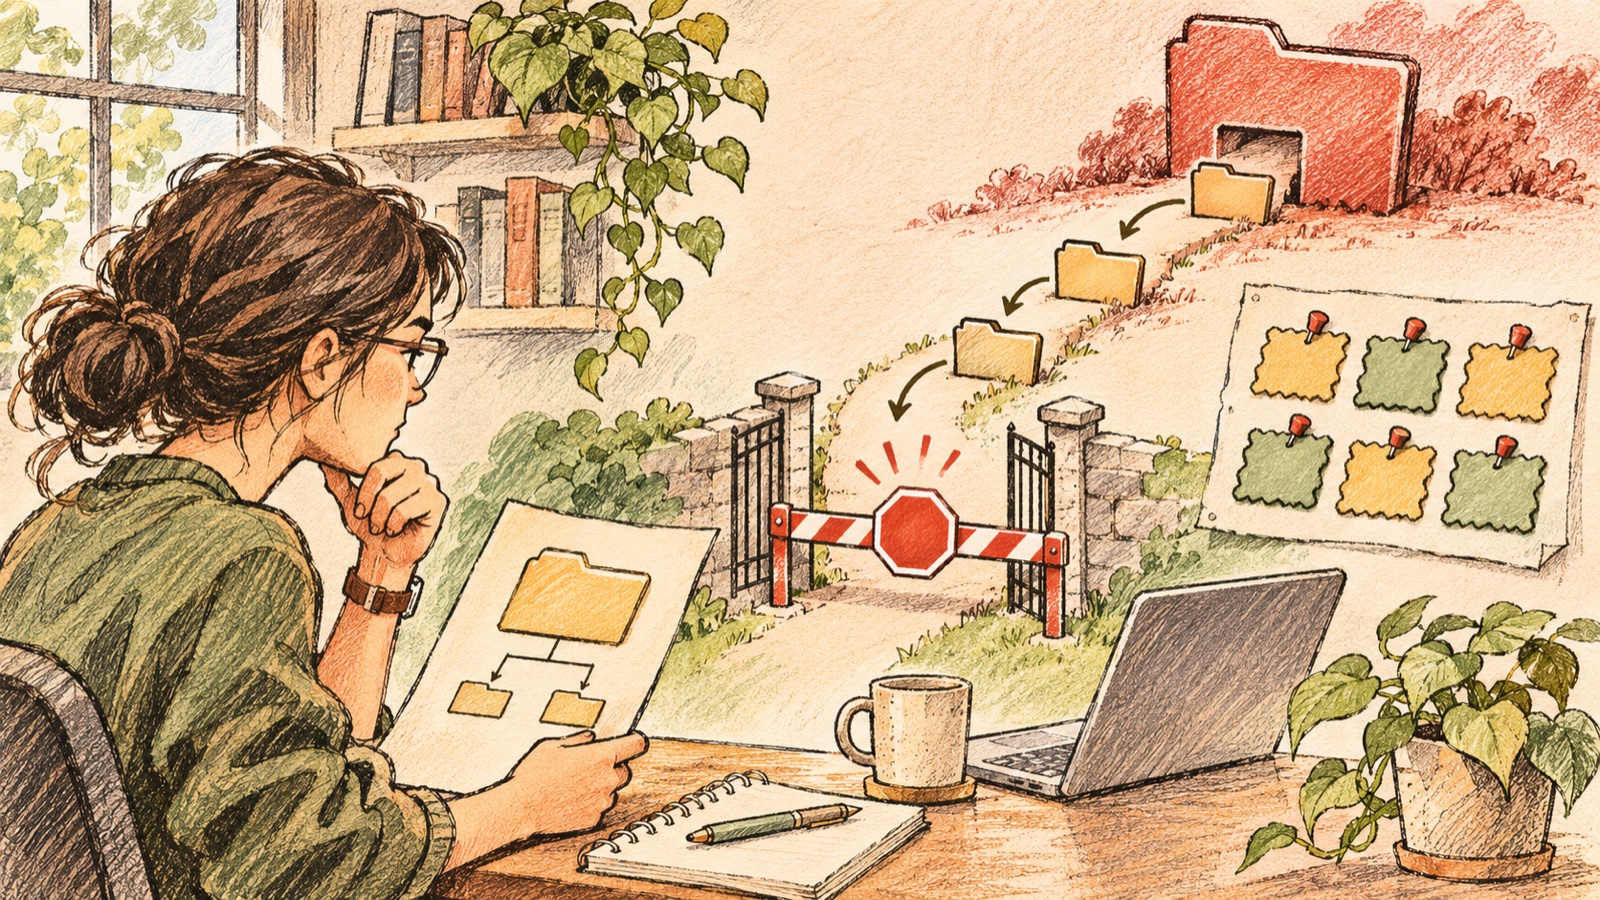
Six fixes, several different paths
GitHub’s November 10 notice groups six vulnerabilities affecting recursive clones, reference handling, merges, binary patches and imports. The patched releases it lists are Git 2.56.1, 2.55.1, 2.54.1, 2.53.1, 2.52.1, 2.51.3 and 2.50.2. The exact maintenance version depends on the series installed; the important operational detail is to verify the actual executable rather than assuming a developer’s package manager updated every copy. [1] [2]
The recursive-clone issue is especially relevant to supply-chain workflows because a top-level repository can direct Git to fetch nested repositories. GitHub’s advisory describes a remote-code-execution risk involving a crafted repository and recursive submodule processing. Its conditions matter: this is not an assertion that opening every repository in a text editor triggers the issue. But build agents, IDE integrations and setup scripts often automate more than a plain git clone, which is why the recursive path deserves an inventory.
The other issues reinforce that Git’s attack surface includes multiple parsers and operations. Malformed references, merge inputs, binary patches and import streams are not equivalent user journeys, so one generic control such as “only allow HTTPS” cannot address all of them. The version update is the common remediation; the operational review should follow each team’s real usage patterns.
Patch the executable that runs
Start by listing Git versions on developer machines, build agents, hosted runners, containers and internal tools. Check whether an application bundles its own Git library or executable. GitHub specifically recommends updating applications that bundle Git; updating the system package may leave an embedded copy unchanged. Confirm the installed version in the environment where repository operations execute, including long-lived runners that do not rebuild automatically. [1] [3]
Next, locate recursive acquisition. Search CI and setup configuration for submodule initialization, recursive clone flags, IDE checkout helpers, dependency bootstrapping and scripts that pull user-supplied repository URLs. Prioritize environments that run such operations with broad credentials, writable workspaces or access to deployment secrets. Reduce permissions for repository-fetch jobs and separate untrusted checkout from privileged release steps. Those are general defense-in-depth practices, not a claim that the advisory requires a particular CI setting.
If you cannot upgrade immediately, constrain the specific risky workflow while you schedule remediation: avoid recursively fetching untrusted repositories in a privileged runner, validate sources and use an isolated environment. Do not treat an allowlist of hosts as sufficient by itself; a trusted hosting service can carry an attacker-controlled repository. Keep the version exception visible, assigned and time-bounded.
A safer intake path for nested repositories
For external code, record who requested the dependency, which repository and revision are expected, and whether submodules are necessary. Prefer pinned revisions over moving branches for repeatable builds. Review submodule URLs and configuration before allowing automation to fetch them, and ensure the fetch step cannot access deployment credentials. A disposable checkout with restricted network and filesystem access can limit what an unexpected repository operation touches.
These measures do not replace the patch. They address different failure modes: a fixed Git avoids the known vulnerabilities; least privilege limits impact if repository content or another tool remains malicious; pinning and review improve traceability. A repository can still contain dangerous build instructions, package hooks or scripts even when every Git component is current.
A practical response checklist
- Inventory Git versions and identify bundled copies.
- Upgrade each environment to its applicable patched release and verify the running version.
- Find automation that recursively checks out external repositories or processes patches and imports.
- Restrict credentials and isolate untrusted fetch/build work from release environments.
- Keep repository provenance and pinned dependency revisions reviewable.
The notice is a reminder that developer tooling is part of the software supply chain. For more context, see GitHub Actions dependency controls and a recent Python supply-chain compromise. Teams should respond promptly, but proportionately: patch Git, review the specific operations they automate, and keep ordinary repository review and isolation controls in place. [1]
Frequently asked questions
Which Git versions contain the November 2026 fixes?
GitHub lists Git 2.56.1 and backports 2.55.1, 2.54.1, 2.53.1, 2.52.1, 2.51.3 and 2.50.2. Use the patched release for the maintenance series you operate.
Is every git clone command affected the same way?
No. The highlighted recursive-clone issue involves cloning a repository with submodules and the recurse-submodules behavior. Exposure depends on how repositories are acquired and which Git build performs the operation.
Does upgrading Git make an untrusted repository safe?
No. The update fixes known Git vulnerabilities, but repositories can still contain malicious build scripts, dependencies or other behavior. Keep review, sandboxing and provenance checks in place.
Sources & further reading
Keep reading
AI Agents Proved Signal Properties Down to Machine Code. The Specification Still Needs You
AlphaProof Code connects Lean proofs to libsignal’s compiled binary. What it proves, what remains trusted, and how teams can use the pattern.
Managed Security Across Tenants Needs More Than a Single Sign-In
Microsoft says granular delegated access for Sentinel and Defender XDR is generally available in its Defender portal. Customer-approved scope remains essential.
GitHub Secret Scanning Adds Cloudflare Access Tokens. What It Catches
GitHub now detects Cloudflare Access service tokens in repositories. Treat detection as a safety net, then rotate exposed credentials and review their scope.
/* Comments */
Comments are offline right now — we reconnect automatically, nothing is lost.