
The LiteLLM 1.107.0 Attack Ran at Python Startup. Check Environments, Not Just Imports
The compromised LiteLLM release used Python startup hooks, so affected environments could execute code without importing it. Here is a response sequence.
On this page
A dependency compromise is easy to underestimate when the affected library appears unused. The LiteLLM 1.107.0 incident changes that calculation: investigators say the poisoned release could execute code during normal Python startup. An environment that installed the package might therefore be at risk even when its application never imported LiteLLM’s API.
What happened
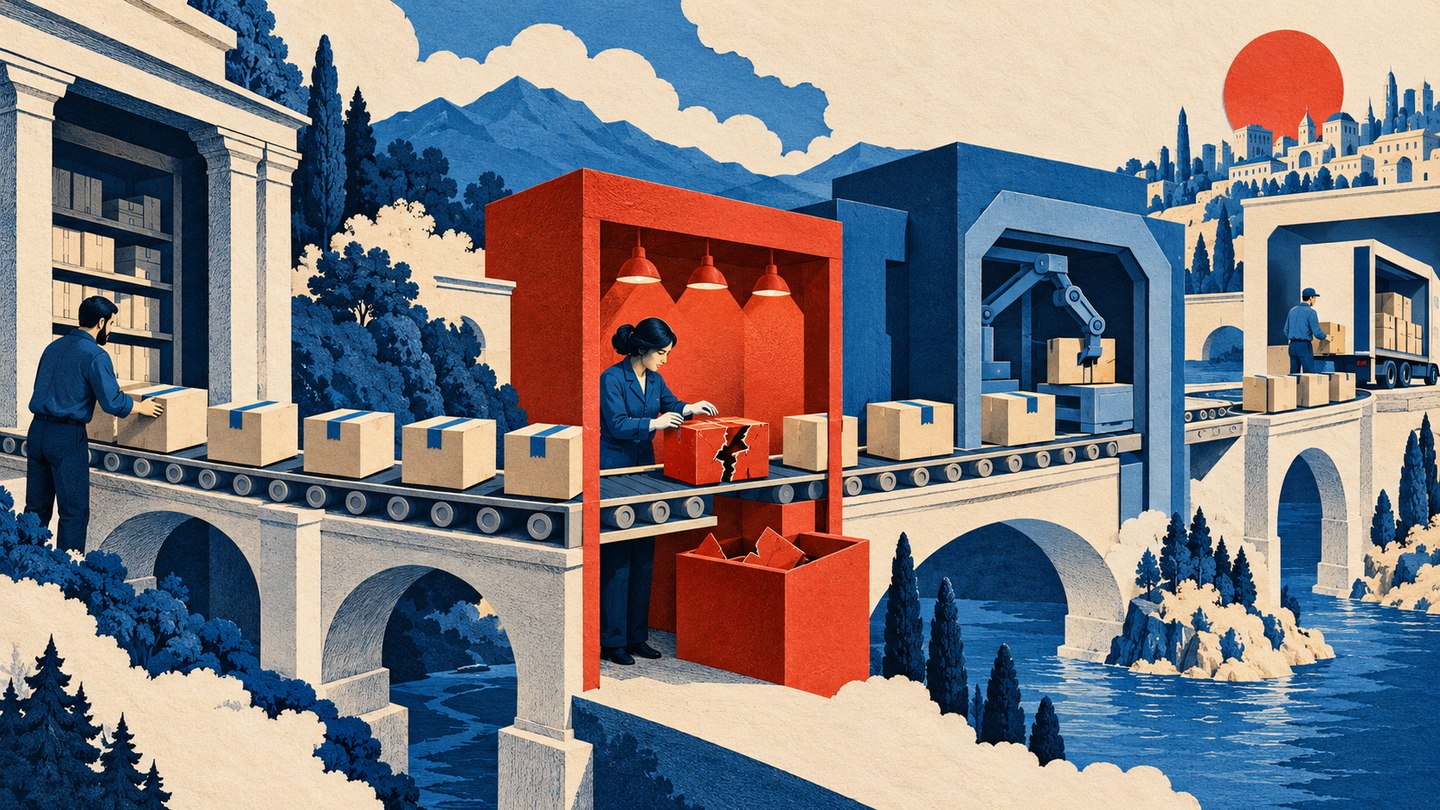
LiteLLM says attackers altered a release workflow and pointed it at a lookalike repository before publishing the compromised version and images. The project’s investigation describes exposed credentials, access to an internal deployment and subsequent changes to release automation. Its October 23 post says a previously exposed platform key had not been revoked; the team describes that key as enabling access to an owner-level GitHub CLI OAuth token. These are the maintainers’ findings and account of the attack chain. [1] [2]
Microsoft independently analyzed the package and described Python startup files that could launch credential collection without requiring an application to import LiteLLM. The targeted material included developer, cloud, browser, SSH and AI-application credentials. Microsoft notes that the release was distributed through PyPI and official container images, widening the set of environments to inspect. [3]
JFrog and CERT-In also published incident analyses. Their coverage supports treating the event as a software supply-chain compromise affecting the named release, while precise affected systems depend on what was installed or executed and on the environment’s available credentials. The incident is not proof that every LiteLLM deployment was compromised, nor that every package version was affected. [4] [5]
Why checking imports is insufficient
Python can load startup customization through mechanisms such as .pth files and sitecustomize modules. Those mechanisms can run when an interpreter starts, before application code chooses which libraries to import. That means an inventory question such as “Does this service import LiteLLM?” is narrower than the right question: “Did this interpreter environment install or execute the compromised distribution?” Microsoft’s technical analysis documents the startup behavior and affected execution paths. [3]
This also changes where defenders should look. Include developer laptops, notebooks, CI workers, test environments, containers and deployment images—not only the production model gateway. Search lockfiles, package caches, build logs, SBOMs, container manifests and artifact registries for the version and the affected images identified by the maintainers. Use exact package and image references from current advisories rather than relying on a broad text search alone.
A response sequence for teams
First, establish exposure. Determine whether 1.107.0 or an affected image was resolved, installed, cached or executed during the incident window. Preserve relevant logs and host evidence before replacing environments. If you cannot establish that a host is clean, isolate it from sensitive systems while investigating.
Second, rebuild from a known-good base. Removing a package or deleting a mutable tag does not demonstrate that startup files, running processes or secondary payloads are gone. Prefer fresh environments created from reviewed artifacts. Validate the package source, lock dependency versions and pin container images by digest so a repository or tag change cannot silently alter the artifact under review.
Third, rotate credentials that were accessible to the affected host or identity. Prioritize high-privilege developer and release credentials, cloud tokens, model-provider keys, database credentials and signing material. Revoke old credentials before issuing replacements, and review authentication and CI logs for unexpected use. Microsoft’s guidance stresses that cleanup is broader than package removal because credentials may have been collected and processes may survive. [3]
Finally, inspect the release path that made the package trusted. Review the source repository identity, build workflow, approvals, artifact provenance and signing. A passing build can still produce a malicious artifact when the workflow fetches from an unintended repository. Require independent approval for workflow changes, restrict tokens to the smallest scope, and verify that published artifacts correspond to a reviewed commit.
Verify what the environment could reach
The response scope depends on the credentials and privileges present at execution time. A developer laptop may carry source-control tokens and cloud CLI sessions; a CI runner may hold release credentials; a production container may reach model-provider keys or a database. Build an exposure map for each affected environment instead of applying one generic “rotate everything” instruction. Use the incident window, package-resolution records and process logs to identify which secrets were accessible, then revoke and replace them through the normal owner-controlled rotation process. Review the audit trail after rotation for use of the old credentials.
For Python environments, inspect startup configuration as well as dependency manifests. A lockfile proves what the build intended to resolve; it does not prove what a running interpreter loaded or whether an image was built from the expected source. Keep the original evidence, rebuild cleanly and validate the result against a trusted artifact digest before returning the host to service. These are incident-response steps derived from the published behavior, not a claim that every system holding version 1.107.0 was exploited.
What this incident teaches beyond one package
A dependency name is not a provenance check. Teams often focus on vulnerability advisories that affect known code paths, but a build artifact can run outside the expected import path or introduce behavior in developer tooling. Strong dependency hygiene therefore combines version inventory with artifact identity, environment isolation, short-lived scoped credentials and recoverable build evidence.
The shortest practical question is not “Do we use LiteLLM?” It is “Could this version have run in any environment holding credentials we care about?” Answer it across the whole build and development fleet, then close the loop by proving fresh artifacts and rotated credentials are in use. The maintainers’ and researchers’ investigations continue to evolve; recheck the incident pages before acting on a stale copy of the timeline.
Read next
Frequently asked questions
Which LiteLLM version was compromised?
LiteLLM and independent security researchers report that version 1.107.0 released on October 21, 2026 was compromised. Follow the project advisory for the exact affected distributions and remediation details.
Is uninstalling the package enough?
No. Microsoft’s analysis says the payload could run during Python startup and recommends addressing the environment, surviving processes and credentials available to compromised identities. Rebuild from a known-good environment and rotate potentially exposed credentials.
Sources & further reading
Keep reading
Apple Opens App Subscriptions to Teams. Developers Should Model Seats Before Enabling Them
Apple adds multiseat app purchases for organizations and plans group buying. App makers need clear seat, billing and entitlement rules.
GitHub’s Xcode 27 Actions Runner Is GA and Apple-Silicon Only
The new xcode-27 labels bring macOS 27 and Xcode 27 to GitHub Actions, but only on arm64. Audit native dependencies before moving an iOS build.
GitHub Can Now Import All Branch Rules at Once. Review Before You Activate Them
GitHub’s bulk importer turns repository branch protection into rulesets. Use its preview and Evaluate mode to catch changes before enforcement.
/* Comments */
Comments are offline right now — we reconnect automatically, nothing is lost.