
GitHub Can Now Import All Branch Rules at Once. Review Before You Activate Them
GitHub’s bulk importer turns repository branch protection into rulesets. Use its preview and Evaluate mode to catch changes before enforcement.
On this page
Branch protection often grows one exception at a time: a stricter rule for the default branch, a separate pattern for release branches, then a special bypass for a service account. GitHub’s new bulk importer can turn those repository rules into rulesets in one action. The important part is the review step: automation can draft the new policy, but the team still has to confirm that it protects the same branches and preserves the intended exceptions.
What the importer does
On October 20, GitHub added an “Import branch protection rules” action under repository Settings → Rulesets. The review dialog previews the rulesets to be created, identifies rules already covered by an existing ruleset, and highlights cases where one branch protection rule becomes multiple rulesets to preserve its original behavior. Administrators can choose which rulesets to create and select Active, Evaluate or Disabled enforcement. After creation, GitHub asks whether to keep or delete the source branch protection rules. [1]
This is an expansion of GitHub’s earlier one-at-a-time conversion path. It is available for repositories where rulesets themselves are available. The source branch rules are not automatically deleted; that choice is made after the new rulesets are created. [1]
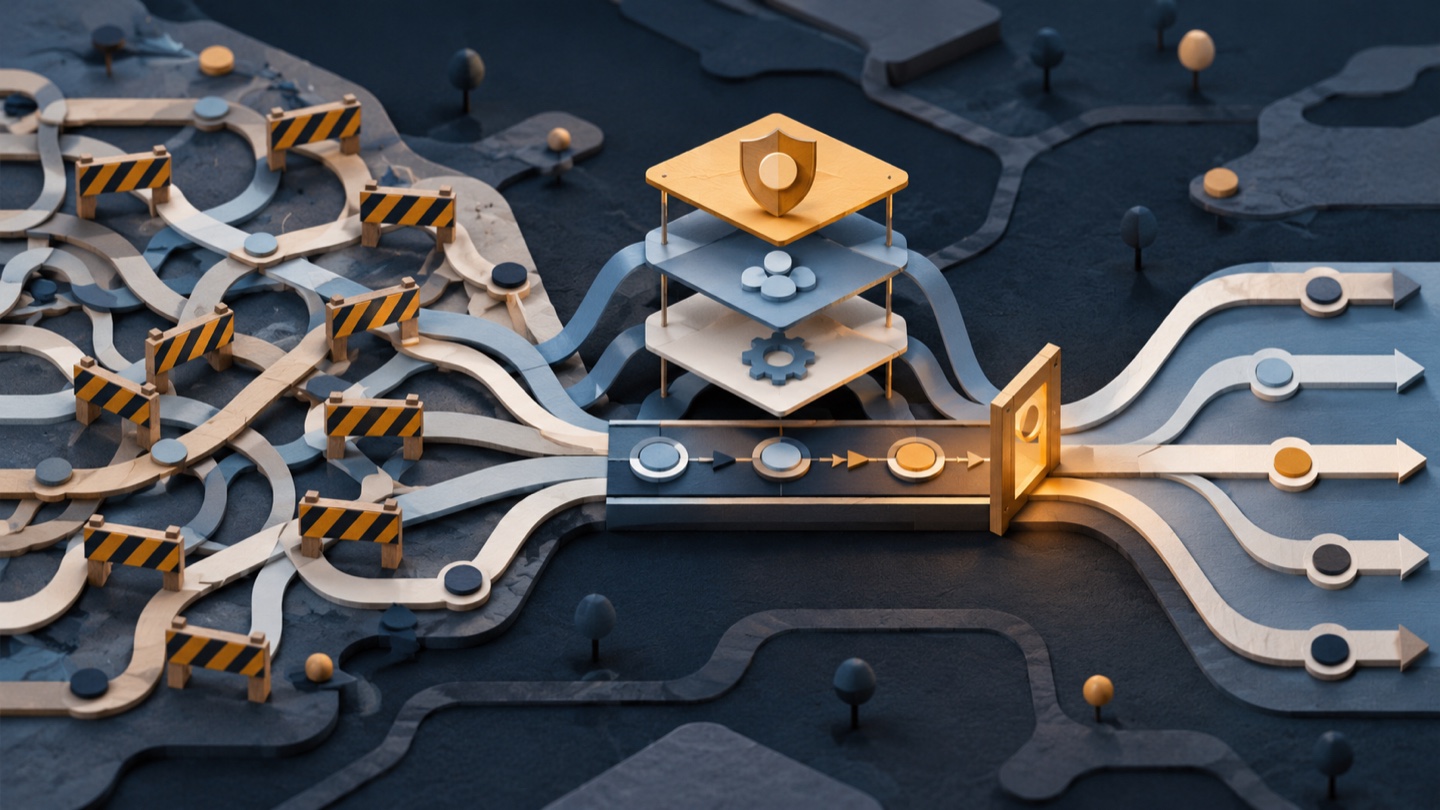
Why teams move to rulesets
Rulesets let administrators apply conditions across several branch or tag patterns, combine multiple policy layers, manage rules at repository, organization or enterprise scope, and configure more specific bypass permissions for users, teams and apps. That makes them useful when the same protection needs to apply consistently across many repositories or changing branch names. [1] [3]
The trade-off is that a policy with broader reach is easier to mis-scope. A wildcard may capture maintenance branches a team did not intend to govern. A bypass role may affect more contributors than a repository’s old exception list. A required status check may have a different effect if the check is missing, renamed or only reported on some branches. GitHub’s documentation explains the rule types and targeting model, but only your repository configuration tells you which branches and workflows are actually affected. [3] [4]
A safe conversion sequence
1. Capture the current behavior. Record every branch protection rule, target pattern, required review count, status check, signed-commit or linear-history requirement, and exception. Identify service accounts and teams with bypass access. This becomes the comparison set for the importer’s output.
2. Read the preview as a proposed policy. Look at each generated ruleset, not only the count. Verify which existing rules it says are already covered, and inspect every one-to-many conversion. A rule appearing in the preview does not by itself prove the resulting scope matches the team’s intent. [1]
3. Prefer Evaluate for the first pass. GitHub offers Active, Evaluate and Disabled statuses in the import flow. Evaluate lets a team observe where the rule would matter before enforcing it. Use that time to compare real pull requests and branch names, especially deployment branches, emergency fixes and long-lived maintenance branches. [1]
4. Check required checks and bypass paths. Confirm the check names correspond to current workflow status contexts and that expected teams or apps can bypass only the constraints they need. Rulesets support more granular bypass permissions, which is valuable but can change how exceptions are administered. [3]
5. Activate in a controlled order. Start with one representative repository or a narrow branch target, watch the normal merge and release path, then expand. Keep the old branch protection rules until reviewers have confirmed the new policy and recovery path. If you do remove them, preserve the reviewed configuration in your normal change record.
The migration is a governance moment
The importer lowers the cost of changing formats, but that is also why review deserves attention. Branch restrictions affect whether code can merge and who can override them. A bulk migration can expose inconsistent legacy policies; it can also propagate an incorrect assumption quickly if every generated ruleset is activated without scrutiny.
Rulesets are especially useful when an organization wants a common baseline plus carefully scoped repository rules. They are less helpful if a team imports and activates everything without understanding precedence, branch matching or bypass semantics. The objective is not simply to replace an old settings page. It is to make the repository’s real release policy visible and maintainable.
GitHub’s conversion documentation and ruleset reference are good starting points. Treat the importer as a policy draft, use its review surface, and let the repository’s own pull requests validate the result before enforcement.
Frequently asked questions
What does GitHub’s bulk branch protection importer do?
The repository Rulesets page can now convert all branch protection rules in one action. Its review screen previews the rulesets, shows rules already covered elsewhere, and may split a source rule into multiple rulesets to preserve behavior.
Should a team delete old branch protection rules immediately after importing?
No. GitHub asks the administrator whether to keep or delete the original rules after creating rulesets. Compare the effective requirements and bypass behavior first, test on representative branches, and retain the old rules until the new configuration is confirmed.
What is Evaluate mode for GitHub rulesets?
Evaluate mode lets a ruleset report where it would apply without enforcing its rules. It can help teams inspect a migration before choosing Active, but the team still needs to review applicable branches, checks and bypass permissions.
Sources & further reading
Keep reading
Apple Opens App Subscriptions to Teams. Developers Should Model Seats Before Enabling Them
Apple adds multiseat app purchases for organizations and plans group buying. App makers need clear seat, billing and entitlement rules.
The LiteLLM 1.107.0 Attack Ran at Python Startup. Check Environments, Not Just Imports
The compromised LiteLLM release used Python startup hooks, so affected environments could execute code without importing it. Here is a response sequence.
GitHub’s Xcode 27 Actions Runner Is GA and Apple-Silicon Only
The new xcode-27 labels bring macOS 27 and Xcode 27 to GitHub Actions, but only on arm64. Audit native dependencies before moving an iOS build.
/* Comments */
Comments are offline right now — we reconnect automatically, nothing is lost.