
On this page
A dependency scanner that reports a problem after installation may arrive too late if a package’s install step has already read CI credentials. GitHub’s package firewall adds a policy checkpoint to the download path itself. Its benefit depends on an equally concrete condition: every endpoint that matters must actually use that path.
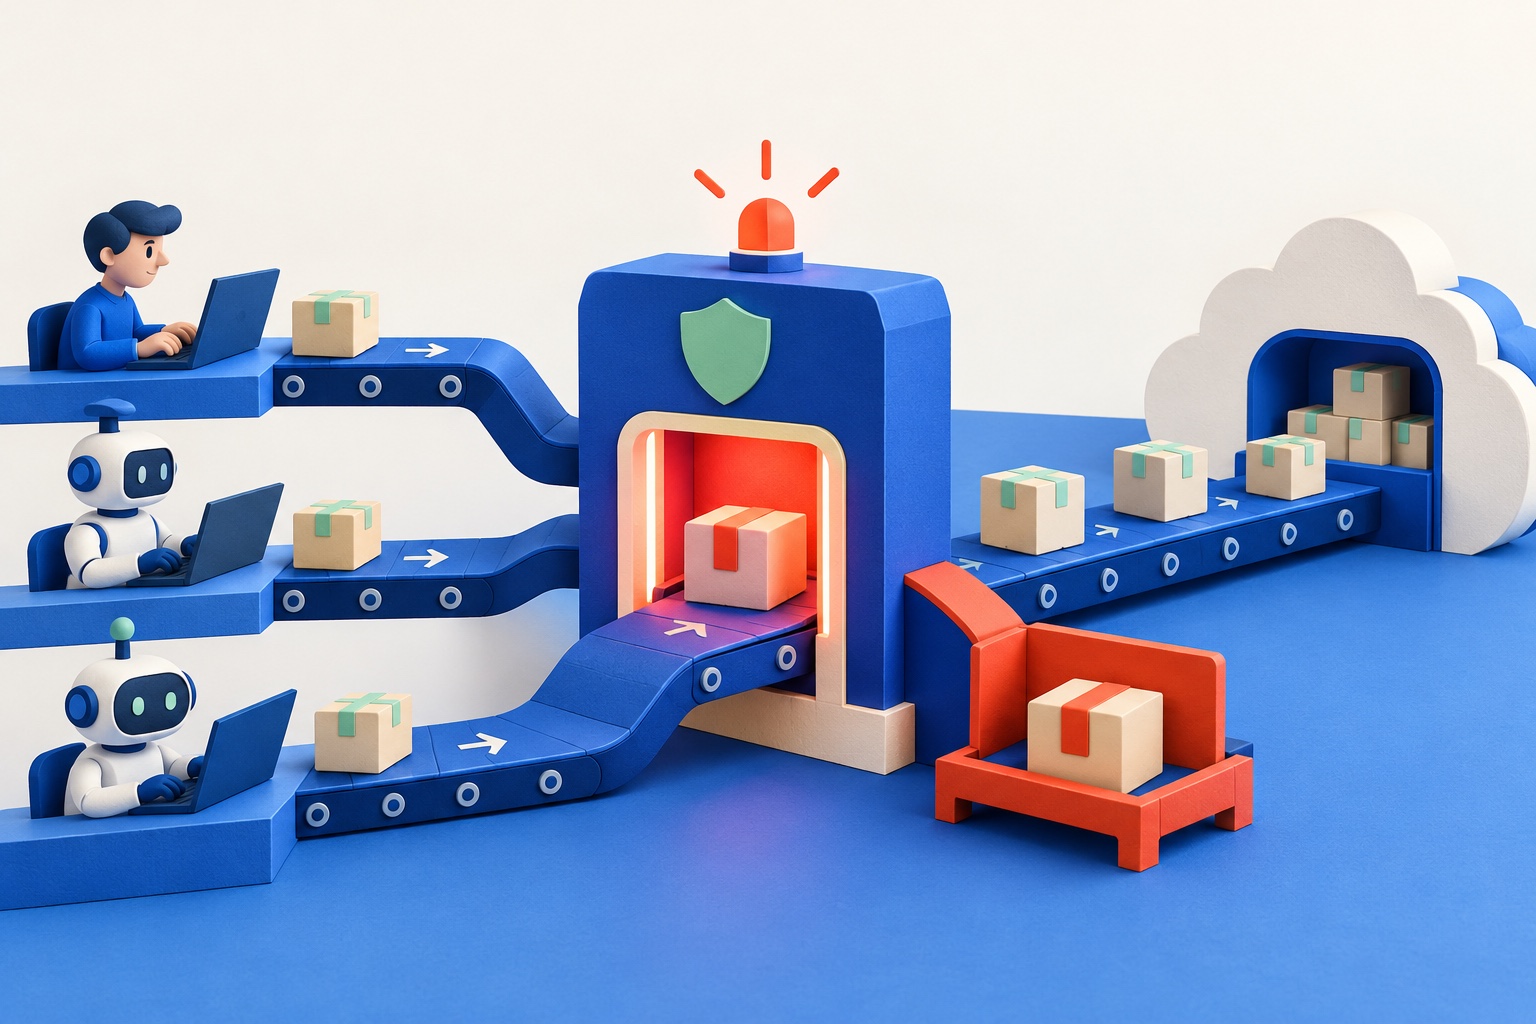
A control before package code runs
GitHub announced the public preview on October 20. The firewall sits between endpoints such as Actions runners, coding agents and developer machines and upstream package registries. It evaluates package metadata and downloads against enterprise policy before a package reaches an install process. GitHub says the available controls include a configurable cooldown, malware and vulnerability advisories, and checks for attestation downgrades. [1]
This addresses a particular risk window. Package malware can execute during installation, when developer or build credentials may be available. OpenSSF’s malicious-package repository describes these packages as intentionally harmful code delivered through ordinary open-source package repositories, distinct from vulnerable software with an accidental defect. A security gate before installation can therefore complement source scanning and vulnerability alerts that operate at other points in the lifecycle. [3]
The firewall is an enforcement path, not a scanner that sees every dependency automatically. GitHub’s setup guide says administrators first configure policy and then change endpoints to request packages through the firewall instead of the normal public registry. If a runner or workstation still reaches npm directly, that request does not pass through the enterprise rule set. [2]
Cooldown is a tradeoff, not a verdict
The minimum-age control blocks versions newer than the configured age, allowing time for problems to be discovered. GitHub’s current guide says the range is one to 365 days, with a one-day default; zero disables it. The policy can also check GitHub’s Advisory Database for malware and vulnerability alerts, with a configurable severity threshold. [2]
A cooldown reduces exposure to very recent releases but can delay a legitimate urgent fix. GitHub’s documented exception flow lets a user request an override and gives enterprise administrators a review queue. That process needs a clear owner and response target: if an emergency patch is blocked, maintainers should know how to evaluate the exception without normalizing broad allow rules. An override for one package version is narrower than allowing every version of that package. [2]
A lockfile and a firewall solve different problems. A lockfile makes dependency selection more reproducible; the firewall evaluates whether a package request should proceed under current policy. Neither proves the package is benign, and neither substitutes for reviewing changes to a dependency. Existing work on workflow lockfiles and secret detection in package ecosystems addresses adjacent controls, not this download-time checkpoint.
The operational boundary should include caches and mirrors. If an internal registry proxy serves packages without consulting the firewall, or a CI cache restores an artifact without a fresh registry request, that path may not trigger a new policy evaluation. Teams should map where package bytes originate, how cache entries are populated and who can publish to internal mirrors. The goal is to bring the first trusted download under policy, then preserve provenance through subsequent builds. Keep the npm lockfile and artifact records so incident responders can identify the exact versions already consumed.
Who can use the preview
GitHub says the preview is available to GitHub Enterprise Cloud customers, including the data-residency offering. It is free during preview; GitHub says general availability is expected to use metered charging similar to Actions billing. The changelog says the feature currently supports npm packages only. That makes it an early option for enterprise npm fleets, not a universal registry policy layer for Python, Maven, Go or every developer toolchain. [1]
GitHub’s guide shows enterprise-specific registry URLs and an authentication token associated with an enterprise member. The example token only needs read access to public repositories, and GitHub recommends keeping it in a CI secret rather than committing it. Artifactory can be configured as an intermediary, but the documentation labels that support experimental and warns that direct public-registry remotes must be excluded if they would bypass the firewall. [2]
A rollout that can prove coverage
Inventory all npm install paths before turning on enforcement: laptop configuration, CI images, self-hosted runners, container builds, automated code agents and internal proxies. Test each path and confirm the registry URL actually used. A successful policy setup in an enterprise console does not prove that every package request reaches it.
Start with a small group and a modest cooldown. Track blocked requests, exception volume, time to resolve requests and any installs that still bypass the proxy. Test a package with a known policy match and one allowed package, then verify the result in both interactive and automated environments. Keep a documented path for urgent fixes and ensure that exception review remains limited to the required package and version.
The security value is strongest when the installation path is controlled and observable. GitHub’s preview can add a useful pre-install decision point for npm, particularly for environments where code and secrets meet. But the first implementation task is endpoint routing; the second is operating the policy without blocking routine maintenance. The firewall helps enforce a rule only where traffic flows through it.
Frequently asked questions
Does GitHub package firewall protect every package manager?
No. The October 20, 2026 public-preview announcement says the service currently supports npm packages. GitHub says it is available to GitHub Enterprise Cloud customers, including data-resident Enterprise Cloud.
Will enabling GitHub package firewall automatically protect CI?
No. Administrators set enterprise policy, and each endpoint must be configured to fetch packages through the firewall rather than directly from the public registry. Any direct route can bypass those checks.
Sources & further reading
Keep reading
Amazon ECS Gateway Shares Ingress Plumbing, but Teams Still Own the Boundaries
AWS adds a shared ingress resource for ECS. See how connectors, ALB capacity, IAM and subnet compatibility shape adoption.
Synaptics’ Astra SR200 Puts a Coral NPU Beside the Sensors
The SR200 pairs multimodal edge compute with Coral NPU and an open compiler path. The published GOPS figures are vendor claims, not benchmarks.
Claude Structured Outputs on Bedrock Can Enforce Shape, Not Business Truth
Bedrock adds schema-constrained Claude output, but route and model support vary and valid JSON still needs domain validation.
/* Comments */
Comments are offline right now — we reconnect automatically, nothing is lost.