
GitHub’s Public Secret Monitoring Reaches Data-Residency Enterprises—Through Domain Matching
A new GitHub preview attributes secrets in public commits to residency-region enterprises using verified domains, not shared membership rosters.
On this page
A leaked credential in a public repository can belong to an employee even when the repository sits outside the company’s GitHub enterprise. For customers using a data-residency region, GitHub says it can now surface those public exposures without sharing the enterprise’s membership roster across the residency boundary: it uses verified domains to match commit authors and route alerts.
What the preview does
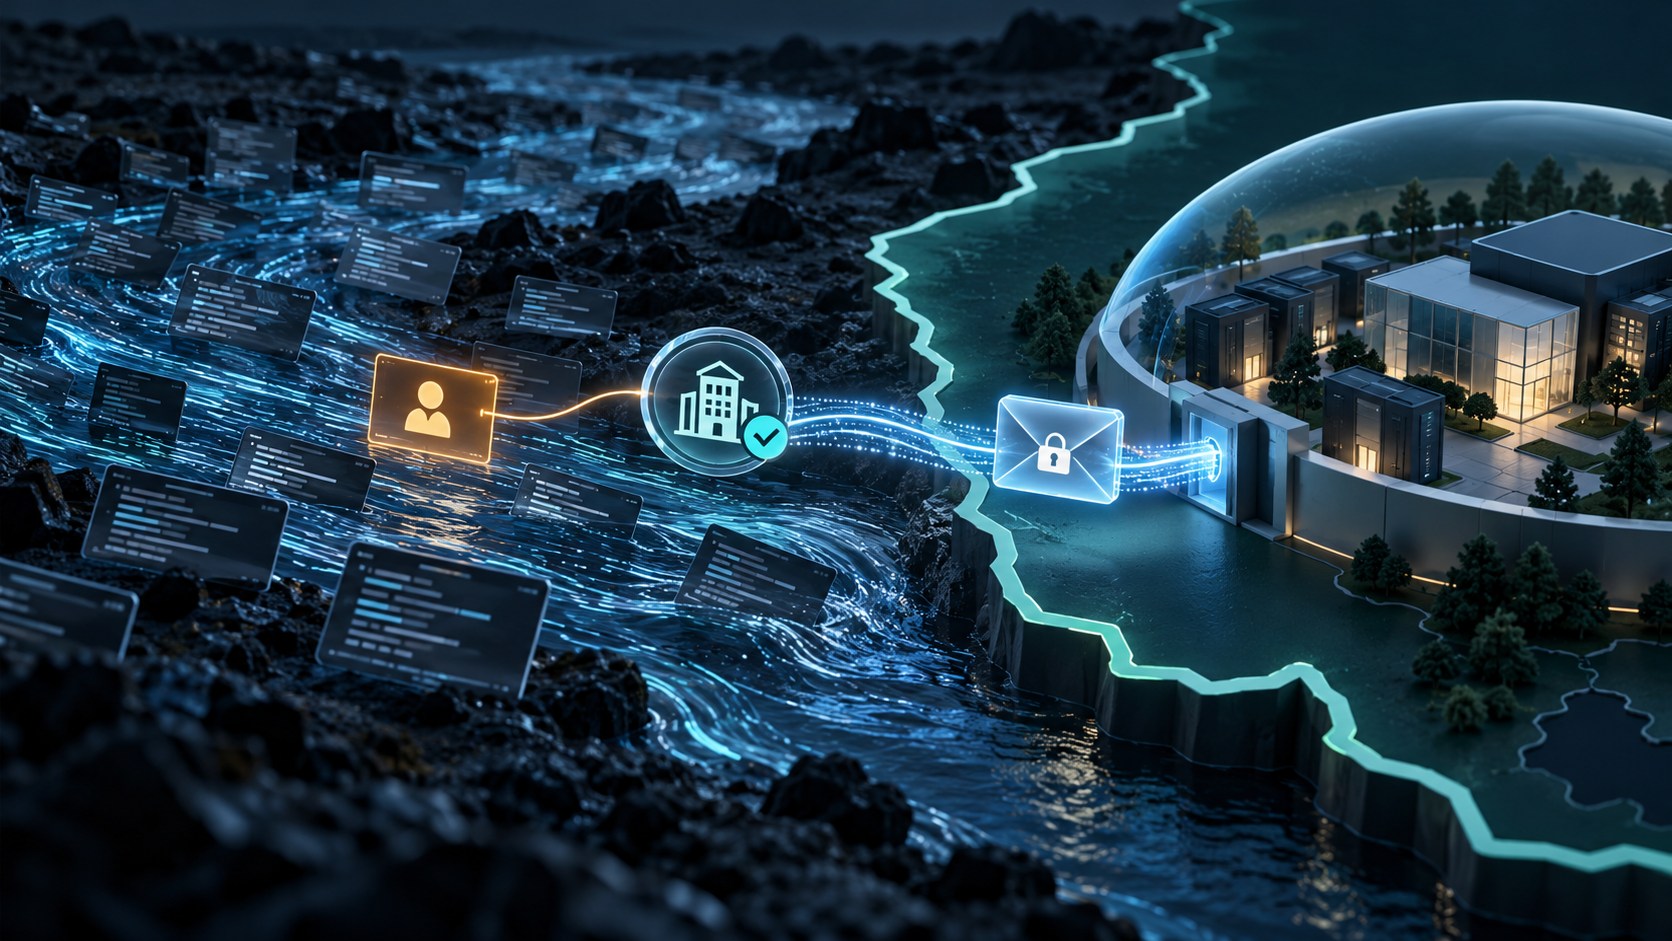
Public monitoring extends secret scanning beyond repositories an enterprise owns. GitHub says it monitors public commits across github.com for exposed credentials and attributes them to an enterprise in real time. For data-residency customers, the October 22 announcement says attribution uses verified email domains because membership rosters are not shared between the dedicated environment and GitHub.com. When a commit author’s email matches a verified domain, GitHub says the alert is encrypted and delivered to the enterprise dashboard while remaining in the designated geography. [1]
The October 22 changelog says public preview is available for GitHub Enterprise Cloud customers with data residency. However, the current feature-specific enterprise documentation still says public monitoring is unavailable to data-residency tenants. That is a material discrepancy: the announcement indicates a new eligibility path, while the operational instructions have not caught up or otherwise conflict. Do not assume access based on the changelog alone; confirm availability and terms with GitHub and the current documentation for your account before planning a rollout. The changelog says an active GitHub Advanced Security or GitHub Secret Protection license is required and that the feature is included with those licenses at no extra charge. [1] [2]
This addresses a specific visibility gap: an employee may push a credential to a personal public repository, a community project, or another location outside the company’s managed organization. Internal repository scanning cannot see those commits. An enterprise-level detection path can give security teams a signal that would otherwise depend on the employee noticing the exposure or a third party reporting it.
Domain matching is the privacy tradeoff
A residency environment cannot simply reuse an account roster that lives on a different service boundary. Domain matching gives GitHub a narrower signal: the author email in the public commit matches a domain that the enterprise has verified. That avoids sharing a broader membership list, but it also depends on the organization’s domain setup and how reliably employees use addresses associated with it. GitHub’s announcement does not describe every edge case, such as aliases, multiple email addresses, or how attribution behaves when no domain match is available. [1]
Before enabling the preview, review verified domains and ownership. Confirm that the domains still belong to the organization and that an administrator can prove control of them. Decide which security team receives alerts, how quickly it should respond, and how an exposed credential will be revoked at its source. The alert is a detection signal; it does not automatically make a cloud key, password, or token safe again.
GitHub’s data-residency documentation describes the dedicated environment and its data handling boundaries. Teams should read the current residency terms alongside the feature-specific preview documentation instead of assuming that every related data type follows the same route. The announcement’s account that alerts are encrypted and delivered to the designated geography is useful, but customers should validate the precise data flow against their own contractual and regulatory requirements. [4]
Monitoring cannot undo exposure
A secret scanner looks for recognizable credentials. It can help find a leaked key after it appears in public code, but that interval can still be enough for someone to copy and use it. GitHub’s documentation frames secret scanning as a way to detect exposed credentials; organizations still need provider-side revocation, rotation, and investigation. [3]
A useful response procedure should say who owns each credential type, how to revoke it, where to check for use, and how to restore the affected service with a replacement. A public alert should trigger containment first: invalidate or rotate the secret at the provider, then examine audit logs and potential access. Removing the commit or repository does not erase copies made by forks, caches, or other users.
The best security posture uses complementary controls. In managed repositories, enable scanning and push protection where available so a known credential can be blocked before a push. For public repositories outside the enterprise, monitoring can be a backstop. Add short-lived and narrowly scoped credentials to reduce the value of anything that escapes, and make response ownership clear before an alert arrives.
A rollout checklist for residency customers
First, verify that the enterprise uses GitHub Enterprise Cloud with data residency and has the required Secret Protection or Advanced Security license. Then resolve the conflicting eligibility guidance: the announcement says the preview is available, while the feature documentation still says it is not available for residency tenants. Ask GitHub to confirm the current account-level availability and retain that confirmation with the rollout record. Identify the enterprise owners or security managers who can enable it, and check the current docs for changes. [1] [2]
Second, review the verified-domain inventory. Include the domains employees use on public commits and confirm domain verification. Decide how the organization handles contractors, acquired domains, and employee departures. Test with a safe, non-secret test pattern if GitHub provides a supported test path; never create a real credential leak to test alerting.
Third, route alerts into an owned response process. Security teams should know how to validate the finding, revoke the credential, identify potentially affected services, and notify the employee without exposing the secret in tickets or chat. Track response time and false positives separately from the count of detected patterns.
The preview gives residency tenants a way to look beyond their controlled code boundary while retaining a narrower attribution mechanism. Its value will depend on verified domains, alert coverage, and incident response. Treat it as another sensor in a credential-protection program—not as proof that public leaks are prevented.
For a complementary credential control, see our article on expiring GitHub CLI OAuth credentials and our guide to secrets detection versus prevention.
Frequently asked questions
Does GitHub public monitoring scan an enterprise’s private repositories?
The feature described here watches public commits across GitHub.com and attributes detected credentials to a data-residency enterprise. It is distinct from scanning repositories the enterprise owns, and it does not replace secret scanning or push protection inside those repositories.
How does GitHub attribute a public secret to a data-residency enterprise?
GitHub says attribution relies on verified email domains because the residency environment does not share enterprise membership rosters with GitHub.com. Matching a commit author’s email to a verified domain triggers an encrypted alert to the enterprise dashboard.
Who can use public monitoring with data residency?
GitHub says the feature is in public preview for GitHub Enterprise Cloud customers with data residency and requires an active GitHub Advanced Security or GitHub Secret Protection license. Enterprise owners can enable it; confirm current eligibility and terms in the product documentation.
Sources & further reading
Keep reading
IBM’s Secure-Room Key Tool Targets One Piece of the Post-Quantum Transition
IBM’s key-orchestration product emphasizes dual control and physical custody; it cannot replace a cryptographic inventory or migration plan.
Why AI’s Hardest Engineering Often Starts After the Demo
OpenAI’s forward-deployed engineers describe the integration, domain learning, and evaluation work that turns AI prototypes into production workflows.
Google’s 1-Gigawatt Virtual Power Plant Is Really a Demand-Response Story
Google and Voltus plan to aggregate flexible loads across PJM, showing how virtual power plants can support grids without behaving like generators.
/* Comments */
Comments are offline right now — we reconnect automatically, nothing is lost.