
MCP’s 2026 Protocol Reset: Stateless Requests, Routing Headers, and Safer Auth
The July 2026 MCP revision removes protocol sessions, adds self-contained requests and routing headers, and changes authorization and long-running work.
On this page
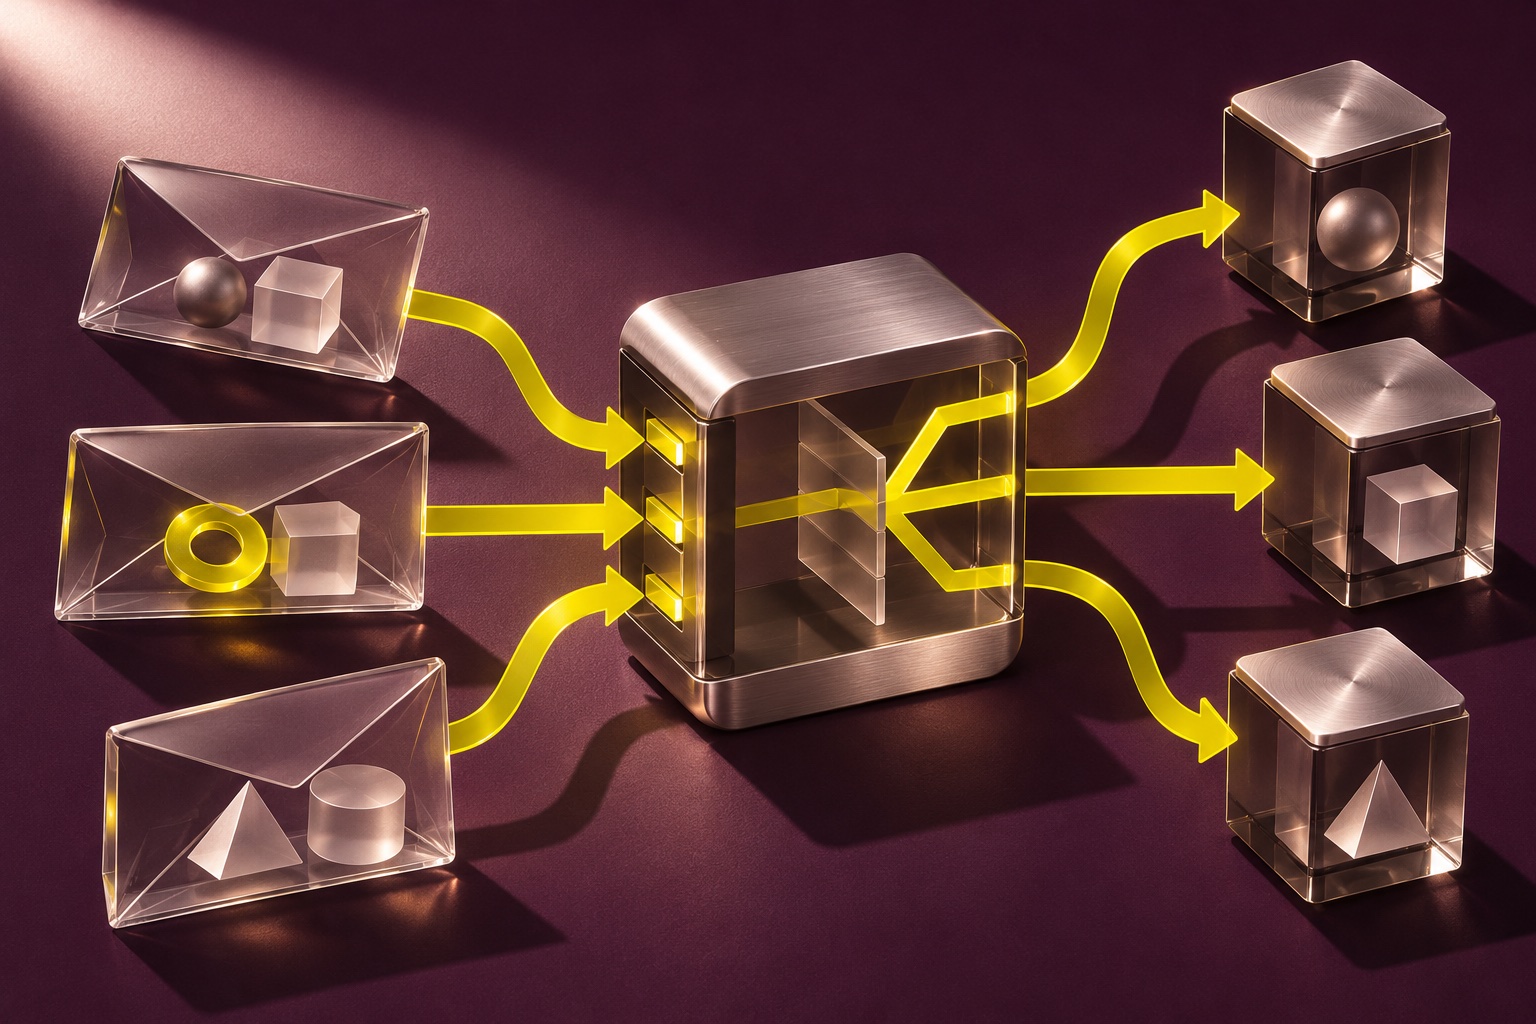
The Model Context Protocol’s first widely adopted shape assumed a client and server could establish a session, negotiate capabilities once, and keep that session alive while requests flowed. The July 28, 2026 revision removes that transport-level session model. For teams deploying MCP remotely, the change affects routing, horizontal scaling, authorization and backward compatibility—not just a version string. [1] [2]
Make each request self-contained
Under the 2026-07-28 revision, MCP retires the initialize/initialized exchange and the Mcp-Session-Id header. Requests carry protocol version, client identity and capabilities in metadata; clients can use server/discover when they want to ask a server about capabilities up front. The maintainers describe this as allowing any request to land on any server instance behind a normal load balancer without shared session storage. [2]
That changes a common deployment constraint. In the earlier session-based shape, operators often had to consider sticky routing or shared state to keep a request attached to the server that had initialized the connection. Stateless protocol requests let infrastructure distribute calls more freely. The application can still be stateful: the maintainers recommend returning an explicit handle from a tool and asking the model to pass it back on a later call. State becomes visible in the application contract rather than being hidden in a transport session. [2]
Put routing information where gateways can use it
The revision adds Mcp-Method and Mcp-Name HTTP headers for Streamable HTTP. A gateway, rate limiter or web application firewall can route or meter a request using those headers instead of parsing the JSON-RPC body. The maintainers also describe cache hints and deterministic ordering for tool, prompt and resource lists, so clients can make informed caching decisions. [2]
This can simplify gateway logic, but it creates a consistency requirement: the routing headers and request body must describe the same operation. Gateways should validate that relationship rather than trusting a header supplied by an arbitrary caller. MCP’s spec describes protocol behavior; it does not eliminate the need for authentication, authorization and input validation in each deployment.
Replace server-initiated interaction with a round trip
Earlier interactions such as elicitation and sampling relied on the server initiating a request back to a client over an open connection. The new Multi Round-Trip Request pattern lets the server respond that input is required; the client can then collect the answer and retry the operation with the response attached. This avoids requiring a permanently open bidirectional stream for those interactions. [2]
Long-running Tasks also move out of the experimental protocol core into an extension. The revision’s maintainers state that this makes the feature’s lifecycle and polling behavior explicit and opt-in. Implementations that used the older experimental task API need to check the new extension contract rather than assuming a drop-in upgrade. [2]
Authorization changes deserve a separate migration review
The release includes authorization hardening: issuer validation following RFC 9207, issuer-bound client credentials, and a formal move away from Dynamic Client Registration toward Client ID Metadata Documents. The maintainers say Dynamic Client Registration remains for backward compatibility but is deprecated. These changes affect OAuth flows and client registration, so a protocol upgrade should include a threat-model and compatibility review, not only transport tests. [2]
The specification itself emphasizes user consent and control, data privacy, and caution around tools that can execute arbitrary code. It also says that the protocol cannot enforce these principles on its own; implementers must build authorization and data protections into the host and server applications. [1]
Plan for mixed-version systems
MCP 2026-07-28 is a breaking revision. The right migration strategy depends on the client/server fleet: inventory deployed SDK versions, identify code that depends on initialization or Mcp-Session-Id, and decide whether to upgrade both ends together or keep separate compatibility paths. Test gateway header handling, request retries, cancellation and task extensions with real clients before removing legacy support.
The larger lesson is that a protocol can evolve without making every application stateless. MCP’s new boundary makes transport requests easier to distribute, while state and user intent remain explicit in application-level handles and authorization checks. For the broader design of agent tool calls and server boundaries, see this production coding-agent architecture, which depends on reliable orchestration and inspectable tool interactions.
Stateless transport still needs an application contract
Removing Mcp-Session-Id does not remove a product’s need to remember a workflow. The maintainer guidance is to pass explicit handles—such as a task or browser identifier—through tool arguments when later calls depend on earlier work. That makes the state visible to the model and application, and it lets the protocol layer distribute requests without silently pinning them to one server process. [2]
This distinction matters for horizontal scaling. If an MCP server stores conversation state in process memory and assumes the next request lands on the same instance, the new transport behavior will expose that assumption. Teams need to move durable state to an application store or make handles explicit, then test retries and cancellation across different server instances.
Multi-round-trip requests change interaction flow
The 2026 revision’s Multi Round-Trip Request approach handles cases where a server needs user input during a tool call. Rather than initiating a callback over a held-open stream, the server responds with an input_required result and describes what it needs. The client gathers the input and retries the operation with the responses attached. [2]
This makes the interaction more compatible with ordinary request/response infrastructure, but it puts responsibility on the client to preserve the original operation and attach the right response. A migration test should cover a missing parameter, an explicit user confirmation, a timeout, a repeated request and cancellation. It should also verify that the server does not perform the side effect before the needed input has been supplied.
Gateways can route by headers, but should verify them
The spec adds Mcp-Method and Mcp-Name headers to Streamable HTTP requests so infrastructure can route or meter on operation names without parsing a JSON body. [2]
That is an operational convenience, not an authorization decision by itself. A robust gateway should validate that the header values correspond to the JSON-RPC operation, enforce authentication and rate limits, and avoid trusting a client-supplied tool name as proof of permission. The specification describes wire format; each deployment must still bind an authenticated identity to the tools and data that identity may access.
The release also makes tool and resource list responses cacheable with hints. That can reduce repeated discovery traffic and stabilize prompts, but caches need scope and expiry rules. A tool list that differs by user or workspace cannot safely be cached as if it were globally identical. [2]
Treat version compatibility as a rollout problem
The new revision removes initialization and protocol sessions and changes how input requests, Tasks and authorization work. Maintainers describe the update as breaking and provide migration notes. A production rollout should inventory deployed client and server versions, identify which side initiates a connection, test old/new pairings, and define a deprecation window rather than assuming the protocol negotiates every old behavior automatically. [2]
MCP’s architecture is still a client/server protocol for tools and context. What changed is the transport and lifecycle boundary: calls are independently routable, while applications must make durable state and permission checks explicit. That reset can make infrastructure easier to scale, but only when implementations migrate the assumptions that were previously hidden inside a session.
Frequently asked questions
What changed in MCP 2026-07-28?
The revision removes the protocol-level initialization handshake and session ID, makes requests self-contained, adds header-based routing, revises interactive multi-round-trip flows, and hardens authorization.
Does stateless MCP mean the application cannot keep state?
No. The protocol no longer requires hidden session state at the transport layer. An application can preserve state explicitly with handles such as a task or resource identifier passed between calls.
Can an MCP client using the 2025-11-25 revision connect to a 2026-07-28 server unchanged?
Not necessarily. The 2026 revision includes breaking protocol changes; clients and servers need compatible implementations or a deliberate migration/compatibility path.
Sources & further reading
Keep reading
How Deep Research Agents Work: Orchestrators, Parallel Sub-Agents, and Cited Synthesis
Inside deep research architectures across OpenAI, Gemini, and Claude: planning supervisors, parallel search sub-agents, and verifiable claim attribution.
Menu Digitization at Scale: OCR, LLMs and Guardrail Classifiers in Production
How DoorDash turns messy restaurant menu photos into structured JSON using OCR, multimodal LLMs, and a gradient-boosted LightGBM confidence guardrail.
OpenAI Prompt Objects Scheduled to Shut Down November 30: A Migration Guide
OpenAI schedules its reusable prompt-object endpoint for shutdown on November 30, 2026. Here is how teams can migrate prompts into code and evals.
/* Comments */
Comments are offline right now — we reconnect automatically, nothing is lost.