
A Vulnerability Feed Is a Starting Point, Not a Patch Plan
Cloudflare Radar’s Zero Wire summarizes critical disclosures. Security teams still need asset matching, exploit context, and a tested fix.
On this page
A critical vulnerability disclosure lands before the workday begins. The security team needs to know whether the affected software exists in its environment, whether attackers are exploiting it, what mitigation is safe, and which service owner must act. A feed can compress the first reading of the advisory. It cannot know your asset inventory or prove that a patch will not break your production system.
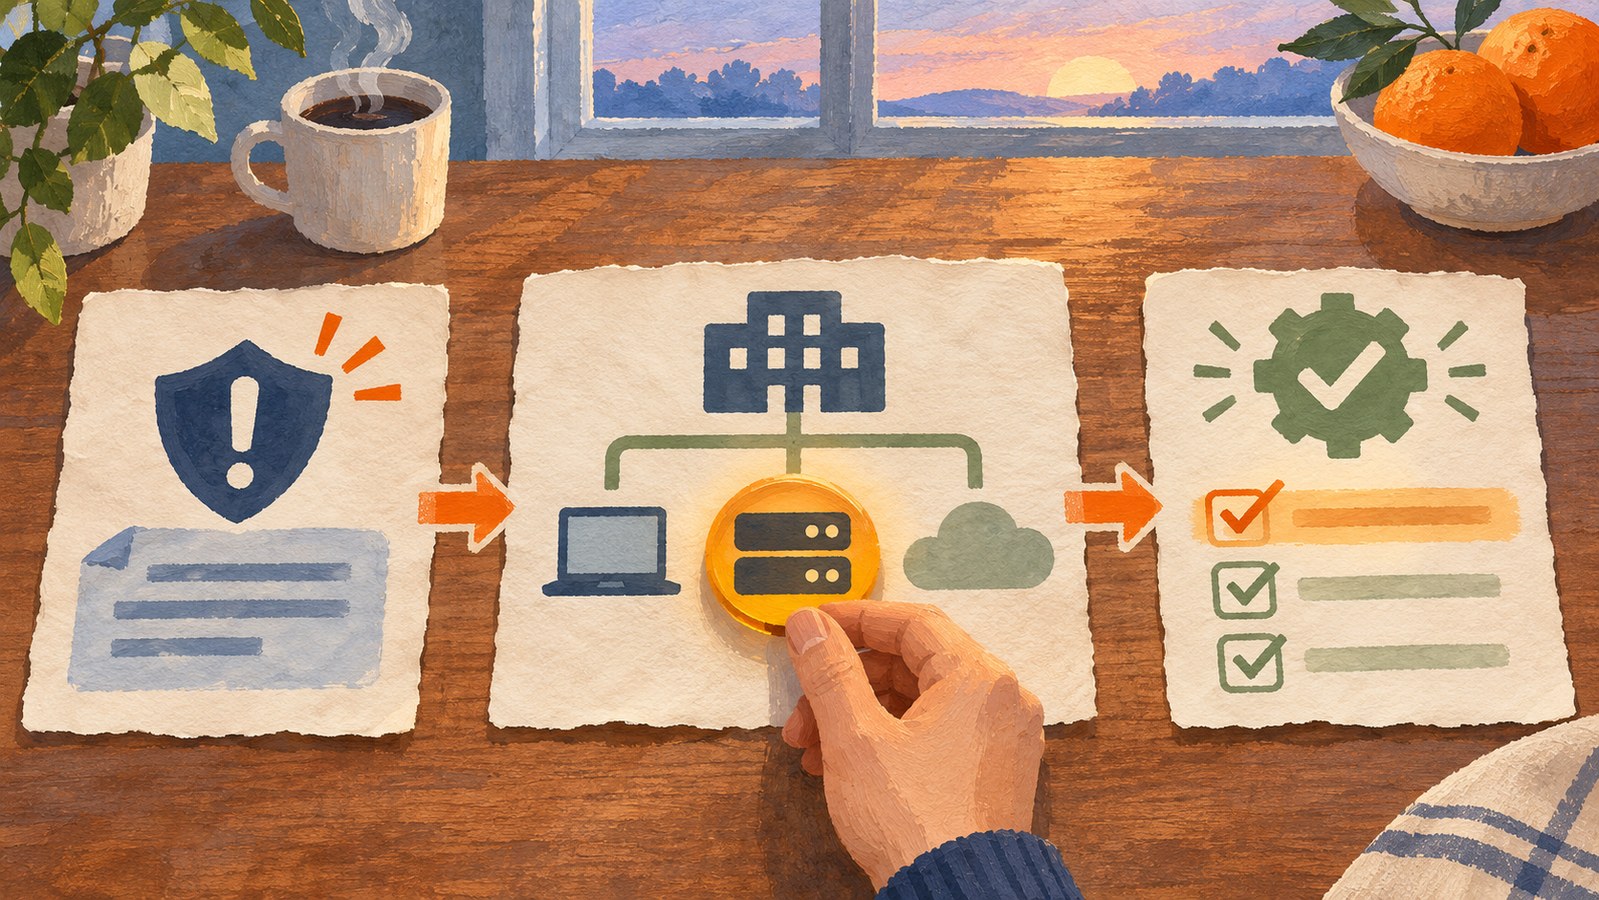
Cloudflare introduced Zero Wire on November 3 as a public vulnerability-intelligence feed inside Cloudflare Radar. Each briefing is designed to pair a plain-language explanation with who should investigate, recommended actions, evidence links, and vendor guidance. Cloudflare also describes a precompiled prompt for an agent to assess an organization’s infrastructure. The product is positioned as a starting point for understanding critical disclosures, including for people who do not use Cloudflare services. [1]
That framing solves a real operational problem: security teams repeatedly translate advisories into decisions for executives and engineers. But a clear briefing is not an environmental assessment. Your inventory, exposed services, version pinning, compensating controls, and deployment windows determine whether the issue applies and how quickly you can respond.
Separate severity, exploitation, and exposure
A CVE score describes characteristics of a vulnerability, not whether your organization runs the affected component or whether attackers are using it against you. CISA’s Known Exploited Vulnerabilities (KEV) catalog records vulnerabilities known to have been exploited in the wild and is intended to inform remediation prioritization. FIRST’s EPSS estimates the probability that a vulnerability will be exploited in the wild during the next 30 days; it is a probability signal, not a statement that exploitation has already occurred. NIST’s National Vulnerability Database provides enriched vulnerability records, but enrichment and scoring do not replace local asset matching. [2] [3] [4]
A practical triage decision combines at least four questions:
- Is the affected product and version actually present?
- Is the vulnerable code path enabled or reachable in the deployed configuration?
- Is there evidence of active exploitation or a credible near-term threat?
- What is the safest available mitigation, and how will the team verify it worked?
These signals should not be collapsed into a single “critical” label. A severe bug in an absent package may be lower priority than a moderately scored flaw on an exposed, business-critical service. A KEV listing can justify urgency, but it does not tell you which host is vulnerable. EPSS can help forecast attention, but it is not an incident report. A vendor advisory may explain a workaround, but your maintainers must validate its fit.
Turn the briefing into an auditable workflow
Use an intelligence feed to open a record, not to close one. Capture the source advisory, affected versions, exploit conditions, mitigations, and date of last verification. Match those details against software bills of materials, package inventories, cloud workloads, appliance fleets, and owners. If an automated assistant helps search the inventory, provide it with a bounded read-only view and require it to return the asset evidence and query method, not just a yes/no answer.
When exposure is confirmed, assign an owner and a deadline based on impact. Test a patch or mitigation in a representative environment, then verify the deployed version and relevant logs. If the vulnerability is not applicable, record why: product absent, affected version absent, feature disabled, or network path unreachable. “We found no match” is weaker evidence than a repeatable inventory query that another responder can run.
Cloudflare says Zero Wire combines external authoritative sources with its own security research and network observations. That can add useful context, but readers should still follow the linked vendor advisory and official catalog entries for operational decisions. Cloudflare’s view of internet traffic is one source of evidence; it cannot reveal every attacker or every privately deployed system. [1]
Use an agent carefully when the inventory is large
A prompt that asks an agent to “check whether we are affected” is underspecified. It can miss aliases, container layers, statically linked libraries, managed services, or systems the search tool cannot access. A better task names the CVE, product identifiers and versions, approved data sources, and output format. Ask for matched assets, query timestamps, uncertainty, and missing coverage. Keep the agent from changing systems while it is still building the picture.
Human review remains necessary before disruptive action. Restarting a service, disabling a feature, or applying an emergency patch can create its own outage. The response should balance exploit risk against change risk, document the decision, and use the fastest reversible mitigation that actually reduces exposure.
What to evaluate in any vulnerability feed
Ask whether a briefing links directly to primary advisories, distinguishes confirmed exploitation from prediction, shows when the information changed, and explains the evidence behind its recommendations. Check whether it tells you what it does not know. Then test whether the feed reduces time from disclosure to verified disposition—not just time to read a summary.
Zero Wire may make the first pass easier. The durable security work still happens inside your organization: inventory the software, establish exposure, decide urgency, apply a tested fix, and confirm the result. A useful feed speeds that chain; it cannot substitute for it.
Sources & further reading
Keep reading
Encrypted Robot Commands Can Still Leave a Readable Rhythm on the Network
A 2026 study found robot actions could be inferred from encrypted traffic metadata, exposing a privacy gap between payload secrecy and behavioral privacy.
Microsoft's Q3 Phishing Report Has a Quiet Warning About Security Exceptions
Microsoft counted 7.3 billion email threats in Q3, but its 129 million spoofed-service messages show how broad allow rules can undo detection.
A Cold-Chain Cyberattack Can Become a Temperature Problem Before It Becomes an IT One
CISA's cold-chain warning shows why exposed refrigeration controls need asset inventories, isolation, supported patches and tested recovery.
/* Comments */
Comments are offline right now — we reconnect automatically, nothing is lost.