
Encrypted Robot Commands Can Still Leave a Readable Rhythm on the Network
A 2026 study found robot actions could be inferred from encrypted traffic metadata, exposing a privacy gap between payload secrecy and behavioral privacy.
On this page
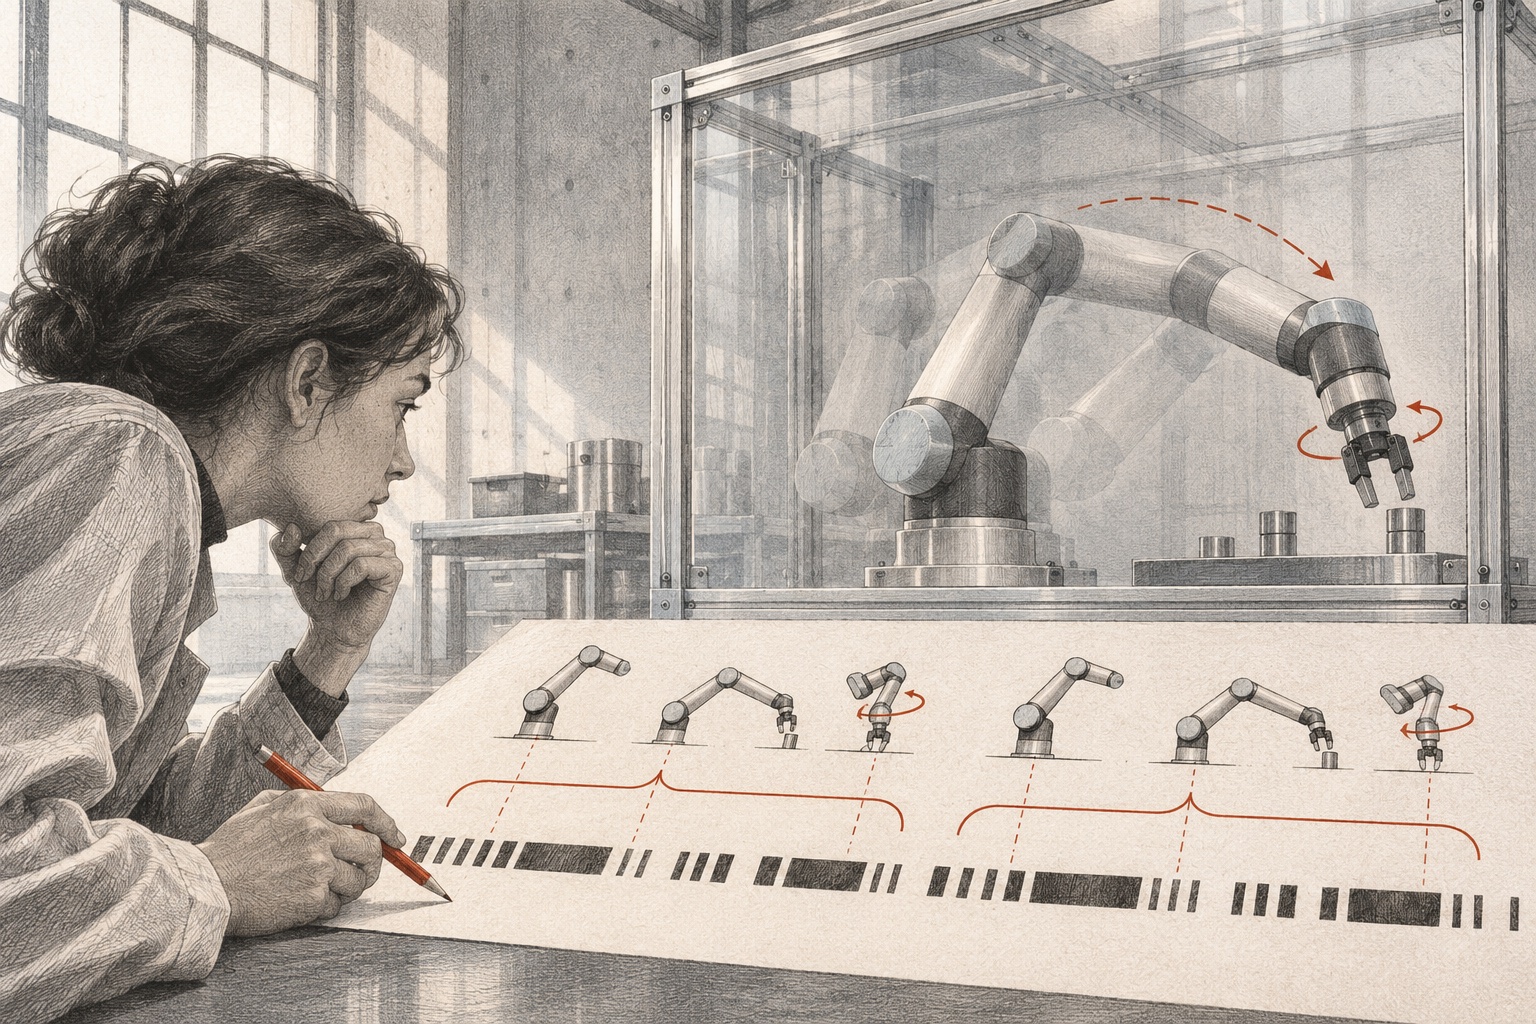
Encryption can keep the contents of a robot command private and still leave clues about what the robot is doing. Packets have timing, size and direction. A system that sends a distinct burst while an arm reaches, turns or grips can produce a pattern an observer may classify without ever seeing the command itself.
A new study in Computers & Security examines that gap using a smartphone motion sensor to control a collaborative robotic arm through three control modes: position, velocity and torque. The researchers studied four actions and analyzed the network traffic exchanged between the phone and robot. They report that machine-learning classifiers could identify actions from traffic metadata, then used information-theoretic bounds to ask how much information the control protocol exposed in principle—not just what a particular classifier happened to learn.
The finding is about privacy leakage in a controlled setup. It is not evidence that an observer can decrypt the robot’s commands, take over the arm or identify every task in a factory. It is a reminder that payload encryption and behavioral privacy are different security goals.
The visible rhythm around a hidden message
Transport encryption protects data payloads as they cross a network. It does not make the network itself disappear. A router or other observer may still see when packets are sent, their approximate sizes and direction, and how traffic volume changes over time. Those properties can correlate with application actions.
For a robot, a control mode affects that rhythm. A controller that continually sends small updates while tracking a target may look different from one sending a short command that begins a predefined movement. The study compares position-, velocity- and torque-based control and reports that torque control carried more deterministic information about the action than its empirical model suggested, while velocity control inherently exposed less. That is a result for the tested setup, not a ranking that automatically applies to every robot protocol.
The authors also evaluated traffic padding, a defense that adds or adjusts traffic to make communication patterns less distinctive. Their analysis warns against assuming that adding bytes alone removes the leak: timing and interaction structure can remain, and padding has costs in bandwidth and latency. In a real-time control loop, those costs matter because delay can affect responsiveness and safety.
Privacy leakage is different from remote control
The word “attack” can make a paper sound like a robot takeover. This work is narrower. The observer is trying to infer the action class from traffic patterns; the payload remains encrypted. That could matter in settings where the action itself is sensitive: a robot assisting a patient, a worker handling a particular material, or a machine running a proprietary process.
Inference can still be uncertain. The study uses a limited set of actions, a specific arm and phone-based controller, and experimentally collected traffic. Real facilities add network noise, different control stacks, changing tasks and background traffic. The paper’s abstract does not support a claim that all deployments leak equally or that its classifier will generalize to an unseen environment.
Earlier University of Waterloo research also studied action fingerprinting in encrypted robot traffic and described how packet patterns could reveal behavior. The new paper extends the question with joint-level control modes and information-theoretic bounds. Together, this line of work makes the issue easier for robotics engineers to treat as a system property rather than a cryptography bug.
Test the whole control loop
Robot builders and operators can start with a threat-model question: who can observe the network path between the controller and the machine? Then assess what a passive observer could learn from traffic timing and volume. Capture traces in a controlled test environment for representative tasks, compare patterns across repeated runs and measure how much background traffic or added shaping changes the result.
Possible mitigations include shaping traffic to make actions less distinguishable, reducing unnecessary exposure of the control network, and limiting access to network telemetry. Each needs testing against control latency, reliability and fail-safe behavior. A defense that makes a sequence harder to classify but causes control delay may create a different operational risk.
This is also why “TLS enabled” is an incomplete privacy statement. It tells readers that message contents are protected in transit under specified conditions. It does not say whether observers can infer activity from metadata, whether endpoints retain sensitive logs, or whether a remote access path is appropriately restricted.
The engineering lesson is clear: evaluate what the motion looks like from outside the encrypted channel. For connected robots, protecting command content is essential, but it may not hide the behavior those commands create. Our cold-chain security guide explores a related operational-technology lesson: network controls must account for the physical system that depends on them.
Frequently asked questions
Can encrypted network traffic reveal what a robot is doing?
Sometimes. A recent study found that packet timing, size and direction in a controlled robot-arm setup could help classifiers infer which of four actions was being performed, without reading the encrypted command contents.
Does this mean an attacker can take control of a robot?
No. The study is about inferring actions from traffic patterns, not decrypting commands or controlling the robot. It describes a privacy side channel that may expose task or behavior information to an observer of the network path.
Would padding all network packets solve the problem?
Not necessarily. The researchers prototyped traffic padding and found limits because protocol behavior can preserve structure even when some packet sizes are obscured. Defenses need to be tested against timing, direction, rate and control-mode leakage while respecting latency and safety requirements.
Sources & further reading
- Tang et al., Computer & Security 170 (2026), article 105018
- Publisher abstract and article record
- University of Waterloo: earlier research on privacy leaks in encrypted robot traffic
- RFC 8446: The Transport Layer Security (TLS) Protocol Version 1.3
- University of Waterloo Active and Interactive Robotics Lab publications
Keep reading
Microsoft's Q3 Phishing Report Has a Quiet Warning About Security Exceptions
Microsoft counted 7.3 billion email threats in Q3, but its 129 million spoofed-service messages show how broad allow rules can undo detection.
A Cold-Chain Cyberattack Can Become a Temperature Problem Before It Becomes an IT One
CISA's cold-chain warning shows why exposed refrigeration controls need asset inventories, isolation, supported patches and tested recovery.
OpenSSH 10.6p2 Fixes a Rare Authentication Path; Check the Build, Not Just the Version
OpenSSH 10.6p2 carries a critical workaround for some Linux builds using musl without PAM. Here is how operators should scope and verify exposure.
/* Comments */
Comments are offline right now — we reconnect automatically, nothing is lost.