
Microsoft's Q3 Phishing Report Has a Quiet Warning About Security Exceptions
Microsoft counted 7.3 billion email threats in Q3, but its 129 million spoofed-service messages show how broad allow rules can undo detection.
On this page
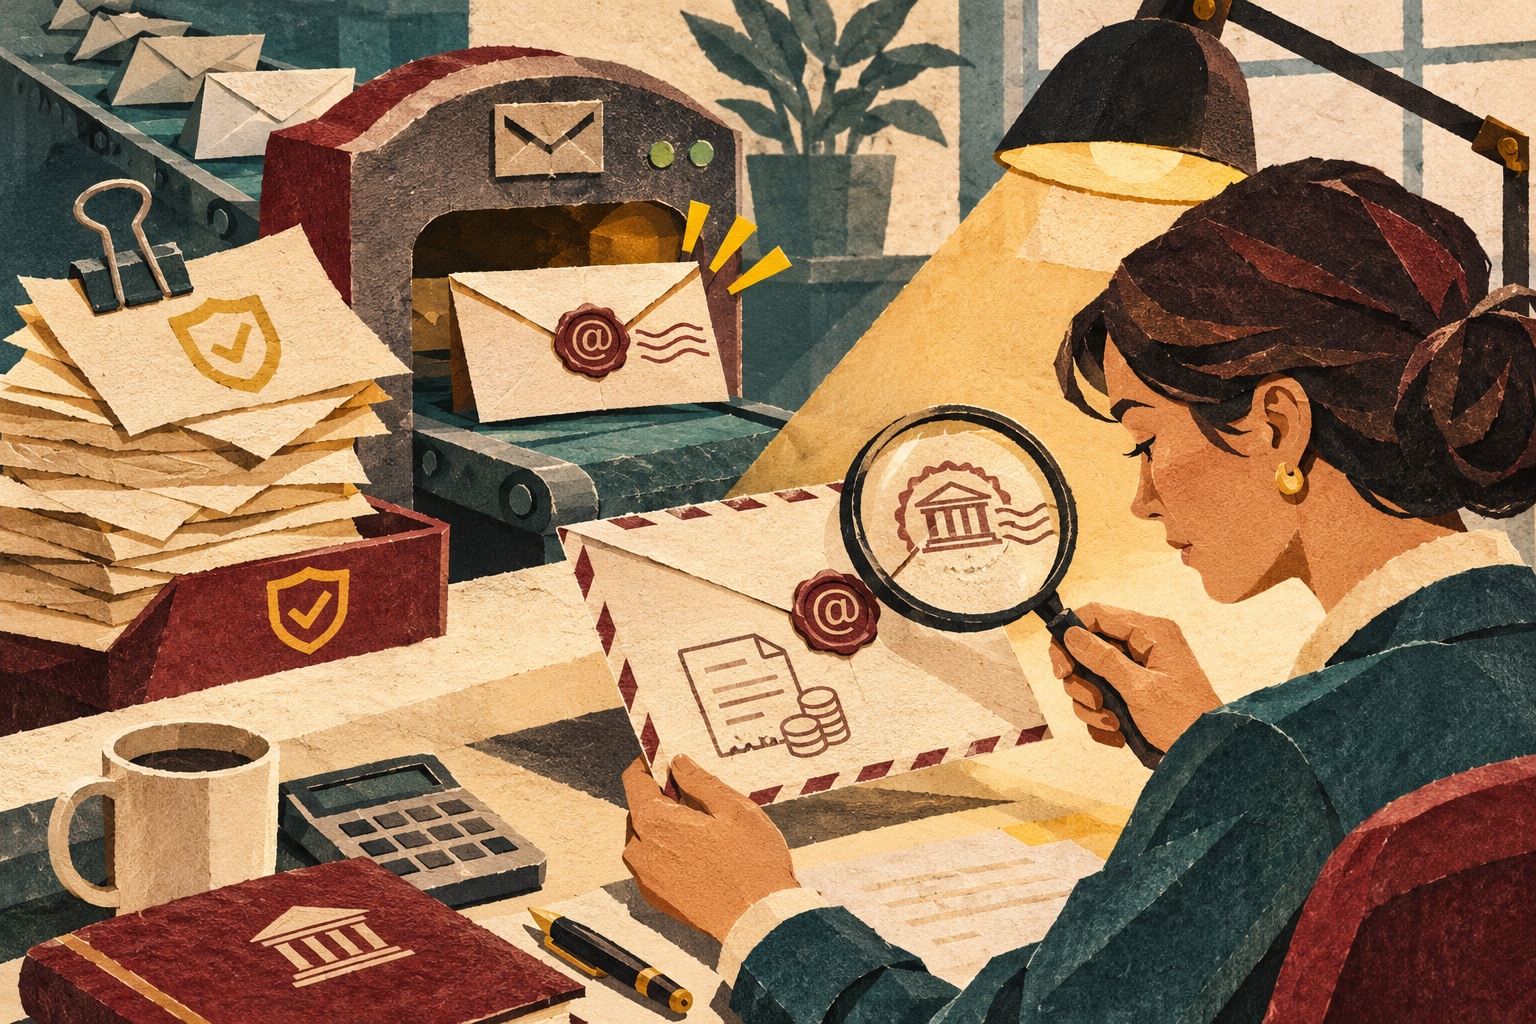
An email security system can recognize a message as dangerous and still let it through. That is the uncomfortable lesson in Microsoft Threat Intelligence’s third-quarter 2026 email report: the barrier can fail in policy after it succeeds at detection.
Microsoft says it detected about 7.3 billion email phishing threats from July through September, with nearly 3 billion in September, 41 percent more than August. Inside that large total, it counted about 129 million malicious messages spoofing tracked business-service sender domains. In September, 63 percent of those spoofed messages with a recorded security outcome had a tenant- or user-level override applied. The report says most of those overrides were tenant-level.
That figure is not a breach count. It does not establish that recipients opened the messages or that accounts were compromised. It does point to a security control worth inspecting: exceptions intended to keep invoices, signing requests or surveys flowing can weaken protections against messages that impersonate those same services.
The failure can happen after authentication
A display name is easy to fake. So is a lookalike domain that swaps one character. A more subtle tactic is to make a message appear to come from the real service a company uses. Microsoft describes these as spoofed sender-domain messages: the attacker borrows the domain identity associated with a familiar business workflow, such as document signing or a survey.
Email authentication helps receiving systems assess whether a sending service is authorized for a domain. SPF checks sending infrastructure, DKIM verifies a cryptographic signature, and DMARC lets a domain owner publish how receivers should handle messages that do not align with those signals. These checks are not a complete trust system: a legitimate service can be abused, account compromise can produce authenticated mail, and policy configuration still affects delivery. But an authentication failure combined with a malicious verdict should be a strong reason to block or quarantine a message.
The risk Microsoft highlights arises when a bypass rule changes that outcome. A broad allow rule can be created to solve a real operational problem—perhaps a partner’s messages are being quarantined. But if it trusts a whole sender domain or ignores other verdicts, attackers may be able to exploit the same carve-out. The organization can end up treating a recognizable brand as proof of sender identity.
Audit the exceptions, not just the detections
Security teams often review detection dashboards, blocked-message totals and user reports. Microsoft’s numbers suggest adding an exception review to that routine. Export allow lists, transport rules, tenant overrides and user-level safe-sender settings. For each one, record who requested it, which exact sender or message type it covers, what control it bypasses, when it was last reviewed and how it will be tested.
Narrow the rule to the smallest workable scope. Prefer a verified sending service or a specific authenticated configuration over a broad domain trust. Keep the rule from overriding malware or high-confidence phishing verdicts where the platform allows that distinction. Assign an expiration or review date to temporary exceptions. If a supplier needs a legitimate workflow, test the narrow fix with that supplier rather than accepting a permanent blanket bypass.
DMARC can reduce direct domain spoofing when configured to enforce a policy, but it does not replace inbound controls. Administrators need to understand both the sender’s published policy and the receiver’s own exception behavior. The right question is not simply “Did authentication pass?” It is “What happens when authentication fails, other signals disagree, or a bypass rule matches?”
The attack mix changed within the quarter
Microsoft’s report also cautions against treating phishing as a single rising or falling number. QR-code attacks declined by 67 percent in Q3, to about 12.1 million, but CAPTCHA-gated phishing recovered from its July low. In September, Microsoft counted 3.1 million CAPTCHA-gated attacks, almost twice July’s volume. SVG attachments accounted for a large share of that technique in August and September.
The purpose is not to chase every file format. An attacker can place a credential-harvesting path in a PDF, an SVG, a QR code or an ordinary URL. The constant is that the message tries to move a person into a second context—often a browser or a phone—where the organization’s email controls have less visibility. Security training should teach people to verify the request through a known channel, especially when it involves payroll, document access or payment.
Microsoft also recorded 141,000 malicious Teams call attempts in the quarter, while reporting a shift toward ordinary personal-name display names instead of explicit help-desk identities. That is a reminder that collaboration tools are part of the same identity problem: an apparent coworker or service contact is a claim to verify, not proof.
A practical review for this week
Choose the ten broadest or oldest email exceptions and review them with the business owners who requested them. Remove stale entries, narrow the ones that remain and test a known legitimate sender before and after the change. Then sample messages blocked for authentication failure and messages delivered under an exception. Check that the outcome follows policy, and make sure an administrator can explain why.
The larger report is based on Microsoft’s own detection systems and definitions; its totals are not a universal census of every provider’s email traffic. Its strongest operational lesson is more specific: protections have to be evaluated end to end. A detector that recognizes a threat cannot protect a recipient when a permissive rule silently reverses the decision.
Our cold-chain security guide examines the same configuration question in operational technology: whether a control is actually enforced when production depends on it.
Frequently asked questions
What was Microsoft’s main Q3 email-security finding?
Microsoft reported 7.3 billion detected email phishing threats in Q3 2026 and 129 million malicious messages spoofing tracked business-service sender domains. Its analysis also found that tenant or user exceptions affected many messages that failed authentication and were identified as malicious.
Does the report show that 63 percent of recipients were compromised?
No. The 63 percent figure refers to September messages with a recorded security outcome where tenant- or user-level overrides applied. It does not show that recipients opened those messages or that accounts were compromised.
What should an email administrator review first?
Review allow lists and other bypass policies for broad sender or domain patterns, remove exceptions that no longer have an owner or business need, and test authentication and delivery controls against legitimate workflows before tightening policy.
Sources & further reading
Keep reading
Encrypted Robot Commands Can Still Leave a Readable Rhythm on the Network
A 2026 study found robot actions could be inferred from encrypted traffic metadata, exposing a privacy gap between payload secrecy and behavioral privacy.
A Cold-Chain Cyberattack Can Become a Temperature Problem Before It Becomes an IT One
CISA's cold-chain warning shows why exposed refrigeration controls need asset inventories, isolation, supported patches and tested recovery.
OpenSSH 10.6p2 Fixes a Rare Authentication Path; Check the Build, Not Just the Version
OpenSSH 10.6p2 carries a critical workaround for some Linux builds using musl without PAM. Here is how operators should scope and verify exposure.
/* Comments */
Comments are offline right now — we reconnect automatically, nothing is lost.