
GitHub Adds API Controls for AI Scan—but Enabling It Does Not Run a Scan
New public-preview REST settings let teams govern AI Scan coverage across repositories. Policy inheritance, 422 errors and credits still shape rollout.
On this page
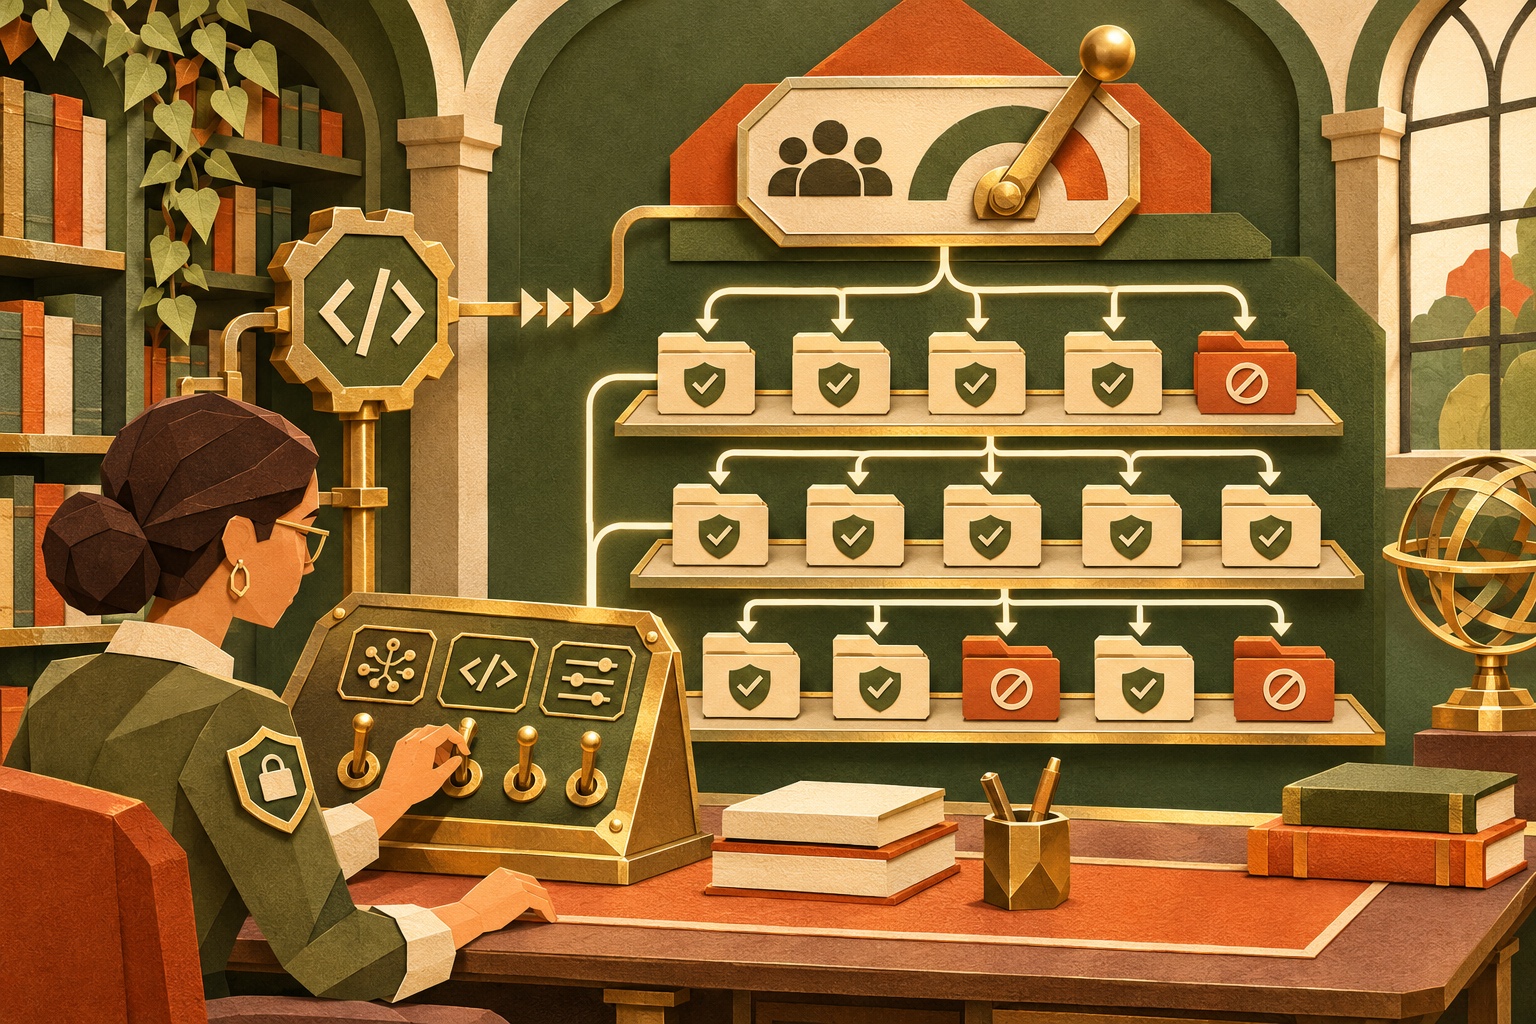
A security feature that must be toggled repository by repository is hard to govern consistently. GitHub’s November 13 public preview adds a repository_scan setting to the existing AI Scan enablement REST endpoints, so organizations can manage repository scanning through scripts and infrastructure as code. The new control answers a policy question—where the feature is enabled—not the operational question of whether a repository has been scanned. [1]
The API exposes GET and PATCH at both organization and repository paths: /orgs/{org}/code-scanning/ai-scan and /repos/{owner}/{repo}/code-scanning/ai-scan. An organization can set repository_scan to enabled or disabled; individual repositories inherit the organization setting and, when policy permits, can opt out. If the organization disables scanning, repositories cannot turn it on locally. This creates a useful hierarchy for broad rollout with controlled exceptions. [1] [2]
The endpoint can update pr_scan and repository_scan together. GitHub documents an atomic failure behavior: if either change is disallowed, the request returns HTTP 422 and neither setting changes. Automation should treat that response as a policy conflict and surface it clearly, rather than retrying or assuming partial success. Enterprise policy can prohibit enabling the setting; in that case the API rejects the change. [1]
Configuration is not execution
The distinction most likely to surprise teams: enabling AI Scan for repositories does not start a scan. Users with write access still initiate scans on demand, and each consumes GitHub Code Security AI credits. A rollout dashboard that only checks the enablement endpoint can report “covered” even when no scan has run and no result exists. Track configuration, scan execution and findings as separate states. [1]
Before applying changes at scale, build a dry-run inventory of repositories, current settings, enterprise policy and expected exceptions. Apply a small pilot, read back the setting, and then verify the scan workflow separately. Record the actor, timestamp and policy rationale for opt-outs. Reconcile changes periodically so a repository created after the rollout does not silently remain outside the intended policy.
Availability also matters. GitHub says AI Scan for repositories is available for public repositories owned by organizations and for private or internal repositories with GitHub Code Security or GitHub Advanced Security. Enterprise owners must first allow the feature. GitHub Enterprise Server is not supported. These constraints belong in deployment automation because an API call can fail for reasons of entitlement or policy, not just transient networking. [1] [3]
The feature is in public preview, so organizations should review its current behavior and API documentation before depending on it as a compliance control. The API’s value today is repeatable configuration: policy can be versioned, reviewed and reconciled instead of relying on click-by-click setup. But deterministic settings do not prove code has been analyzed, findings were triaged or vulnerabilities were fixed.
A mature rollout therefore needs two loops. The governance loop manages allowed state and exceptions. The execution loop schedules or requests scans, tracks credit consumption, records completed results and routes findings to owners. Keeping those loops distinct makes gaps visible and prevents a checkbox from standing in for a security outcome.
Does enabling repository AI Scan trigger analysis? No. Users with write access still run scans, and each scan consumes AI credits.
For related engineering context, see our guides to github actions workflow log secret scanning and rate limiting strategies token bucket sliding window. What does HTTP 422 mean here? GitHub documents it when policy blocks enablement; if either setting in a combined update is blocked, neither setting changes.
Can GitHub Enterprise Server use this preview? No. GitHub lists GitHub Enterprise Server as unsupported for this feature.
Frequently asked questions
Does enabling AI Scan start a repository scan?
No. The API changes whether repository scans are enabled by policy. A user with write access must still start a scan, and each scan consumes GitHub Code Security AI credits.
Can a repository override an organization policy?
A repository may opt out when the organization enables repository scans, but it cannot enable the feature when the organization disables it. Enterprise policy can also block enablement, producing a 422 response.
Sources & further reading
Keep reading
Replay Production Traffic Before Release—But Make Side Effects Impossible
A new AWS reference pattern replays sampled production requests against candidate code. The hard part is isolating writes and comparing the right outputs.
Cloud Pathways Keeps TPU Jobs Alive When a Slice Fails
Google Cloud’s GA Pathways runtime uses one controller across TPU slices and can reshard training after a host interruption.

Traffic Engineering at the Boundary: Load Balancers, Gateways and Reverse Proxies
How Layer 4 and Layer 7 balancers, edge API gateways, and reverse proxies coordinate to shape, authenticate, and distribute web-scale traffic.
/* Comments */
Comments are offline right now — we reconnect automatically, nothing is lost.