
Dependabot Dismissal Requests Now Stay Open for a Year
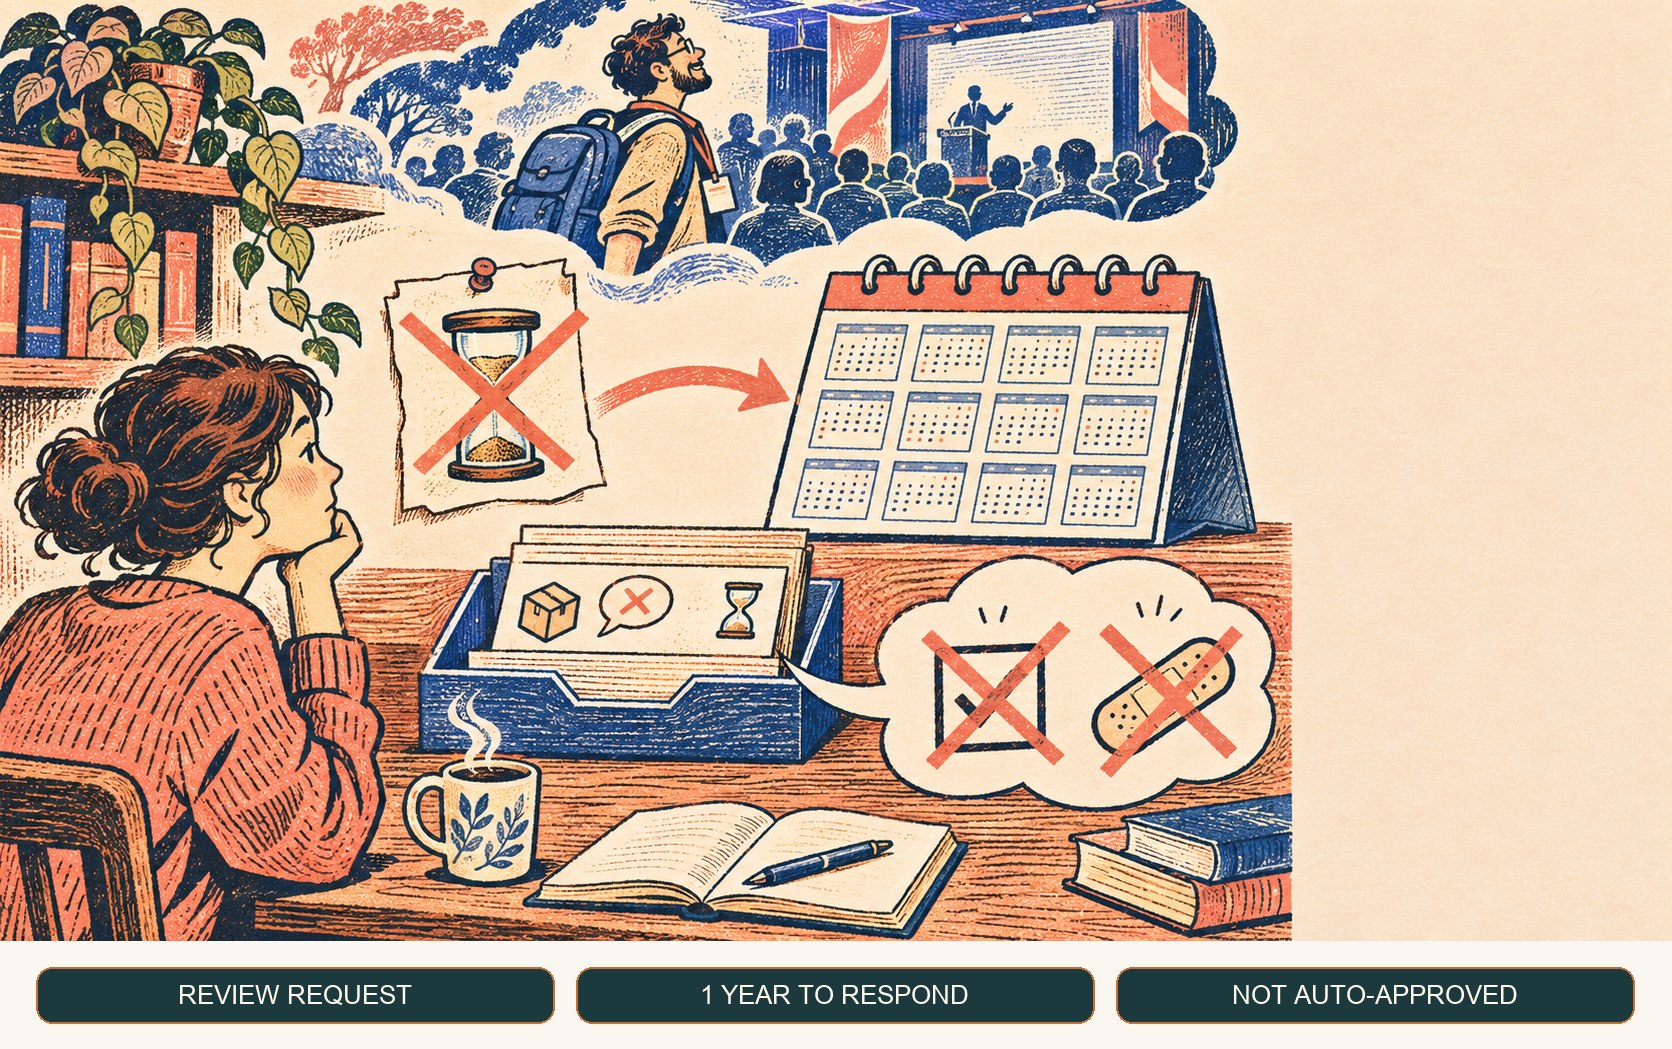
GitHub extended delegated Dependabot dismissal requests from one week to one year. The extra time helps review coverage but does not approve or fix alerts.
On this page
A vulnerability dismissal can need a second set of eyes. That review step adds governance, but it can also create a queue that expires while the right reviewer is away or working through a backlog. GitHub has extended the lifetime of delegated Dependabot dismissal requests to one year, giving organizations more time to decide without resubmitting the same request every week.
What changed
GitHub’s November 16 changelog says delegated alert dismissal requests now stay open for one year instead of one week. The change is available on github.com and is planned for GitHub Enterprise Server 3.24. The announcement describes a longer period for reviewer response; it does not change who has authority to dismiss an alert or make the request self-approving. GitHub’s announcement
Delegated dismissal lets an organization route a repository’s request to dismiss a Dependabot alert to an authorized reviewer. GitHub’s documentation names organization owners and security managers as roles that can dismiss alerts when the workflow is enabled. Repository administrators can configure it unless an organization-enforced security configuration owns that setting. GitHub’s setup guide
The extra time is particularly useful when review depends on a small security team, release calendars or evidence from the package owner. But a longer-lived queue can also conceal stale requests if nobody watches it. Our Dependabot inactive-repository explainer covers a separate policy change that makes repository activity and alert maintenance worth tracking together.
Longer expiry is not a weaker security decision
The request lifetime and the alert’s disposition are different states. The alert remains open until an authorized reviewer takes action. If a request expires, it must be resubmitted; extending the window reduces avoidable expiry, not the evidence required to dismiss a finding.
That distinction is important for false-positive handling. A dismissal should have a defensible reason, such as a confirmed non-affected version or an accepted risk with an owner and review date. A queue change cannot determine whether a package is reachable, whether a vendor fix exists, or whether a compensating control is adequate. Teams should preserve that reasoning in the request and their normal vulnerability records.
Keep the queue useful
- Assign a primary and backup reviewer. A one-year window does not replace coverage planning.
- Review pending requests on a regular cadence. A persistent request is still unresolved work; include it in the same workflow as open vulnerabilities.
- Require evidence and a reason. Ask for the package, affected range, exploitability context, proposed disposition and an owner.
- Recheck long-running requests. Package versions and fixes can change while a request waits. Reassess the finding before approving a stale rationale.
- Measure age, not just expiry. A request that is valid for twelve months can still represent an operational backlog that needs attention.
What organizations should check
The feature’s exact configuration and role behavior depend on repository and organization settings. Confirm whether delegated dismissal is enabled, whether an enforced security configuration controls it, and which people can act on the request. GitHub’s delegated alert dismissal documentation describes the model.
The update is a small workflow adjustment with a clear tradeoff: fewer requests expire before a reviewer can respond, while older pending items remain visible for longer. Keep the human decision explicit, track unresolved requests as work, and avoid treating a longer timer as vulnerability remediation.
Frequently asked questions
Does a Dependabot dismissal request close the alert automatically after a year?
No. GitHub says the request remains open for one year instead of one week so a reviewer has longer to respond. It still requires an authorized reviewer to dismiss the alert, and the request must be resubmitted if it expires.
Who can approve delegated Dependabot dismissals?
GitHub's documentation says organization owners and security managers can dismiss alerts when delegated dismissal is enabled. Repository administrators may enable the feature unless an organization-enforced security configuration controls it.
Sources & further reading
Keep reading
Windows Warns Some Secure Boot Updates May Add One Restart
Microsoft says a limited number of devices may restart once more during Secure Boot updates. Plan without mistaking the extra restart for a failure.
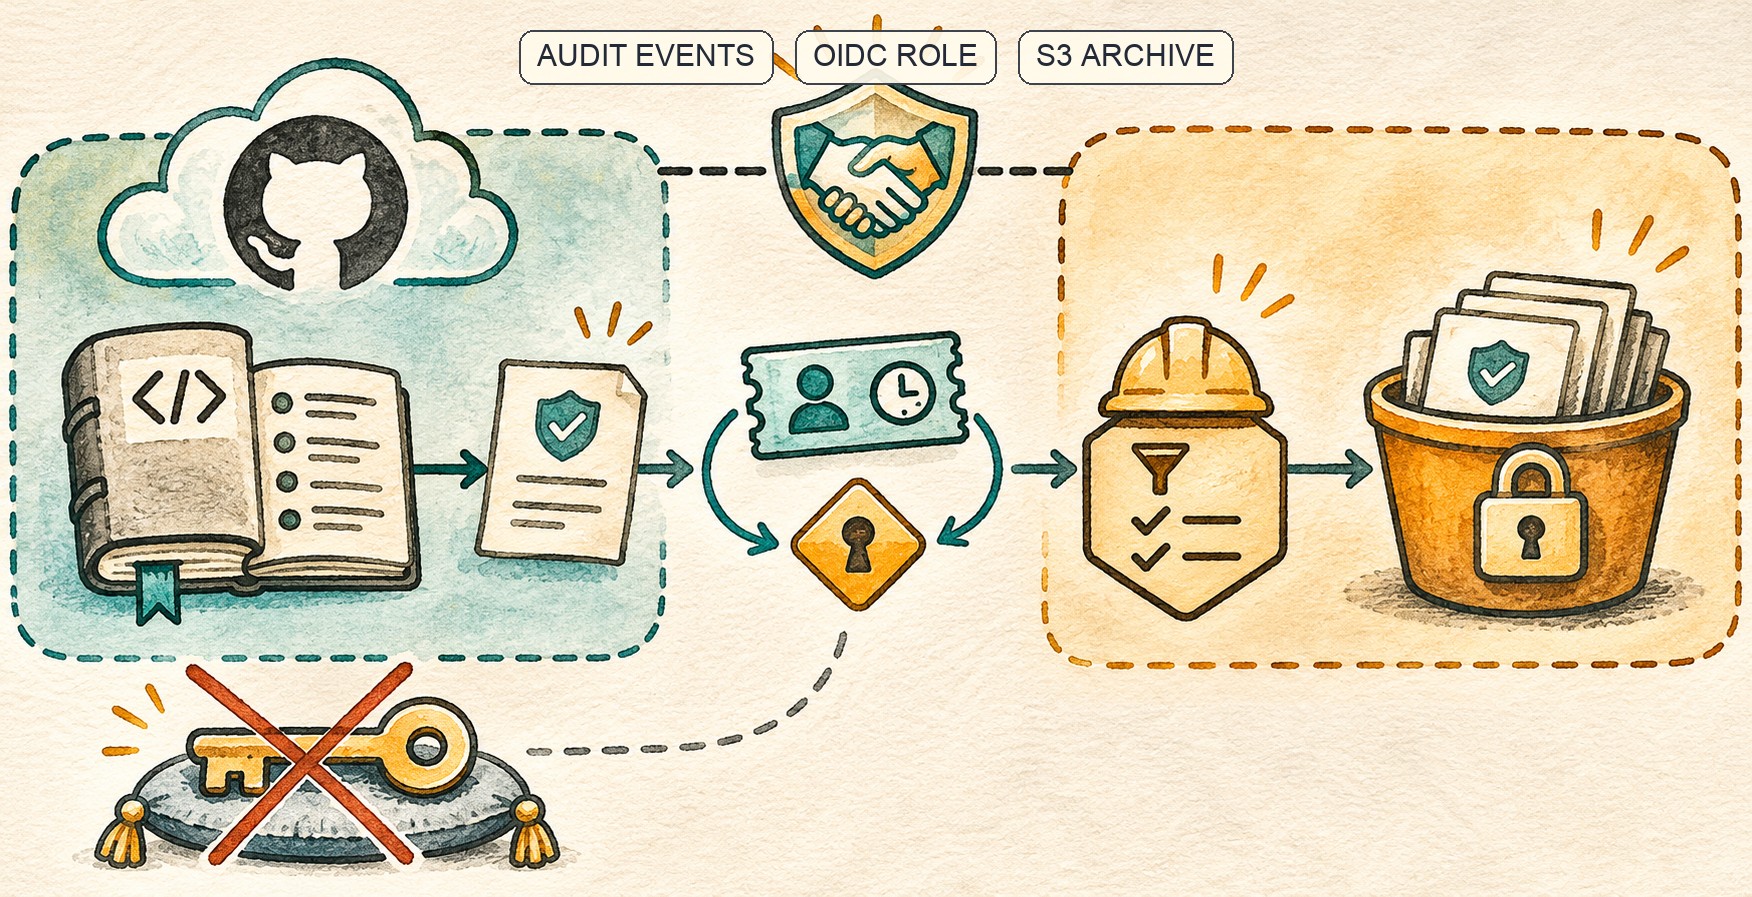
GitHub Audit Logs Reach GHE.com’s S3 Stream Through OIDC
GitHub extended OIDC-based S3 audit-log streaming to GHE.com. Short-lived role access removes stored AWS keys, but trust and retention still need care.
GitHub Team’s Automatic Risk Assessments Surface Work, Not Fixes
GitHub Team now runs organization security risk assessments automatically. Understand the findings and turn them into owned remediation.
/* Comments */
Comments are offline right now — we reconnect automatically, nothing is lost.