
AWS Lets Coding Agents Start Account Setup. The Approval Boundary Still Matters
AWS account setup now fits coding agents, but people must still review identity, permissions, cost, and deployment.
On this page
The first cloud deployment has always involved an awkward handoff: an agent can write the application, but the developer must leave the editor, create an account, set up access and return with credentials. AWS is trying to shorten that path. Its November 17 announcement says agentic coding harnesses can open the new AWS sign-up experience, complete the browser-based flow and return short-lived credentials to the harness. AWS says the first project starts with a home Region and an IAM role manager. [1]
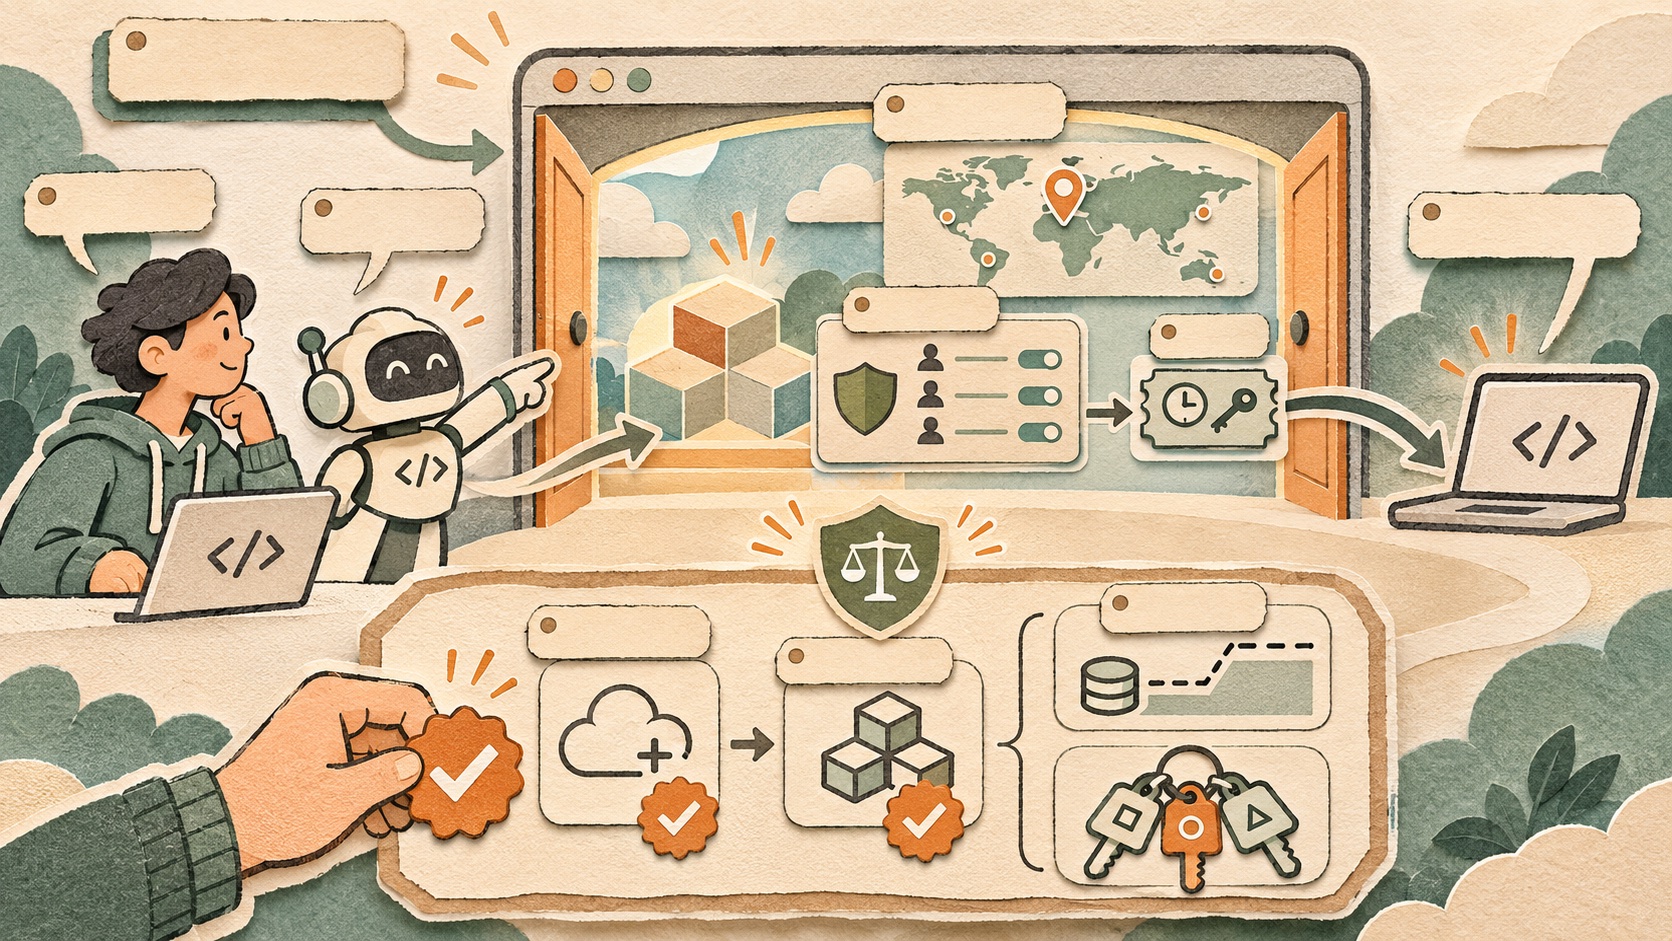
What changed in the setup path
The announcement addresses onboarding friction, not the underlying cloud permission model. AWS says a supported harness can open the sign-up experience for a developer who does not yet have an AWS account. The new experience then provides the first project’s region and role-management setup, with short-term credentials that refresh automatically. AWS lists its Agent Toolkit plugin or configuring the toolkit as ways to try the path. [1]
The distinction matters because “the agent can start deploying” can sound like an agent receives unrestricted account authority. The announcement does not say that. It describes a route into AWS’s new account experience and credentials that are temporary. The account still has an owner, a selected Region, identities and permissions, and the human remains responsible for the actions taken in the project.
AWS’s account documentation also describes signing up through a browser and receiving credentials through AWS CLI flows. It explains that credentials from the new sign-up path are temporary and can be refreshed, avoiding the creation of conventional long-lived access keys for this local-development path. The exact command and prerequisites depend on which entry point is used; check the current documentation and toolkit version before relying on a particular interaction. [2]
Short-lived credentials help, but they do not answer every security question
A credential’s lifetime is only one part of its risk. A short-lived token with broad permissions can still make consequential changes while valid. An agent that can invoke deployment tools may create billable resources, expose a public endpoint or alter infrastructure. Expiration limits the window; it does not decide what should be allowed in that window.
Teams should identify the AWS principal represented by the credentials, inspect the permissions available to it, and make the agent ask before account-level or externally visible changes. Separate discovery and code generation from deployment where possible. Use scoped roles, account budgets and service controls that match the project. Do not paste credentials into prompts, logs or repository files; use the supported local credential mechanism and verify how each harness stores it.
The Agent Toolkit quick start reinforces that documentation discovery can work without AWS credentials, while tools that execute AWS API calls or scripts require credentials. That is a useful boundary for setup: let the agent research and explain options before granting it the ability to mutate a cloud account. [3]
A safer first deployment checklist
Before trying an agent-led setup, decide which person or organization should own the account and which Region is appropriate. Confirm the account’s billing and identity requirements in the official signup flow. Once connected, inspect the available role and credential setup rather than assuming the toolkit has selected least privilege automatically.
For the first project, ask the agent to plan resources and explain expected permissions before it executes deployment commands. Review the plan, use the narrowest role that supports the task, and require a human checkpoint before creating public networking, persistent data stores or paid capacity. Afterward, review the account activity and clean up resources that were only needed for a trial.
These steps are practical controls, not claims about special AWS defaults. AWS’s announcement does not specify a universal spending cap or permission boundary for every project, and account setup can vary with existing AWS identities and region availability. Treat the product announcement as a new onboarding route, then verify the live console and role configuration for the account you actually use.
What the feature does not solve
Agent-led signup does not choose an application’s architecture, validate its threat model or guarantee that code is production-ready. It shortens the transition between an idea and a first cloud environment. That makes a clear approval boundary more important: the easier it becomes to start deploying, the more deliberately teams should define who approves account creation, credential scope, resource creation and public exposure.
Developers who already have AWS accounts may not need the new signup path at all. The Agent Toolkit can be installed separately, and its documentation distinguishes discovery functions from API execution. Teams designing the runtime side of those systems may also find AWS Step Functions agent-tool patterns useful, though that is a separate orchestration concern. Existing teams should preserve their normal identity federation, account separation and deployment approvals instead of treating a convenience flow as a reason to replace them.
The useful measure is not whether an agent can get to a cloud console faster. It is whether the setup removes repetitive administration while keeping identity, cost and deployment decisions visible. AWS has announced the bridge; teams still design the guardrails on either side of it.
Frequently asked questions
Can an AI coding agent create an AWS account without a person?
AWS describes a browser-based sign-up journey initiated by an agent, but a developer still completes account setup in the browser. The feature reduces context switching; it does not remove the human sign-up step or the need to review what the agent does afterward.
Does the new AWS flow use long-lived access keys?
AWS says the new experience returns short-term credentials that refresh automatically. That is different from creating a permanent IAM access key, but teams still need to understand where credentials are stored and what identity and permissions they represent.
Sources & further reading
Keep reading
Cloud Armor’s CDN Edge Rules Can Filter Before Cached Content Is Served
A November Preview adds ASN, threat-intelligence and HTTP filtering to Cloud Armor edge policies for Cloud CDN. The cache boundary changes where policy applies.
Cloudflare vs AWS and Azure: Compare Execution Boundaries, Not Labels
A grounded comparison of edge Workers, regional cloud functions and CDN paths—focused on runtime, networking, state, operations and workload fit.
Chrome DevTools Gives Coding Agents More Context, With Larger Trace Costs
Chrome adds paginated CSS inspection and chunked traces for agents. Learn to use the extra browser evidence safely.
/* Comments */
Comments are offline right now — we reconnect automatically, nothing is lost.